PFG SMS Verification API: Quick Integration Guide
Quick answer: To verify PFG with a virtual number, choose a country on PvaPins from $0.12, enter that number as your PFG phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
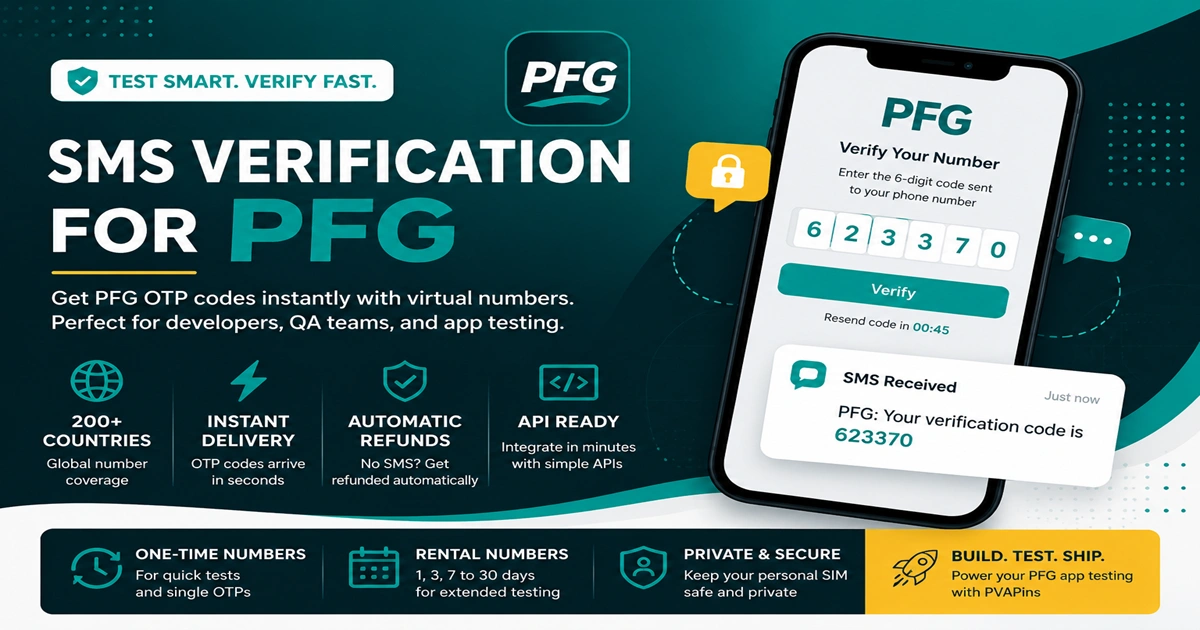
How it works
- Grab your API token from your PVAPins dashboard; no separate activation step required.
- Request a number via the API with the app short name for PFG and your target country to get an order_id.
- Poll the check endpoint with your order_id every 10–12 seconds until the status flips to sms_received.
- Use the code from the sms field in your test flow, then let the session expire or release the number. For manual tests, log into the dashboard instead, pick a country, and the OTP appears with no refresh needed.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
- Match the country you select; most test triggers are easiest when the virtual number's country matches the region you're testing.
- If a country flags the number (e.g., as VoIP), try a different region or a mobile-type number for better delivery rates.
- Watch for non-standard formats if an app rejects the number; double-check the prefix and any required international notation; use the number exactly as provided in the API response.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about PFG SMS verification.
Is it legal to use a temporary number for PFG SMS verification?
Yes, in most jurisdictions, using a temporary virtual number for privacy and testing purposes is legal. However, you must not use it to commit fraud, circumvent bans, or violate the PFG app's Terms of Service. Always test within the app's guidelines and your local regulations.
Why isn't my PFG verification code arriving?
The most common reasons are that the app flagged the number as a VoIP or known virtual line, the code was sent to a previous number (if you re-logged in), or you requested a new code too soon after the last one expired. Check the status field in your PVAPins dashboard; if it reads NO_CODE, try pressing "Resend" in the PFG app or request a fresh number.
What's the difference between a one-time number and a 7-day rental for testing?
A one-time number works for a single OTP verification event: use it, get the code, and the session expires. A 7-day rental keeps the same number active for a full week, which is useful when you need to receive multiple codes on the same number (like re-verification after session timeouts or multi-step flows). Use one-time for quick smoke tests; use rentals for sustained QA cycles.
What should I NOT use a temporary verification number for?
Do not use virtual numbers for banking OTPs, high-security financial verification, bypassing permanent bans, or creating multiple fraudulent accounts on any platform. These numbers are meant for privacy, testing, and legitimate account creation, not for evasion or abuse.
I'm getting a "this number has already been used" error in the PFG app. What now?
The app has seen this number recently, likely from a previous test or because the number pool reuses some prefixes. Grab a new virtual number from PVAPins, ideally from a different country, and restart the app flow. This usually resolves the error immediately.
Can I use the PVAPins API in a CI/CD pipeline for automated testing?
Yes. The API is designed for exactly that. You can request a number, capture the order_id, poll for the code, and feed it into your automated UI tests all within a GitHub Action, Jenkins job, or any CI runner that can make HTTP requests. Many development teams use this pattern to smoke-test verification flows on every pull request.
Does PVAPins charge me if the verification code never arrives?
No. If the session expires without a code being delivered (status NO_CODE), PVAPins automatically refunds that transaction. You pay only for successful verifications where the code arrives and is retrievable through the dashboard or API.
Will the PFG app know I'm using a virtual number?
It depends on the app's detection methods. Some apps flag known VoIP or virtual number ranges and refuse to send codes. If you encounter this, try a number from a different country or a mobile-type number (as opposed to VoIP). PVAPins provides varied number types across 200+ countries, which improves delivery rates compared to single-country, single-type services.
Read more: Full PFG SMS guide
Open the full guide
Let's be honest: if you're building or testing app flows that need phone verification, you've probably burned through your personal number more times than you can count. You get rate-limited, the codes stop coming, and suddenly your QA pipeline grinds to a halt. That's exactly where a virtual number for SMS verification PFG comes in. This guide is for developers, QA engineers, and product testers who need to verify PFG OTP flows reliably without tying their real SIM to every test run. We'll walk through the fastest way to grab a virtual number, hook into the API, and handle the edge cases that make verification testing painful. And yes, we'll show you real code patterns, not just theory.
Quick Answer:
A virtual number for SMS verification, PFG lets you receive OTP codes without using your personal phone, ideal for testing sign-up flows, password resets, and 2FA scenarios.
The PVAPins API has three core endpoints: request a number, poll for the code, and retrieve the SMS content. Integration takes about 5 minutes.
Codes arrive in the dashboard instantly and via API polling; if no SMS is received within the window, PVAPins automatically refunds that transaction.
Use one-time numbers for manual spot checks and 1–7 day rentals when you need the same number across multiple test cycles.
Never use virtual numbers for production account verification or to bypass bans; stick to QA environments and legitimate test workflows.
Why SMS Verification PFG Matters for App Testing and Where It Gets Tricky
Mobile apps lean on phone verification as a trust anchor; it's how they confirm you're a real human, not a bot spinning up fake accounts. PFG's OTP flow sits right at the center of that logic. During testing, though, that same flow can become a bottleneck. The core problem: your personal SIM is a finite resource for testing. Try verifying the same number across 50 test runs, and you'll hit rate limits or get outright blocked. Worse, your number lands in an SMS list somewhere, and suddenly you're getting marketing texts from apps you barely remember testing. Using a dedicated temporary phone number for PFG SMS verification keeps your personal line clean and your test pipeline predictable. You get a fresh number for every session, codes arrive in real time, and you never worry about "code already used" errors derailing a test suite. The isolation matters more than most developers realize. When your test environment shares a number with production monitoring or your own 2FA setup, you introduce variables that are impossible to debug. A test bench with its own number supply is cleaner, faster, and less frustrating.
Validating sign-up and registration flows during sprint QA
Simulating password reset paths across multiple test accounts
Testing international number coverage without physical SIMs
Running automated smoke tests in CI/CD pipelines
For production account recovery on real user accounts
To bypass permanent bans or create fraudulent accounts
For any test that violates the target app's Terms of Service
How to Integrate SMS Verification PFG API into Your App: A 5-Minute Developer Walkthrough
The integration flow is surprisingly lean. You don't need OAuth dances, webhook infrastructure, or a queue worker set up locally. The whole thing runs on three HTTP calls, and you can copy-paste from the docs and start receiving codes in under five minutes. Here's the exact sequence:
Grab your API token from the PVAPins dashboard. It's generated the moment you sign up; no separate purchase or activation step required.
Request a number by POSTing to the number request endpoint with the app shortname for PFG and your target country.
Poll for the code using the order_id returned in step 2. Check the status field; once it flips to sms_received, the code is in the sms field.
Use the code in your test flow, then let the session expire or manually release the number.
The entire cycle is stateless on your side. You don't manage number pools, you don't worry about cleanup, and the API response times run in milliseconds. For a quick headless start, the public API docs include cURL examples you can paste directly into a terminal. If you need a number fast without touching the API, you can also receive SMS online through the web dashboard- same delivery speed, zero setup. A common question: do you need webhooks? Not really. Webhooks are great for production systems, but for testing, polling gives you cleaner control over timing and easier debug logging. You decide when to check, and you never miss a delivery because a webhook endpoint was down during a CI run.
PFG OTP Verification API: Key Endpoints and Polling Logic Developers Should Know
The API surface is intentionally small, but understanding the status transitions is what separates smooth integrations from fragile ones. Core endpoints you'll use every time:
GET /request/sms/ request a number. Send app, country, and provider parameters; get back an id, number, cost, and initial status.
GET /request/check/sms/ poll for the code. Pass the order_id (same as the id from the request). The response carries the sms text and a status field that tells you where things stand.
GET /request/list/ review active and past orders; helpful for correlating test runs in team dashboards.
WAITING: the number is active, but no SMS has arrived yet. Keep polling.
SMS_SENT: the code has been delivered to the virtual number; the sms field contains the extracted OTP.
NO_SMS: the window expired without a code. This is a soft failure; you can retry with a new number, and PVAPins refunds this transaction automatically.
NO_CODE specifically indicates the code payload couldn't be parsed from the SMS. Treat this like NO_SMS.
Polling logic that won't hammer the API: Space your polls 10–12 seconds apart. Anything tighter risks rate limiting without meaningfully faster code delivery. Most PFG OTPs arrive within 30 seconds, so your script will typically make 2–3 polls before getting the code. Time out your polling loop at 5–10 minutes, and always code the NO_CODE path as a retry trigger rather than a hard failure. For the full parameter reference and response schema, check the full API Integration docs; every field is documented with example responses.
How to Receive PFG SMS via API: From Payment to Incoming Code
Here's the real-time flow, step by step, because seeing the actual sequence matters more than abstract descriptions. Request the number. You submit your request via API or dashboard. The number is allocated instantly; there's no manual provisioning delay. On the dashboard, the interface updates immediately; via API, the response includes the full number and country details. Trigger the OTP from PFG Head to the PFG app, enter the virtual number in the verification field, and hit the button that sends the code. This step is on the app side, not the API. Poll and retrieve. Start polling the check endpoint every 10–20 seconds. When the status field reads sms_received, the sms field contains the 4–6 digit code (or full SMS text, depending on the app). No manual refresh is required; the API response reflects delivery in real time. Use and release. Copy the code, complete your test flow, and move on. The number session expires after the usage window, or you can release it early through the dashboard. If no sms text appears in the API response and the status stays WAITING, the code hasn't arrived yet. Don't retry the same number. If the status eventually lands on NO_CODE, PVAPins refunds that transaction automatically. Contact support. Want to see it in action? Grab a number now and run a real PFG test in under 30 seconds.
PFG App Test OTP SMS: The Quick-Start Guide for QA Engineers
Manual QA testers don't always need the API, and that's fine. The dashboard path is fast enough for most ad-hoc verification checks.
Log into your PVAPins dashboard and click "Get a number."
Select your target country and match it to the region you're testing.
Copy the displayed virtual number.
Paste it into the PFG app's phone field (sign-up, login, or Forgot Password flow).
Wait for the app to trigger the SMS, then come back to the dashboard.
The OTP appears in your session automatically; no refresh needed.
Use the Forgot Password flow for a reliable, always-available SMS trigger; it's less prone to app-side caching weirdness than the sign-up path.
If you find that a number type (mobile vs. VoIP vs. DID) affects delivery rates for certain apps, note the number_id from the API response and correlate it with your test reports. Over time, you'll notice patterns.
For manual test runs, one-time numbers are usually sufficient. But if you're testing a flow that requires the same number across a session (say, re-verification after a timeout), consider a rental.
How to Use SMS Verification PFG for Development vs. Production: Knowing the Difference
This is one of those distinctions that developers nod along to in principle and then accidentally violate late on a Friday deployment. Let's make it concrete. Development and QA environments: Virtual numbers are ideal here. You're testing flows, not real user accounts. You need repeatable verification cycles without polluting production data. PVAPins is built for exactly this use case. Production environments: Don't use virtual numbers for production account verification. Most apps' Terms of Service prohibit it, and more importantly, you're introducing a point of failure that real users shouldn't depend on. Production verification should use the real phone infrastructure that your users actually have access to. What about load testing? For repeat load tests, the PFG SMS rental numbers (1-day, 3-day, 7-day plans) give you a stable number across test runs without the overhead of provisioning a new one each time. This is especially useful when you're testing rate-limit behaviors or session persistence over hours. The rule of thumb: if real user data is involved, don't use a virtual number. If it's a sandbox, a staging environment, or a CI pipeline, you're in the right place.
Troubleshooting: Why PFG Verification Codes Fail and How to Fix It
Most OTP failures come down to three things: the code never arrived, the number got flagged, or the app's resend logic conflicts with your polling window. Here's how to diagnose and fix each one. Code never shows up. Check the PVAPins dashboard first. If the status reads NO_CODE, the SMS was never delivered to that number. Press "Resend" in the PFG app; this usually generates a fresh SMS within the same session. If the status stays WAITING for more than 5 minutes, the number might be blocked; try a different country or number type. App says "number already used." The app has seen this number recently from another test or session. Grab a new virtual number (a different country often bypasses this) and restart the app flow. Most times, this resolves in under 30 seconds. Code expired before you could use it. OTP codes have short expiry windows- sometimes 10 minutes, sometimes as little as 2 minutes. The app controls this, not the virtual number provider. If your polling script is checking every 30+ seconds, you might miss the window. Tighten your poll interval and always code for the code_received status before assuming you've missed it. The API returns code_received, but your UI shows no code. Race condition. Your script parsed the code before the UI updated. Add a small delay (500ms) and re-check the sms fieldor log both states in your debug output for correlation. If NO_CODE keeps popping up, try a different country or our premium number options. Refunds are automatic when no code arrives. Check available services → or review country pricing
PFG Verification API Testing Use Case: A Real-World Example from Start to Finish
Let's walk through an actual test scenario, complete with API calls and the responses you'd see. This is the pattern QA teams use to automate PFG verification in CI. Test a new user sign-up flow where PFG sends a 6-digit OTP to the phone number entered in the registration form. Request a UK number for PFG. Your script sends a request to the API with country=GB and app=pfg. The response includes order_id: 423 and a +44 number. Feed the number into the app's UI. Your test automation (Selenium, Cypress, Playwright, whatever) enters the number in the phone field and clicks "Send Code." Poll with the order ID. Your script hits the check endpoint with order_id=423 every 10 seconds. After two polls, the status field reads sms_received, and the sms field shows 623370. Complete the verification. The automation enters 623370 in the OTP input, submits the form, and asserts the success state (redirect to dashboard, welcome message, whatever defines "passed"). Log and move on. The order_id is logged alongside the test result for traceability. If the flow fails at step 3 and the status goes to NO_CODE, the script retries with a new number and logs the first attempt for later review. This entire loop runs in under 90 seconds, is fully headless, and integrates into GitHub Actions or Jenkins without any external dependencies beyond HTTP requests.
How to Integrate SMS Verification PFG into Your App Without Hurting User Privacy
Privacy in SMS verification testing is a two-sided concern: your own test data, and the hypothetical user data you're simulating. On the test side: PVAPins never stores your outbound messages (because the platform only receives SMS; it doesn't send them). API tokens are encrypted, and one-time numbers aren't linked to any persistent identity. When you use a disposable number for a single OTP, the session is ephemeral; no long-term record ties that number to your team or your tests. On the app side: The app never sees your real SIM. It sees a virtual number that exists solely for that verification event. If the app adds that number to a marketing list, it goes nowhere after the session expires. Best practices for privacy-conscious testing:
One-time numbers for sign-up tests: Lowest risk of data leakage. The number dies after the OTP, so even if the app stores it, there's nothing to link back to.
Rental numbers for session-based tests: When you need the same number across multiple verifications (e.g., re-verification after a password change), a 1-day or 7-day rental keeps the session alive without involving your personal line. PFG SMS rental numbers are available for exactly this.
Never use real user PII in test flows: Even with a virtual number, don't plug real names, emails, or other identifiers into test accounts. Keep everything synthetic.
According to the OWASP Mobile Security Testing Guide, test environments should be isolated from production data and credentials; virtual numbers for SMS verification fit squarely within that guidance by keeping test identity separate from personal and production identity.
How to Use SMS Verification PFG for Development vs. Production: Best Practices for QA Test SMS Verification PFG
We've covered the dev/prod split already, but specific practices make the difference between a flaky test suite and one that runs cleanly every sprint. For more guides, read our blog for tips.
Assign a unique order_id to every test case and log it with your test results. When a failure happens, you can trace exactly which number was used, what status it returned, and what the code was (if any arrived).
Build a small matrix of countries you test against, especially regions where OTP delivery is historically slower. If your app serves users in Indonesia, Brazil, or Nigeria, test those routes specifically. PVAPins covers 200+ countries, so coverage isn't the bottleneck; delivery variability by region is what you're measuring.
Treat NO_CODE as a retry, not a test failure. Your test script should request a new number and retry once before flagging the test. Most NO_CODE events are transient.
Use 1-day or 7-day rental numbers for long-running tests where the same number needs to receive multiple OTPs across hours or days.
Don't reuse the same virtual number across different PFG accounts in the same test session. The app's anti-abuse systems will flag it.
Don't call the API at sub-second intervals hoping for faster delivery. It won't help, and it risks rate limiting.
Don't skip logging the API response status. When a test fails silently, the only way to debug it is by knowing whether the status was WAITING, NO_SMS, or something else entirely.
a test suite that catches real bugs (wrong OTP format, broken redirect after verification, timeout handling) without failing on infrastructure issues that are outside your control. Virtual numbers make that possible, but only if your test logic accounts for the same status transitions the API does.
Key Takeaways
SMS verification PFG testing is faster, cleaner, and more reliable when you isolate it from personal phone numbers.
Integration takes three API calls and fits into any CI pipeline with standard HTTP libraries- no special infrastructure needed.
Poll every 10–12 seconds, code for every status value (especially NO_CODE), and always log order_id with test results.
Never use virtual numbers for production verification, but lean on them heavily for QA, staging, and automated smoke tests.
Privacy is maintained on both sides: the app sees a single-use number, and your personal SIM stays off marketing lists.
If a code doesn't arrive, PVAPins automatically refunds that transaction, no manual intervention required.
For extended test sessions, rental numbers (1, 3, 7, up to 30 days) provide a stable number without reprovisioning.
Compliance note: PVAPins is not affiliated with any app or website. Please follow each app's terms and local regulations.
Last updated:
Ready to Keep Your Number Private in PFG?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Daniel Marsh
Daniel Marsh is a software developer and technical writer with 8 years of experience in API integrations, backend automation, and online identity verification systems. At PVAPins.com, Daniel focuses on the technical side of virtual phone numbers — covering topics like SMS verification APIs, bulk number management, programmatic account setup, and integrating virtual numbers into development workflows.
Daniel has worked as a backend developer for multiple SaaS startups, where he regularly built and maintained phone verification systems for user onboarding and 2FA. That first-hand development experience gives him a uniquely practical perspective: he writes for developers, DevOps engineers, and technical teams who need more than just a surface-level overview of how virtual numbers work.
His guides at PVAPins go beyond the basics — diving into rate limits, number recycling, country-specific verification quirks, and how to select the right virtual number service for production environments. Every piece he publishes is informed by real testing and code-level experience, not just documentation review.
Outside of writing, Daniel contributes to open-source privacy tools, follows developments in GSMA and telecom regulation, and enjoys helping other developers navigate the often-underdocumented world of SMS verification at scale. His core belief: if a verification workflow is painful to set up, it's probably not designed for real-world use — and it's his job to help developers find what actually works.