PCA SMS Verification: Protect Your Number Instantly
Quick answer: To verify PCA with a virtual number, choose a country on PvaPins from $0.12, enter that number as your PCA phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
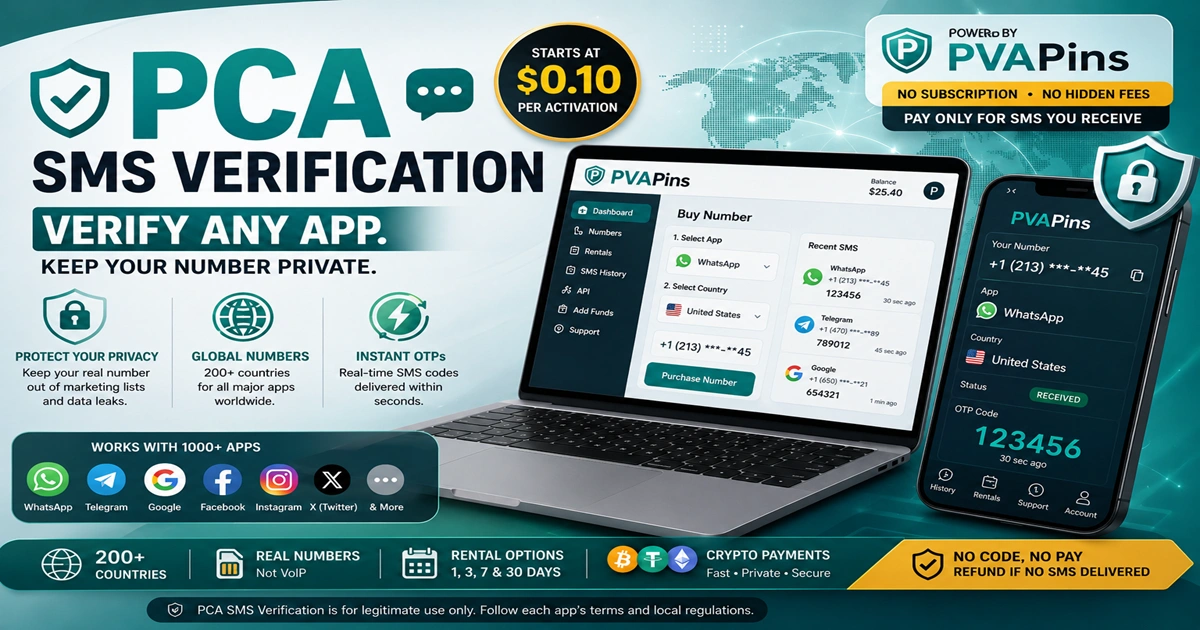
How it works
- Choose a number Select a temporary or rental number that supports your country and service.
- Copy the full number Include the international country code when you enter it in the app.
- Request the OTP Enter the number in the service's verification field and request an SMS code.
- Receive the code The SMS appears in your provider dashboard when delivered.
- Enter the OTP Copy the verification code into the app to complete the supported verification process.
- Keep or discard the number Use a rental number when you need continued access, or let a temporary number expire after one-time use.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
- Always enter the complete international phone number, including the country code.
- US: +1XXXXXXXXXX
- UK: +44XXXXXXXXXX
- India: +91XXXXXXXXXX
- Use the country format accepted by the target service and avoid adding an extra leading zero after the country code.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about PCA SMS verification.
Is PCA SMS verification safe?
Yes, when you use a legitimate provider. The number is temporary and not linked to your identity, so spam and SIM-swap risks drop significantly. Just make sure you're not violating any app's terms of service.
Why did my PCA verification code never arrive?
Usually it's because the app already flagged the provider's number, or the app doesn't support the country you picked. Try a different country or provider, and double-check that you entered the number correctly.
Can I reuse a PCA number for multiple verifications?
Often yes, but not on the same app. If you've already verified an account with that number on a service, the app may reject a second attempt. Rental numbers (1, 3, 7, or 30 days) work better for repeated OTPs.
What is the difference between a one-time PCA number and a rental PCA number?
A one-time number is for a single OTP; once used, it may expire. A rental number (1–30 days) stays active for multiple codes, which is useful for apps that send periodic verifications or for ongoing testing.
What should I NOT use PCA SMS verification for?
Never use it for fraud, spam, creating fake accounts to abuse promotions, or bypassing security bans. Also avoid using it on banking or KYC-required services where you need to provide a verified real identity.
How long does a PCA verification number stay valid?
It depends on the provider. One-time numbers are good for a single activation. Rental numbers last for 1, 3, 7, or up to 30 days before they're deactivated.
Can I get a refund if my PCA verification fails?
Reputable providers like PVAPins offer refunds if no OTP is delivered. Always check the refund policy before buying. If a provider promises delivery but doesn't follow through, you should be covered.
Read more: Full PCA SMS guide
Open the full guide
PCA SMS verification is the workaround nobody tells you about. It lets you pass those "enter your phone number" checks without ever giving away your actual digits. Think of it as a burner phone number, minus the burner phone. The whole point is simple. When an app demands SMS verification, you give it a temporary or rented number instead of your personal one. The app sends a code, you grab it from a dashboard, paste it in, and you're in. Your real SIM never enters the picture. Whether you're a privacy nerd, a developer who needs to test signup flows without burning through personal numbers, or just someone who wants to try a service for a week without committing, this guide covers the whole process.
Quick Answer:
PCA SMS verification uses a temporary or rented virtual number to receive one-time codes (OTPs) during account setup.
Your real SIM stays out of marketing databases and away from SIM-swap attackers.
From the app's perspective, it's just a normal SMS verification; it can't tell the number is disposable.
You can grab a number on PVAPins for as little as $0.10 per activation, with codes delivered in real time and no subscription required.
What Is PCA SMS Verification? (Definition & Core Concept)
At its core, PCA SMS verification means confirming your identity by receiving an OTP on a number that isn't your personal SIM. The "PCA" typically stands for "Pseudo-Code Authentication" or "Phone Code Authentication," but honestly, the acronym matters less than what it does. You're using a temporary or dedicated number solely for verification purposes, and in doing so, you're cutting the link between your real identity and whatever account you're creating. That's the privacy layer in action. The number you verify with is disposable or rented, not your primary line. The app sending the code sees a perfectly normal phone number; it has no idea that number is temporary.
PCA systems generally rely on virtual numbers from providers like PVAPins that receive SMS and show you the OTP in real time.
Because the number is temporary, you can toss it after verification- goodbye spam exposure.
Fair warning: "PCA" isn't some formal industry standard. It's a practical label that privacy-focused verification platforms use.
The verification flow itself? Identical to standard SMS OTPs. You provide a number, the app sends a code, you type it in.
How PCA SMS Verification Works (Step-by-Step Process)
If you've done standard SMS verification, you already know 90% of this. The difference is where the number comes from: a temporary or rental service instead of your phone's SIM tray. You pick a virtual number from a provider, plug it into whatever app wants verification, and then watch for the OTP in your provider's dashboard. Paste that code into the app, and boom. Verification complete. Your personal number never even broke a sweat.
Step 1: Buy or rent a virtual number through an SMS verification platform like PVAPins. Match the country and app to your needs.
Step 2: Enter that number into the signup or verification field of the target app- WhatsApp, Telegram, Google, whatever.
Step 3: The app fires off an OTP via SMS to that virtual number through standard carrier routing.
Step 4: Your provider catches the incoming SMS and displays the code in your account dashboard.
Step 5: Type the code back into the app to confirm you own the number. That's it.
Why PCA SMS Verification Exists: The Security Problem It Solves
Traditional SMS verification creates something most people don't think about: a permanent link between your personal number and every service you've ever signed up for. That link sits in databases, gets sold to data brokers, and occasionally leaks. PCA SMS verification exists to snap that link. You use a temporary or rented number that can't be traced back to you, and the whole mess disappears. This matters most when it comes to SIM-swap attacks- those nasty exploits where an attacker hijacks your personal number to bypass two-factor authentication on your other accounts. CISA has a whole breakdown of how these attacks work and why separating your number from your accounts is critical. SIM-swap attacks: With a PCA number, there's nothing to hijack. The number is disposable, so even if it's compromised, the damage is contained.
Without PCA, every verification you complete becomes a data point that can be sold or leaked, and we've all seen how often that happens.
SIM-swap attacks go after personal numbers; PCA numbers aren't linked to your identity, so there's no leverage.
Developers testing SMS flows use PCA to keep their personal inboxes from filling up with test codes.
Privacy regulations like GDPR push for data minimization; PCA fits that principle by limiting personal data exposure from the start.
Key Benefits of PCA SMS Verification for Privacy & Account Security
The main draws are straightforward: privacy, control, and a smaller attack surface. You never hand over your real SIM number, which means it can't be used to reset passwords on your other accounts if a SIM-swap attempt happens. And since you can reuse or discard PCA numbers whenever you want, a compromised verification number doesn't haunt you for years. For businesses, it's a different flavor of win. QA teams can test SMS flows across multiple countries without buying a single physical SIM. And the GDPR minimization principle backs this up: you should only collect data you actually need, and PCA helps you avoid collecting your own phone number in the first place. GDPR minimization principle
Keeps your personal number out of marketing lists and third-party data aggregators.
Reduces targeted phishing calls or texts aimed at your real line.
Gives you temporary access for service trials without a long-term commitment; you can use rental numbers for 1, 3, 7, or even 30 days.
Supports multi-region testing for developers: spin up a US number for one test, a UK number for the next.
PCA SMS Verification Mechanism Explained: Behind the Scenes
Here's where it gets a little nerdy, but stick with me- it's cooler than it sounds. Under the hood, PCA SMS verification rides the same cellular infrastructure as any other SMS. The only twist is the destination: a virtual number hosted on a SIM farm or some cloud-based telephony platform. When the app sends an OTP, the carrier routes it to the virtual number's associated SIM (or software SIM). The provider's system intercepts the message, pulls out the code, and pushes it to your dashboard via WebSocket or polling. From the app's point of view, nothing looks unusual. It thinks it just verified a real user with a real number. The GSM architecture that handles this routing is defined by standards like the ETSI 3GPP spec, which lays out how messages travel from sender to receiver regardless of who owns the number. GSM architecture for SMS routing
The virtual number sits in a real mobile network operator (MNO) range, so the app treats it like any other number.
Providers may use physical SIMs or GSM gateways; either way, the SMS path stays standard.
Some platforms offer a developer API so you can poll for codes programmatically without clicking around a dashboard.
If you've seen "PCA" tossed around in a fragmented context, the mechanism underneath is consistent: a temporary number routes the OTP just like any other.
When You Should Use PCA SMS Verification (Use Cases)
So when does PCA SMS verification actually make sense? Honestly, more often than you'd think. Any time you need to sign up quickly without exposing your real number, or when you need to receive multiple OTPs for testing, temporary access, or plain old privacy, this approach shines.
Signing up for geo-restricted services that demand a local number (a US number for a US-only app, for instance).
QA testing of SMS flows without dragging your personal phone into it keeps test data clean and separate.
Securing high-value accounts like crypto exchanges by using a disposable number during initial setup.
Receiving codes for services you only need for a day or a week- rental numbers are perfect for that.
Ready to try PCA SMS verification without risking your personal number? Grab a temporary number from PVAPins for as low as $0.10 per activation, no subscription, no hidden fees- just a private number and real-time OTPs. Get started now.
Step-by-Step Guide: How to Perform a PCA SMS Verification
You don't need any technical wizardry to do this. You need two things: a temporary phone number provider and the app you want to verify. Pick the country and app that match your needs, buy the number, copy it into the app's signup field, and wait for the OTP to land in your provider's inbox. Type that code back into the app, and your real SIM never touched the process. Here's the exact sequence:
Step 1: Head to PVAPins.com and pick the country and app that matches the service you're verifying.
Step 2: Complete payment; rates start around $0.10 per activation, and they accept crypto for a fast, private checkout.
Step 3: Copy the virtual number shown in your dashboard.
Step 4: Paste the number into the target app's phone number field and request the SMS code.
Step 5: Watch your PVAPins dashboard; the code shows up in real time. Type it into the app, and you're done.
Common Mistakes That Break PCA SMS Verification (And How to Avoid Them)
Most PCA verification failures come down to three things: using a number the app has already flagged as virtual, dragging your feet, or trying to verify an app in a country where the provider has zero coverage. The OTP expires, or you try to verify an app in a country where the provider has zero coverage. None of these are hard to avoid; you need to pay attention. Check our pricing page.
Mistake 1: Buying a number from a country the app doesn't serve. Always check the provider's country and app support list first.
Mistake 2: Reusing a number that was already registered on the same app; it may already be blocked.
Mistake 3: Waiting too long after payment. Some numbers become reserved, but only for a limited window.
Mistake 4: Assuming every app accepts virtual numbers. Read the app's TOS first. Some explicitly ban them.
If your PCA verification code doesn't arrive, don't panic. PVAPins offers refunds on undelivered codes, and support can help you pick a working number. Check the country list or reach out for assistance.
PCA SMS Verification vs. Standard SMS Verification What's Different?
Honestly? The only real difference is the phone number you use. Standard SMS verification means using your personal SIM- your real number, tied to your name, your address, your everything. PCA verification means using a temporary or rented virtual number that's yours for a little while but can't be traced back to you. The app can't tell the difference because the virtual number routes SMS normally. The mechanism underneath is the same.
Standard verification creates a permanent link between your identity and the service.
PCA verification creates a temporary link; the number can expire or be tossed.
Standard numbers are vulnerable to SIM-swap attacks; PCA numbers aren't tied to your identity.
Costs differ: standard verification is "free number" (you already pay your mobile bill), while PCA verification costs a small per-code fee.
Is PCA SMS Verification Legal? Safety, Compliance & What You Must Know
Here's the straight answer: PCA SMS verification itself is legal in most places. You're just receiving an SMS at a number you control. But here's the catch: you must comply with each app's terms of service and any local regulations that apply. Using a temporary number to violate an app's terms (like creating a pile of fraudulent accounts) is not legal, and reputable providers won't help you with it. Always check the target app's terms regarding virtual numbers. WhatsApp's terms of service, for example, outline acceptable use cases, and some platforms explicitly forbid temporary numbers. App terms of service regarding virtual numbers
In regions with strict KYC laws, you may need a real number for financial services. PCA numbers won't cut it there.
PCA verification is safe when used for private account registration, testing, or temporary access.
Never use PCA numbers for fraud, spam, or ban evasion that violates provider terms and often the law.
Reputable providers like PVAPins are upfront about pricing and refund policies; refunds are offered if no code arrives.
Need a number that lasts longer than one OTP? Rent a virtual number for 1, 3, 7, or 30 days at PVAPins. Perfect for ongoing app verification, testing, and temporary accounts- pay only for the SMS you receive. Explore rental options.
Key Takeaways:
PCA SMS verification decouples your real identity from account signups using a temporary virtual number.
From the app's perspective, the process is identical to standard SMS verification; the number is just disposable.
It reduces risks like SIM-swapping, spam, and data leaks while keeping your personal number private.
Use it for legitimate purposes like privacy, testing, and temporary access, never for fraud or TOS violations.
PVAPins offers one-time and rental numbers with instant delivery, crypto payments, and refunds if no code arrives.
Compliance note: PVAPins is not affiliated with any app or website. Please follow each app's terms and local regulations.
Last updated:
Ready to Keep Your Number Private in PCA?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Ryan Brooks
Ryan Brooks is a tech writer and digital privacy researcher with 6 years of experience covering online security, virtual phone number services, and account verification. He joined PVAPins.com as a contributing writer after years of working independently, helping consumers and small business owners understand how to protect their digital identities without relying on personal SIM cards.
Ryan's work focuses on the practical side of online privacy — specifically how virtual numbers can be used to safely verify accounts on platforms like WhatsApp, Telegram, Facebook, Google, and hundreds of other apps. He tests these workflows regularly and writes only about what actually works in practice, not just theory.
Before transitioning to full-time writing, Ryan spent several years in IT support and network administration, which gave him a deep, first-hand understanding of the vulnerabilities that come with exposing personal phone numbers to third-party services. That background is what drives his passion for educating readers about safer alternatives.
Ryan's guides are known for being direct and jargon-free. He believes privacy tools should be accessible to everyone — not just developers or security professionals. Outside of work, he keeps tabs on data privacy legislation, follows cybersecurity research, and occasionally writes for privacy-focused communities online.