Dyin SMS Verification API: Developer Guide & Integration
Quick answer: To verify dyin with a virtual number, choose a country on PvaPins from $0.12, enter that number as your dyin phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
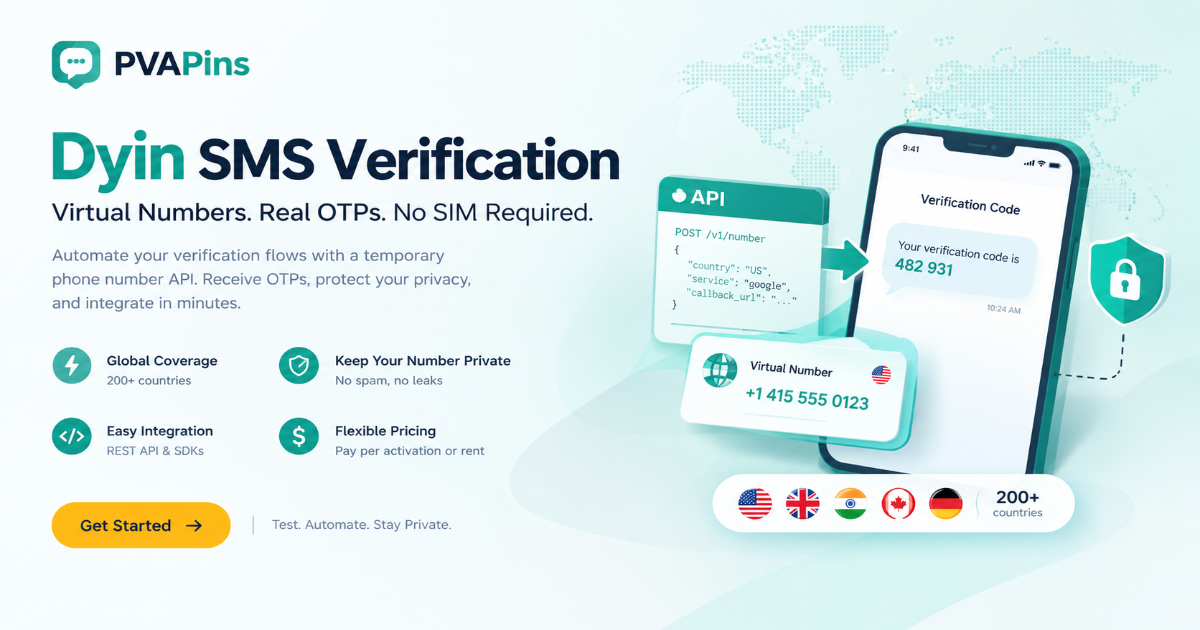
How it works
Register and get an API key. Create a developer account with a provider like PVAPins and generate a unique API key. Store it in an environment variable, not in source code.
Request a number via API. Make a POST request to the "get number" endpoint with your country and service parameters (e.g., "google" or "whatsapp") to get a temporary virtual number.
Use the number for OTP delivery. Enter the returned number in your target application so it sends its verification code there.
Retrieve the SMS. Poll the "get SMS" endpoint every 5–10 seconds, or set up a webhook to receive the code automatically.
Release the number. Free the number after use, or extend the rental window (1, 3, 7, or 30 days) if you need it for recurring OTPs.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
US numbers: Needed for US-only apps some services are sensitive to the area code, so pick accordingly.
UK & Canada: Strict telecom regulations mean quality providers are essential; expect reliable delivery for fintech and crypto exchanges.
India & Germany: High SMS-dependent user bases; occasional delivery delays are possible, but a solid provider keeps them rare.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about dyin SMS verification.
Is it legal to use a temporary SMS verification API?
Using a temporary number to receive OTPs is generally legal in most jurisdictions, as long as you're not violating a specific app's terms of service or using the numbers for fraud. Legality hinges on intent: legitimate testing, privacy, and registration are fine; abuse and spam are not. Always check both local regulations and the target app's terms before integrating.
Why do verification codes fail to arrive on some apps?
The most common reason is that the target app actively blocks virtual or VoIP numbers from receiving SMS. Some services also geo-restrict delivery, so a number from the wrong country pool won't work. A good provider will show which services it supports and offer a refund if no code is delivered.
What's the difference between a one-time number and a rented number?
A one-time number is for a single verification; it's released after the session ends. A rented number (1, 3, 7, or 30 days) stays alive for recurring OTPs, which is essential for apps that re-verify your identity on login or password resets. Choose a rental if you plan to keep using the same account.
What should I NOT use a temporary number for?
Never use temporary numbers for referral fraud, creating fake accounts to farm bonuses, spamming, or bypassing bans. These uses violate most apps' terms of service and can get the numbers banned and your provider blacklisted. Stick to legitimate privacy, testing, and QA use cases.
How do I troubleshoot when a code doesn't arrive?
First, check whether the app supports virtual numbers. Then verify that you requested the correct country pool and that the number was assigned properly. Increase your polling frequency or switch to webhooks, and check whether the SMS body contained a link instead of a code. If all else fails, request a new number.
Is the dyin SMS verification API safe to use for my development team?
Yes, when used properly. The API abstracts away the hardware, so your team never needs physical SIM cards lying around the office. It's a standard REST interface that integrates cleanly into CI/CD pipelines and test environments, keeping everyone's personal numbers private.
Read more: Full dyin SMS guide
Open the full guide
Every developer hits this wall eventually. You're building a sign-up flow, you need to test the OTP step, and suddenly you're staring at your team's personal SIM cards like they're made of gold. Nobody wants to burn through their own number or their coworkers' to see if a button works. That's where "dying SMS verification" comes in. It's not one specific product. It's shorthand you'll spot across dev forums for an entire category of tools: APIs that hand you a temporary, virtual phone number through code, then let you grab the one-time passcode (OTP) sent to it.
This guide is the technical, no-fluff walkthrough. We're covering what this API actually does, how to wire it into your stack, where the common failure points hide, and what separates a solid provider from one that'll leave you debugging at 2 AM. We're talking automation and privacy the real reasons to use this stuff, not just "grab a free number for fun."
Quick Answer
A "dying SMS verification" API lets you request a temporary virtual number via a REST call and receive OTPs sent to it, no physical SIM required.
It's built for automation: testing onboarding flows, QA regression, and keeping your real number out of marketing databases.
The typical flow is request → assign → receive SMS → retrieve code, with results usually landing within seconds or a few minutes.
Key features to evaluate: country coverage (200+ nations is a solid benchmark), refund policies for failed deliveries, and clean documentation for webhooks and polling.
You pay per activation (starting around $0.10) or rent a number for 1–30 days for recurring OTPs, often via crypto for extra privacy.
What Is the Dyin SMS Verification API?
The Dyin SMS verification API is an interface that lets developers programmatically request a temporary virtual phone number and receive one-time passcodes from apps and services, without using a personal SIM card. It's an automation tool designed for testing SMS flows, creating verified accounts for legitimate business use, and keeping your real number off marketing databases. Essentially, it turns phone verification into a simple API call.
Now, about the term itself. "Dyin" isn't an official standard or a registered trademark. It's community slang, dev-speak you'll encounter in forums and GitHub threads as shorthand for "dying" or disposable number services. But the underlying function doesn't change across providers: you get a real, SMS-capable phone number that exists virtually and responds to API control.
Here's what that actually means in practice:
The API abstracts the whole SMS reception process: request a number, wait for the SMS to land, then retrieve the code via a GET request or webhook.
Codes typically arrive within seconds to a couple of minutes, depending on the provider and the country's carrier infrastructure.
Providers like PVAPins Android app, a global SMS verification platform, offer this functionality across 200+ countries, making it a genuinely global tool.
You're not just getting a number; you're getting managed infrastructure. The provider handles the physical hardware, carrier connections, and message parsing behind the scenes.
The point is: you're not buying a phone number. You're buying an abstraction layer that makes phone verification feel like any other API call in your stack.
How Dyin SMS Verification Works: The Technical Flow
Here's the step-by-step mechanics of how this works under the hood. When you send an API request for a number, the provider reserves a real SMS-capable virtual number and returns it almost instantly. The service you're verifying, say, a banking app or a social platform, sends its OTP to that number. The provider's infrastructure captures the SMS, parses it, and exposes the code for you to retrieve via API. All of this happens in real time, and you never touch a piece of hardware.
The magic lives in the provider's backend. They maintain pools of numbers across different countries and mobile operators. When you request one, their system assigns you a number that isn't currently in use, then listens for incoming messages. Once an SMS arrives, it parses it and stores it in a temporary buffer linked to your request ID.
The flow breaks down like this:
API request → number assigned → OTP sent by target service → SMS captured by provider → code retrieved via API
A few technical details worth knowing:
Most providers hold the SMS for a limited time window, often 5–10 minutes. Polling frequency matters; if you check too late, the code's gone.
Response formats are usually JSON, which means clean parsing into any modern application: Python, Node.js, Go, you name it.
The number gets released back to the pool after the session ends, unless you're renting it for a longer window via a service like PVAPins' rental plans.
Some providers include the sender name in the response, which is helpful when you're verifying multiple services simultaneously.
The whole thing is designed so the provider's infrastructure absorbs all the carrier-level complexity. You make requests and read responses.
Dying SMS Verification API Documentation: What to Look For
Let's be honest: good API documentation is the difference between a 20-minute integration and a three-day headache. When you're evaluating a provider, open their docs first. That's your window into how seriously they take their engineering.
What you want to see:
Endpoint structure: A clear base URL, a well-defined authentication method (API key vs. OAuth), and the required content-type headers. No guesswork.
Request/response examples in multiple languages: cURL is the baseline, but Python and JavaScript examples show the provider actually thinks about developers.
Explicit error code explanations: What happens when no SMS arrives? When a number is unavailable? When the session expires? Look for HTTP status codes like 400, 404, and 429 and explanations that tell you what to do about them.
Rate limits and timeout behavior: The docs should tell you how many requests you can make per minute and what happens when you exceed them.
A sandbox or test environment: This is a huge green flag. It means the provider wants you to test before you commit real credits.
Here's the thing: a provider's documentation mirrors its production reliability. If the docs are sloppy, ambiguous, or incomplete, their infrastructure probably is too. If they define every field in the payload precisely the order ID, the number format, the status enum values- that's a provider who cares about edge cases.
Also check for:
Webhook vs. polling: The docs should clearly explain both patterns and recommend one for high-volume automation.
Quick start guide: A full end-to-end example that takes you from account creation to receiving your first SMS is a strong sign of a developer-first provider.
Rental extensions: Documentation should cover how to extend a number's life (e.g., 1-, 3-, 7-, or 30-day plans), not just one-off usage.
If the docs leave you guessing, walk away. There are better options.
Dying SMS Verification API Integration: Step-by-Step Setup
Integration follows a standard pattern: create a developer account, generate an API key, fund your balance, then call the "request number" endpoint with your country and service parameters. From there, you poll for the incoming message. Most developers are up and running within an hour; the key is structuring your code to handle the full lifecycle cleanly, from number assignment to message retrieval.
Here's a concrete walkthrough:
Step 1: Register with the provider and generate a unique API key. Store it in an environment variable, not in your source code. (Seriously, committing keys to GitHub is how breaches happen.)
Step 2: Make a POST request to the "get number" endpoint with your country and operator preferences. You'll often specify a service ID (like "google" or "whatsapp") to indicate which app you're verifying against.
Step 3: Use the returned phone number in your target application to deliver the OTP.
Step 4: Poll the "get SMS" endpoint every 5–10 seconds, or set up a webhook to receive the code automatically. The choice depends on your scale and latency tolerance.
Step 5: Release the number after use, or extend the rental window if you need it longer for re-verification.
A quick note: most providers freeze or return the number if no SMS arrives within a specified time. This prevents you from being charged for a dead session. Check your provider's policy, because it directly affects your failure costs.
Test the flow for free. Grab a public or free online phone number and run your first OTP request in under five minutes no credit card required to see how it works.
Dyin SMS Verification API for Developers: Code-Level Considerations
Beyond simple HTTP calls, serious developers need SDKs, retry logic, and robust parse handling. A solid integration treats the verification API like a microservice: handle timeouts gracefully, store order IDs, and always log the full response payload for debugging. Accessibility matters: look for official SDKs or clean REST specs you can quickly port into any language.
When you're writing the client code, think about resilience. The network is unreliable, and third-party APIs have hiccups. Your wrapper should fail gracefully without crashing your entire application.
Key considerations:
Language support: Python, Node.js, PHP. Check whether the provider offers official SDKs or if you'll write your own HTTP client. Both are fine, but official SDKs usually handle edge cases better.
Authentication best practices: Store API keys in environment variables, never in source control. Use a secret manager if you're in the cloud.
Response parsing: Know the schema for order ID, number, status, and SMS content fields. Defensive parsing is crucial: fields might be missing or null, and your code shouldn't crash when they are.
Timeout strategy: Implement exponential backoff when polling to avoid hammering the endpoint and getting rate-limited. A 5-second interval with a 60-second cap is a reasonable starting point.
Test mode: Use a public or low-cost number to validate your flow before committing real credits to a production run. It's cheap insurance.
One more thing: log everything: the full request payload, the response, the timestamp, the order ID. When something goes wrong in production, you'll need that data to diagnose the issue. Future you will be grateful.
Dying SMS Verification API for Automation: Polling, Webhooks & Retry Logic
Automation is where a verification API proves its worth. You can batch-create test accounts, automate QA regression for sign-up flows, or run scheduled jobs that check whether SMS delivery is functioning globally across different carriers. The trick is designing your automation to be fault-tolerant: not every SMS arrives on the first attempt, and your code should handle that gracefully instead of crashing. The architecture pattern you choose polling vs. webhooks depends on your scale and latency tolerance.
Polling is simpler. You make a GET request at a fixed interval and check for new messages. It works well for low-volume scripts and personal projects. The downside is wasted requests when nothing new arrives, plus the risk of missing the delivery window if your interval is too long.
Webhooks are the production-grade approach. The provider pushes a POST to your endpoint the moment an SMS arrives: no wasted polling requests, no timing risk, no rate-limit worries. You need a public HTTP endpoint; a simple Flask or Express route works fine.
Here's what solid automation looks like:
Polling intervals: Respect the provider's rate limits; typical intervals are 5–10 seconds. Don't hammer the endpoint with 1-second polls unless you're in a sandbox.
Webhooks: Push notifications when SMS arrives eliminate unnecessary polling overhead and reduce API load. Your server needs a public endpoint to receive the POST.
Retry logic: If a code fails, request a resend from the target service, or request a new number entirely. Don't loop infinitely on the same dead number; that's how you burn credits.
Multi-threading: Run parallel verifications for different services without cross-contaminating order IDs. Clean up your thread locals properly.
Built-in health checks: Monitor your integration's success/failure status to catch provider outages early. Set up alerts for a sudden spike in failures; it's usually the first sign of a problem.
The bottom line: automation is about graceful degradation. The API will fail sometimes. Your job is to make sure those failures don't cascade.
Privacy & Security: Why Use a Temporary Number API for OTPs
The core value of a temporary number API is privacy: you keep your personal SIM number out of databases that may be sold, leaked, or spammed. For developers, this also means you never expose internal staff numbers during testing or QA. It's a protective layer that prevents contamination of your personal and professional channels.
Here's how it works in practice. The virtual number is disposable. Once you're finished with it, it goes back into the pool, and any follow-up SMS marketing spam, phishing attempts, whatever goes to that dead number, not your iPhone. For QA teams, it's a massive win because no one's personal phone is tied to test accounts.
Consider what this means:
Protect your primary number from marketing lists and data brokers by routing all public sign-ups through a temporary number.
Reduce phishing risk: you don't receive follow-up spam at your real number because the virtual number is disposable.
Shield individual testers' personal numbers from automated verification flows during QA cycles.
Maintain anonymity when evaluating app onboarding without revealing your identity.
And remember the legal side of this. PVAPins is not affiliated with any app or website. Please follow each app's terms and local regulations. Just because you can use a temp number doesn't mean every platform allows it; their terms are their terms.
Common Failure Points and How to Troubleshoot Them
When an OTP doesn't arrive, the cause is usually one of four things: the target service blocks virtual numbers, the number was assigned to the wrong country pool, the SMS was delivered, but the message body was empty, or your polling interval missed the delivery window. Each problem has a specific fix, and a good provider gives you visibility into all of them.
Let's walk through the diagnostic flow:
Blocked service: Some apps actively block virtual/VoIP numbers. You'll know because the code never arrives and no SMS is logged in your dashboard. There's no workaround if the app hard-blocks; you need a provider that tells you this upfront so you don't waste credits.
Wrong country pool: Some apps are geo-sensitive and will only send OTPs to numbers matching your IP or the account's country. Choose a local number at request time if you're testing region-specific features a US number for a US-only fintech, a UK number for a London-based bank, etc.
Missed window: Most providers discard an SMS after a set time (often 5–10 minutes). If you poll too slowly, you lose the code. Poll faster, or better yet, switch to webhooks.
Empty body: Occasionally, apps send a verification link instead of a numeric code. Parse the whole message for URLs or special characters, not just digits. Your regex should handle both cases.
The other thing to check: your account status. Are you funded? Is your API key valid? Did you specify the service ID correctly? These sound basic, but they're the most common causes of support tickets.
If a code fails, the we refund PVAPins team covers activations where no code is delivered. Build your automation without betting on success rates. Try a reliable number and see the difference.
Dying SMS Verification Compared: One-Time Numbers vs. Rental Numbers
There's a key distinction between a disposable number used for a SMS verification and a rented number that stays alive for repeated OTPs. One-time numbers are the most common use case and the cheapest. Rental numbers (1-, 3-, 7-, or even 30-day plans) matter for apps that send recurring codes, like two-factor authentication on a daily-use account.
Think of it this way: a one-time number is a throwaway email address for a single sign-up. A rental is like a dedicated mailbox you can check as often as you want. Both are valid, but they solve different problems.
Here's how to decide:
One-time number: Ideal for account creation, a single sign-up, or testing a single SMS flow. Release it immediately after you've got the code. You're not holding onto anything.
Rental number: Necessary if your app requires re-authentication on login, password reset, or device trust. You need the same number to retain the account's session; switching numbers mid-lifecycle tends to trigger fraud flags.
On-demand rental: You can free the number instantly when you're done; you're not locked into a contract like a traditional phone plan. You can also rent a number for 1, 3, or 7 days depending on the platform.
Cost difference: The cost difference is usually modest; renting a number for a week typically costs less than a coffee. If you're running a long-term project, renting often works out cheaper than repeated one-time purchases.
Some users keep a rental number for months to maintain a stable verification identity, which is especially useful for business accounts subject to audit.
The choice comes down to session persistence: if your account needs to receive codes repeatedly, rent; if it's a one-and-done verification, pay per activation.
Cost Models and Payment Options for SMS Verification APIs
Pricing usually falls in a predictable range: per-activation costs start around $0.10 to $0.50 depending on country and service, and rental costs scale with duration. The right model depends on volume: if you're automating hundreds of verifications a day, per-activation pricing is fine; if you need consistent volume, rentals may be more efficient. The best part is that you pay only for what you actually receive.
A good provider publishes transparent rates for each country and service. They don't hit you with hidden fees or surprise charges. The payment layer is also evolving; crypto is increasingly common for privacy-focused users.
The main cost models:
Pay-per-activation: Cost includes receiving one SMS; some providers refund if no code arrives. This is the "pay-as-you-go" model, perfect for sporadic testing.
Rental pricing: A flat rate for 1, 3, 7, or 30 days, independent of how many SMS receivers online. Great for ongoing projects where you want predictable spend.
Crypto checkout: Many privacy-focused providers accept Bitcoin and USDT, making the payment layer as anonymous as the number itself.
No subscription: You don't pay monthly access fees; you buy credits and consume them. This keeps costs low for sporadic use.
Hidden fees: Always check for number allocation fees, SMS overage charges, or inactivity costs. Read the fine print before you commit.
One tip: start small. Buy $5–10 worth of credits, run a few test verifications across different services, and measure the actual success rate before scaling up. That data is worth more than any pricing page.
Dying SMS Verification in USA, UK, India, Canada, and Germany
Geographic coverage determines whether your verification actually works. The USA, UK, India, Canada, and Germany are the most requested markets for temporary numbers; each country has native service availability, which matters when apps geo-lock their SMS gateways. Globally, a strong provider gives you access to numbers in 200+ countries, so geography never limits your integration.
Here's what to watch for in each region:
USA: Needed for US-only apps and platforms that restrict verification by area code or state. If you're targeting a US-based fintech, you need a US number, period. Some services are also sensitive to the area code, so pick accordingly.
UK & Canada: Popular for fintech apps, crypto exchanges, and regional services. Both markets have strict telecom regulations, so quality providers are essential; a provider with sloppy carrier relationships will fail here more often.
India & Germany: Both have high SMS-dependent user bases and strong two-factor authentication penetration. India's market has unique carrier quirks that a good provider will handle; expect occasional delivery delays, but a solid provider keeps them rare.
Country-specific number pools are frequently replenished to avoid reusing dead numbers, which can cause "number already in use" errors. Ask about this before you commit.
At request time, explicitly specify the country to guarantee you get a number from the right region; don't rely on defaults. The six extra seconds it takes are worth it.
The takeaway: if your use case is geo-specific, make sure your provider actually has strong coverage there, not just "a couple of numbers," but a real pool.
What NOT to Use a Dying SMS Verification API For
Temporary numbers are tools for legitimate privacy and testing, not for fraud, spam, or abusing free-trial loops. Using them to create hundreds of fake accounts to farm referral bonuses, break an app's terms of service, or evade bans violates the spirit of the service and can get you blacklisted. A reputable API provider filters for intent, and you should too.
This is the line you shouldn't cross. We've all seen "Free iPhone" scams that require submitting dozens of phone numbers; that's referral fraud, and it's illegal in many jurisdictions. Similarly, using temporary numbers to bypass a ban you've earned on a platform is a violation of their terms. It's not clever; it's just abusive.
The explicit red lines:
No SMS spam: Don't use the API to send messages; it's reception-only. Any provider that also supports sending is a different tool with different compliance requirements.
No crypto exchange abuse: Most exchanges verify by ID, not just SMS; cluttering them with fake numbers is pointless and illegal. They'll block the number and potentially flag your IP.
No referral fraud: Creating multiple accounts to exploit signing bonuses is outright abuse. It wastes the provider's resources and degrades the service for everyone else.
No bypassing verification to harass or scam other users. This is malicious behavior, and no reputable provider tolerates it.
Legitimate uses include testing your own app's SMS flows, keeping your real number private during sign-ups, and QA automation. Stick to those, and you'll be fine.
How to Choose the Right SMS Verification API Provider
No single "best" provider exists, but objective criteria separate a reliable API from a flaky one: country coverage, transparency about success rates, documentation quality, and fair refund policies. A professional provider holds its product to a high bar; it won't promise the impossible, and it'll be honest when success rates vary by app or service. Verify your own integration against multiple sources before committing at scale.
Choosing a provider is a bit like choosing a cloud host; you need to know what happens when things break. Does the provider have a status page? What's their average uptime? How responsive is support? Ask these questions before you need them.
The evaluation checklist:
Real-time delivery: Test the number's response time on a few services yourself before scaling. Run a series of test requests and measure the time-to-SMS. If it's consistently slow, move on.
Refund policy: Does the provider refund when no code is delivered? This is the single most important trust signal. If they don't, they're just selling you hope, not a service.
Developer API: A formal API with clear endpoint documentation beats a panel-only service. You need programmatic access for automation; that's non-negotiable.
Support channel: Responsive Slack, Telegram, or ticket support is essential for production use. If you can't reach a human when the API breaks, you're in trouble.
Transparent pricing: Published rates per country and service, without hidden sneaky fees. They should be upfront about what a "failure" means.
And one thing to watch for: providers that promise 100% success rates are lying. No one hits 100% across all services and countries. The honest ones tell you where their success rates vary and why.
Key Takeaways
The dying SMS verification API is a workflow for automating OTP reception via temporary virtual numbers; it's a critical tool for dev teams and privacy-conscious individuals.
Integration is a standard REST pattern: request number → receive SMS → retrieve code. Poll efficiently or use webhooks.
Privacy isn't just about anonymity; it's about keeping your primary number clean from marketing lists and data leaks.
Troubleshooting is straightforward if you understand the four failure points: blocks, geo-mismatch, missed windows, and empty bodies.
Choose a provider with transparent refunds, good documentation, and wide country coverage. Don't be swayed by promises of 100% success; that's a red flag.
Compliance note: PVAPins is not affiliated with the app/website or platform. Please follow each app/website’s terms and local regulations.
Last updated:
Ready to Keep Your Number Private in dyin?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Ryan Brooks
Ryan Brooks is a tech writer and digital privacy researcher with 6 years of experience covering online security, virtual phone number services, and account verification. He joined PVAPins.com as a contributing writer after years of working independently, helping consumers and small business owners understand how to protect their digital identities without relying on personal SIM cards.
Ryan's work focuses on the practical side of online privacy — specifically how virtual numbers can be used to safely verify accounts on platforms like WhatsApp, Telegram, Facebook, Google, and hundreds of other apps. He tests these workflows regularly and writes only about what actually works in practice, not just theory.
Before transitioning to full-time writing, Ryan spent several years in IT support and network administration, which gave him a deep, first-hand understanding of the vulnerabilities that come with exposing personal phone numbers to third-party services. That background is what drives his passion for educating readers about safer alternatives.
Ryan's guides are known for being direct and jargon-free. He believes privacy tools should be accessible to everyone — not just developers or security professionals. Outside of work, he keeps tabs on data privacy legislation, follows cybersecurity research, and occasionally writes for privacy-focused communities online.