DukascopyConnect911 SMS Verification Alternative
Quick answer: To verify DukascopyConnect911 with a virtual number, choose a country on PvaPins from $0.12, enter that number as your DukascopyConnect911 phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
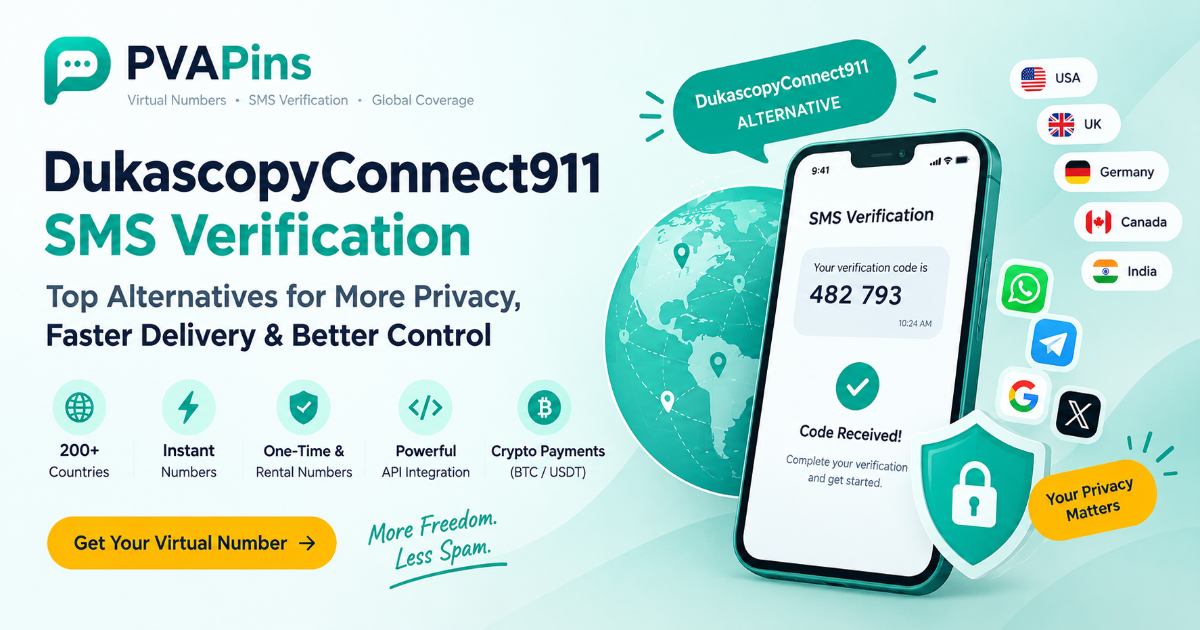
How it works
Register on the platform and top up your wallet via Bitcoin, USDT, or another supported gateway.
Find the service under "Receive SMS" say WhatsApp, Google, or Telegram and set your country.
Copy the virtual number that appears instantly, and plug it into the app's sign-in flow.
The OTP code arrives live on your dashboard in real time. No hidden fees, no subscriptions.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
US numbers are most common and work reliably with Google/WhatsApp; UK is also solid.
Germany is stricter with privacy laws expect more blocks, use local physical SIMs.
India is complex due to DoT rules; find a provider that rotates the pool often.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about DukascopyConnect911 SMS verification.
Is it legal to use a virtual phone number for SMS verification?
Yes, in most countries. But app terms vary; some platforms don't allow virtual numbers, so read each app's Terms of Service. Using temp numbers for legitimate privacy/testing is allowed; mass-created fake accounts in spam tactics violate platform rules and can get suspended.
Why didn't my OTP code arrive?
The number may have been reused before, or the app may block specific virtual provider ranges. Grab a fresh number, wait at least 5 minutes before requesting new codes, and if nothing appears, ask your provider for a refund/no-answer refund.
One-time codes or rentals: which is better?
One-time is cheapest for a single login. But if you're testing an SMS integration or using the same app for a whole week, a 3-day or 1-week rental will save you money compared to buying 10 individual codes.
What should I NEVER use temp SMS numbers for?
Banking, email account recovery, nearly any service tied to your identity, or state services. Only use privacy-conscious apps for genuinely throwaway use-cases.
WhatsApp sometimes bans virtual numbers; how do I fix it?
Sometimes WhatsApp blocks virtuals mid-verification. Wait 10 minutes, then request a fresh number in a different country ; if too many people use US numbers, choose UK instead. A good provider holds diversity. Some apps also offer voice call verification instead.
Can I use this in my CI/CD pipeline?
Absolutely, if there's a REST API to request numbers programmatically and poll for or webhook the OTP. Top providers (like PVAPinas) have Python/Node examples. With a webhook setup, you can instantly see any new message.
Read more: Full DukascopyConnect911 SMS guide
Open the full guide
Let's be honest: if you've ever depended on DukascopyConnect911 SMS verification, you know the drill. You wait for a code that never shows up. You refresh the page. You wait some more. Then you realize the service doesn't hold up for today's apps. This guide is for anyone who's hit that wall. Maybe you're privacy-conscious and tired of handing out your real number. Maybe you're a marketer juggling multiple accounts across platforms. Or maybe you're a developer trying to automate verification flows without losing your mind to manual copy-paste.
Here's the thing: better alternatives exist now. Modern virtual number services work across 200+ countries without locking you into a subscription. You get control both through a simple dashboard and via API when you need to go deeper.
Quick Answer:
Ditch the one-size-fits-all approach. You want a provider offering both one-time numbers for single OTPs and rental numbers (1, 3, 7, or 30-day) for repeat verifications.
Speed matters. Choose a service that issues a number in under 60 seconds and actually refunds you if the OTP never arrives. No ticket systems, no runaround.
Go local. Make sure you can grab US, UK, Germany, Canada, or India numbers specifically. Beware of anything labeled "global" that's really just a US pool with a logo slapped on it.
Pay your way. If you're privacy-focused, crypto checkout is a game-changer. BTC/USDT payments keep your purchase private and unhook you from another recurring subscription.
Think ahead if you build software. Running automated tests? An API is a requirement, not a "premium add-on" you should have to argue about.
Why You Might Need a DukascopyConnect911 SMS Verification Alternative
If you've been using DukascopyConnect911 for OTPs, you've probably run into some annoying roadblocks. Coverage gaps where codes don't land. Slow delivery when you need it fast. Or niggling costs that creep up and up when you're handling OTP verification in a single day.
A solid alternative fixes all of that. You get a dedicated virtual number that works across WhatsApp, Telegram, Google, and hundreds of other platforms. No subscriptions, no tying yourself to one ecosystem. You pay for what you actually use, and the number pops in instantly. Carriers know this scenario well; if someone searches for a DukascopyConnect911 SMS verification alternative, they've hit a hard wall.
Why do people switch in the first place? Usually because their real number started getting spammed. Or they're a tester who needs to simulate sign-up flows without tying up their personal SIM on every app they touch.
Here's who benefits the most:
Developers and QA engineers: In need of fresh numbers at scale for testing and app flow simulation.
Marketers managing accounts: Running social media accounts that demand OTPs daily.
Privacy-conscious folks: Anyone who wants to dodge SIM-swap attacks and telemarketing blasts that follow sharing a phone number.
The best alternative offers a robust, reliable API for heavy automation, plus simple virtual phone numbers for app verification. Once you're not chained to a contract, everything gets easier. No minimum commitments, no opaque pricing decoding.
What to Look for in a DukascopyConnect911 SMS Verification Service Alternative
When you start shopping around for a DukascopyConnect911 SMS verification service alternative, there are a few non-negotiables to have in your back pocket. Topping the list is delivery speed. You want a provider that shows the number fresh on your dashboard instantly, and incoming texts appear in real time, not after five minutes of staring at a cloud spinner.
Here's a practical checklist to separate top-tier providers from frustrating intermediaries who resell recycled numbers:
Real-time dashboard interface: You should see the SMS arrive live in your browser session. If you're waiting for automated emails instead, walk away.
Rotational variety through independent country pools: Any provider can say "200 countries available." But can they actually deliver a US number when you need one at 2 PM on a Tuesday? Check for real coverage, not pie-in-the-sky metrics.
Honest, pay-as-you-go pricing: You pay per OTP received. If someone claims "100% guaranteed success," that's a red flag; don't trust anyone in this industry unquestioningly.
Instant refund protection: If a code doesn't hit, your money comes back. No support ticket gymnastics, no "please wait 3-5 business days."
And the supply should be lightning fast: A number should be issued in under 60 seconds. After that, you're just wasting your time.
You also want to check whether the provider runs its own network or is just reselling someone else's stagnant data. If they're a middleman, you add latency to already-time-sensitive delivery. A good provider should also make it effortless to switch numbers if the first one turns out to be unusable.
6-Step Comparison of SMS Verification Options
Most people assume one kind of "temporary SMS" handles everything. That's not true. You have three solid formats: one-time numbers for a single OTP, daily rentals, and longer monthly leases.
Here's the breakdown:
One-time number (5-10 min window): For instant signups on platforms like Telegram, Google, or Tinder. Pay-per-use, usually runs between $0.10 and $0.50. Good for when you need one code and done.
1-day rental: A full 24 hours of ownership. Great when you're managing app logins that change multiple times a day or the setup requires an extra SMS or two.
3-day to 7-day rental: Perfect for developer sprints or grinding through an app's entire "resend code" workflow without fretting about headroom.
30-day rental: For long-term enterprise projects, device onboarding, or anything that needs a persistent number stable for weeks.
Numbers game: a one-time OTP is cheaper if you need one signature. But if you're pulling 5 OTPs weekly, you need to go rental. It'll save you cash and avoid the headache of repeatedly buying short-lived numbers and repeating the same steps. If you're wading in and reading how you can receive SMS online, that's a smart start, but there's more to the story.
Comparison Cheat Sheet:
Need Best Option Why
Sign up for WhatsApp once One-time OTP Cheapest, instant
Testing your own app Rental (3-day) Stable number for retries and edge cases
Social media account management: Rental (7-day). Multiple SMS per session without adding friction
Hardware/Device setup (router verification) Rental (30-day) Continuous link, no downtime
Low-budget, one-off trial. One-time OTP. Pay for exactly what you need
Quick Start: How to Use an SMS Verification Service in 3 Steps
You don't need a credit card, an existing phone line, or a Dukascopy account. Grab a crypto wallet or payment card, and you're basically ready.
Step 1: Register on the platform and top up your wallet via Bitcoin, USDT, or whatever supported gateway works for you.
Step 2: Find the service under "Receive SMS," say, WhatsApp, Google, Telegram, and set your country.
Step 3: Copy the number that appears, plug it into the app's sign-in flow, and make the OTP appear live on your dashboard.
That's all there is to it. No hidden fees. Just the base number plus what you've spent on the OTP codes you see. And here's the kicker: your unmined balance stays in place for later use, not eaten up while you look away.
This is the easiest way to take back your security. If you're new to this, you'll likely wait for the OTP in the inbox area before anything else. A well-designed panel handles incoming messages live and cuts out the scattered console nonsense. Plus, you can also try out free numbers to get a taste of the dashboard before dropping a cent.
Troubleshooting: Why OTP Codes Fail and How to Fix It
Here is the reality: even the best SMS verification service fails between 1% and 5% of the time. App-specific restrictions, carrier latency, something called "OTP reuse" all of it happens. The top reason for most failures? The number you're using was already used on that same app before. WhatsApp, Instagram, Google they all keep a black/hotlist Of virtual numbers that got tried one too many times. The fix: you truly need a fresh number for each serious attempt.
If a code doesn't show, run these in order:
Wait 5 minutes. Sometimes the SMS sits in a queue because the local carrier is slow.
Request a new number. If you don't get a code within 5 minutes, it's likely not coming. Grab a different number and try that. Also, check the provider's refund policy as you go. Expected, right?
Respect resend cooldowns. Google might force a 24-48 hour wait if you've tried an SMS attempt on a virtual range too many times. Don't tell sync "resend." Wait.
Try a rental instead. If the app is super strict, a fresh number from a top-tier pool may do much better for your situation.
Switch to voice call verification. Some apps route to a voice call when they suspect a virtual number. A solid provider lets you access either channel.
Already junking one number and want a more stable route? Grab a temp number for your next OTP and expect fewer call interruptions from server breakdowns.
DukascopyConnect911 SMS Verification API Integration for Developers
Let's face it: as a developer, manually visiting a web portal to copy codes is like using dial-up. Suppose an API that does it for you is just better. A typical DukascopyConnect911 SMS verification API rewires this: you POST your country and app name, receive a request_id inside JSON, then GET an endpoint until the OTP lands in front of you.
Here's the standard REST flow:
Order Number: POST /v1/sms/number (payload: { "country": "US", "service": "telegram" }) → returns request_id and number in the response.
Poll for Message: GET /v1/sms/message?request_id=123; loop every 2 or 3 seconds.
Capture Success: The moment you spot the OTP token, parse the message and continue with your flow.
Pro-tip: Use WebSocket or webhooks if the provider offers either. A webhook is the cleanest of the two: you set https://your-site.com/hooks, and the platform pushes the OTP to you the instant it arrives: no polling, no sleeping, no waste.
Services like the PVAPins Android app provide developer API docs with examples in Python and Node.js. Once you plug in, you can automate registrations for thousands of test accounts in a safe, isolated sandbox environment.
How to Test Your Own SMS Flow with an OTP API Endpoint
If you're building an app that runs on OTP validation, you need actual end-to-end testing, not a hard-coded bypass that gives false reassurance. An OTP API endpoint lets your CI/CD pipeline trigger a real SMS to a virtual number and validate against it in milliseconds.
This approach catches ugly production issues: expired Windows, flagged country detection, missing message templates, before any users see them.
Here is a minimal Python test script idea:
Use the API for your own app: request a number with your-app-name as the service label.
Trigger your app's OTP: plug that number into your sign-up form (or test harness).
Poll or use a webhook for the SMS.
Timeouts: never wait past the app's code expiry (usually 5 minutes). Check early and often.
Parse the code using a simple regex, and submit it back to your auth endpoint.
Pitfalls developers trip over:
Don't hardcode OTPs. Use the real, active number pool. If the test fails, it means there's a real gap in your infra, not just your test.
Set realistic test limits. If there are fewer charges on the number, 10 tests per night is safe. Unlimited tests on virtual numbers could get you flagged, anyway.
Use rental numbers if you test for multiple days. You don't want your number to expire mid-test suite.
Testing with real SMS infrastructure means your results actually reflect how it behaves, not an idealized guess of what works.
Privacy and Security: Why Using a Virtual Number Beats Your Real SIM
Your phone number is the master key to your identity, and it's not uncommon for it to fall into the wrong hands. Some offenders can use it to get into your 2FA-protected accounts. They don't hack your bank; they hack your phone number.
That's exactly why throwaway virtual numbers are so effective. When you use a temporary number, you put a disposable layer between you and total strangers. No more spam texts getting out of hand. And you slam the door on SIM-swapping, a port-out attack where someone gets access to your 2FA codes by getting onto your real SIM.
The US Federal Trade Commission (FTC) has warned that you should share your numbers only with what's needed. A virtual number is a controlled, disposable perimeter for exactly this. And if you pay via crypto, your purchase is pseudo-anonymous too, with no cards tied to it.
Checklist:
Keep your SIM for banking. Use a burner for a bank, and you also burn your account.
Use a virtual number for trials. Perfect for apps that spam or hang on your data (dating apps, shopping apps, you name it).
Leak prevention under your control. If a merchant sells your number and pollutes you with SMS, throw the number away without consequence.
It costs cents but saves your inbox and your sanity.
Dukascopy Sephora? sms* US/UK/Germany/Canada/India: Global Coverage
If you're in the US, UK, Germany, Canada, or India, you need a provider that understands the local telecom quirks and number supply. Here's the nuanced view: US numbers are the most common, and they work reliably well with Google/WhatsApp. UK is also solid for most apps. Germany is a bit trickier; it has strong data privacy laws, and that trickles down into how virtual numbers behave. Hardware blocks and slow systems are more common. India is famously strict now with SIM validation; many apps and carrier integrations reject a random virtual number. Using a local number typically improves success rates.
USA: High-volume demand; you want direct or near-direct carrier connectivity plus unused "phone farm" recycled numbers.
United Kingdom: Fast and cheap solution for WhatsApp/Telegram.
Germany: Decently strict about privacy, but costly; you want physical SIMs there, not just VoIP, to avoid refusal blockout.
Canada: Usually strong, but certain carrier systems occasionally drop SMS to virtual numbers during verification checks.
India: Very complex, strict DoT rules. A capable provider keeps the number pool active longer than a one-time flow.
Check if the provider's API's GET /countries returns live stock, not personas. If you're heading into Germany or similar places where you need speed and reliability, rented numbers can be your best bet.
Pricing Breakdown: One-Time vs 1, 3, 7, 30-Day Rentals
Get flexible payment. For a single sign-up, you're looking at anywhere from $0.10 to $0.50 per OTP. If those add up, you should rent: a 1-day rental around $5, a 3-day rental for around $12, a week around $17, and a month closer to $25-30. That's actually when rentals become a serious deal when you need codes continuously or on a schedule with test rides.
Pricing Decision Tree:
Testing one app one time? One-time OTP for cents.
Rough day? Rent daily for breathable space.
Temp account for SEO/marketing? Weekly rentals help because you can re-enter verification if the client doesn't log in that day and can do so later.
IoT or long-term device portal? Go rent monthly for a reliable backhaul channel.
One small hidden fee to watch for: "unlimited incoming" claims on rentals. Sometimes these are marketing fiction. Check the package tolerance (100-500 SMS/month) and re-send policies behind the otherwise-unlimited promise; the fine print matters.
Safety, Legality, and Terms of Service: What You Must Know Before Buying
Using virtual numbers to create accounts is safe if you play by the rules. Temporary numbers are a legitimate, standard tool for testing, privacy protection, and setting up new business channels, not for fraud or account abuse.
3 quick do's and don'ts:
DO use it for a consumer app you don't want calls or notifications for, like Telegram.
DON'T use it for your personal Google account spam-password reset PINs. If you lose that third sign-in code, you could lose the whole associated account, and the 2FA recovery loops become nightmare fuel.
DON'T use it for banking or crypto exchange. You need a dedicated, real line when transferring funds. Temporary = risky if recovery is needed.
DO check the email for "voice call" fallback options on any platform that allows voice call verification, in case SMS fails.
Starting slow is always smart. Try a free sms receive site or low-cost numbers before you invest more. That'll give you clean onboarding without hurting your wallet or your trust in the system.
Conclusion: Which DukascopyConnect911 Alternative Is Best for You
Let's cut to the chase: the best alternative is one that doesn't need a subscription. A pay-as-you-go SMS provider with one-time numbers, rentals, and an API is simply a better fit than a siloed legacy service.
Pick what you're optimizing for:
One-offs: Cheap is fine; pick based on delivery speed and refund directness.
Dev/Tech: Look for real REST API integration, webhooks, and actual documentation.
Privacy-focused: Pick a provider that supports anonymous crypto checkout so your data stays back.
You don't need the biggest vendor. You need an agile one. See how PVAPins fits your flow: read more and get a number now.
Key Takeaways
Skip the subscription; pay-per-use aligns exactly with your OTP needs.
Choose country-specific routes: your success rate varies hugely by geography.
Rent for continuity, not for per-OTP convenience; scale compute.
Build API tests that give long-run cost savings, never manual entry.
Call the privacy shots: keep your real number only for banking.
Compliance note: PVAPins is not affiliated with the app/website or platform. Please follow each app/website’s terms and local regulations.
Last updated:
Ready to Keep Your Number Private in DukascopyConnect911?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Ryan Brooks
Ryan Brooks is a tech writer and digital privacy researcher with 6 years of experience covering online security, virtual phone number services, and account verification. He joined PVAPins.com as a contributing writer after years of working independently, helping consumers and small business owners understand how to protect their digital identities without relying on personal SIM cards.
Ryan's work focuses on the practical side of online privacy — specifically how virtual numbers can be used to safely verify accounts on platforms like WhatsApp, Telegram, Facebook, Google, and hundreds of other apps. He tests these workflows regularly and writes only about what actually works in practice, not just theory.
Before transitioning to full-time writing, Ryan spent several years in IT support and network administration, which gave him a deep, first-hand understanding of the vulnerabilities that come with exposing personal phone numbers to third-party services. That background is what drives his passion for educating readers about safer alternatives.
Ryan's guides are known for being direct and jargon-free. He believes privacy tools should be accessible to everyone — not just developers or security professionals. Outside of work, he keeps tabs on data privacy legislation, follows cybersecurity research, and occasionally writes for privacy-focused communities online.