Duffl SMS Verification API: How to Receive Duffl OTP Codes
Quick answer: To verify Duffl with a virtual number, choose a country on PvaPins from $0.12, enter that number as your Duffl phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
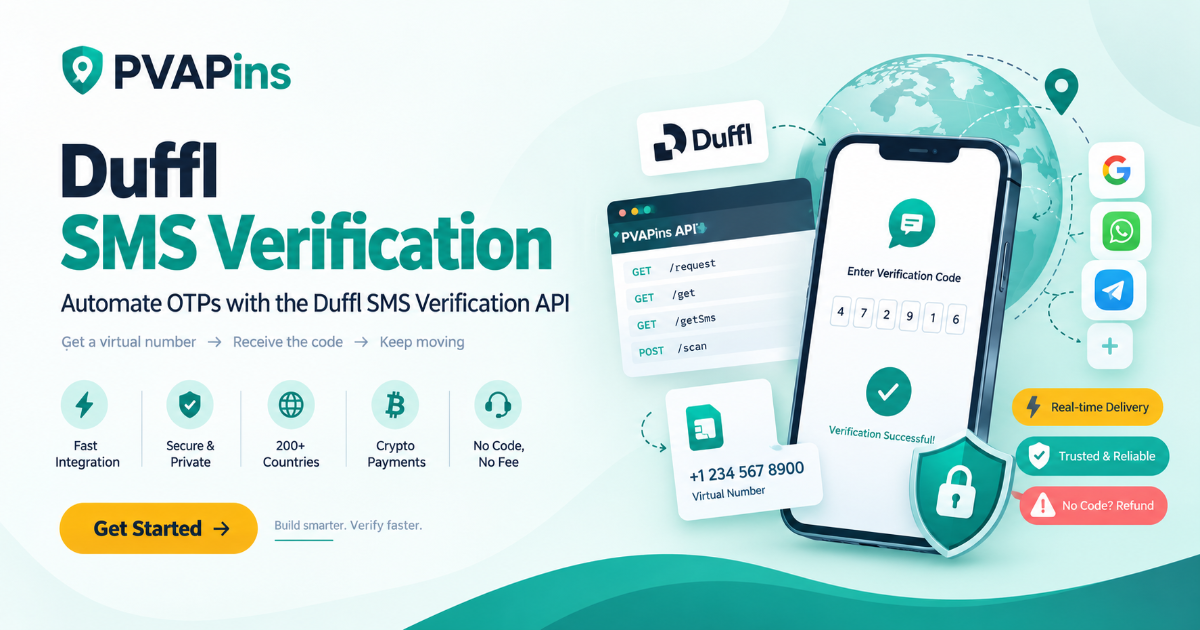
How it works
Top up with crypto: Fund your PVAPins balance with Bitcoin (BTC) or USDT via the price dashboard.
Select the service and country: Pick "Other" or the dedicated device option, choose your country, then send GET /request with your apikey, service, and country.
Receive your number: The API returns JSON like {"id":"223344","number":"+19251231234"} in under 60 seconds.
Input the number into Duffl: Drop the virtual number into Duffl's sign-up or verification screen.
Poll or webhook for the code: Use getSms on a 1–4 second loop, or set up a webhook callback to receive the OTP in real time then build it into your pipeline.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
US & UK: Numbers flow smoothly; virtual numbers are common and OTPs arrive with little friction.
India: Tightly regulated telecom norms mean inconsistent coverage is normal check by try.
Global: Match your app server location with the number's country code for near-instant delivery across 200+ countries.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about Duffl SMS verification.
Is Duffl SMS verification safe to use?
Yes, when used for the right things: your own test accounts, internal QA, and setup. Make sure you're not violating any Safety rules, and never use verification to bypass security systems. Safety = where the intention lies.
Why do I get "Invalid code" or "Already used" from Duffl?
You are probably polling your wait, or you tried the same "used" number twice. The unique OTP has already been consumed, or you exceeded the 8–10 minute limit. Open a new request.
Should I buy a temporary number or rent a number for Duffl?
Use a temporary number for a single sign-up check. Rent deals for ongoing/new optimization testing where several seasonal cycles need the same number to remain registered.
What shouldn't I use a temporary number for?
Never use a number for payments, financial benefits, bank recovery, or official government services, as these have a high-risk security profile. Use your personal, physical SIM.
How do I get a refund if a code never arrives?
Go to Support via "Open Ticket," provide the activation ID, and explain. Support checks whether the SMS was delivered. If not, they'll top up your balance.
Does this API work with Google and WhatsApp?
Yes. For Google, you'll need to be judicious about the number to be a fresh one just attached to the Google service. For WhatsApp, it works; stick with fresh numbers and avoid batch spam.
Read more: Full Duffl SMS guide
Open the full guide
Welcome to the no-nonsense guide to automating Duffl SMS verification. You're probably a developer, an automation engineer, or a power user who's tired of babysitting browser tabs. You don't want to sit in a dashboard refreshing a page; you want a Duffl SMS verification API that hands you a fresh number, grabs the OTP, and lets you move on to the next task. This guide cuts the fluff. We'll walk through integration steps, where to grab numbers, how to troubleshoot when codes fall flat, and the compliance stuff you can't ignore.
Here's the roadmap: we'll cover API logic, polling options, the exact request-to-code flow, handling picky apps like Google, and troubleshooting steps for when things break.
Quick Answers
Service Name: PVAPins exposes a REST API to request temporary numbers and receive OTPs.
Payment: Pay per use (starting ~$0.10), settled via crypto (BTC, USDT), no subscription fees.
Delivery: Codes arrive via real-time polling or webhooks (callbacks).
Refund: No code arrives? You get a refund under the "No Code, No Fee" policy.
Compliance: PVAPins is not affiliated with any app. You must follow each app's Terms of Service and local regulations.
What Is a Duffl SMS Verification API?
A Duffl SMS verification API is a programmatic interface that lets you request a virtual phone number and retrieve the SMS verification code sent to it, all without a human ever looking at a screen.
Think of it as the bridge between your project's logic and how Duffl delivers OTP codes. SMS-based OTP is distinct from email verification because it's tied to a phone number. An API abstracts all that away.
Why a dedicated API beats manual copy-paste
When you're stuck in a manual dashboard, you're a prisoner of logins and browser tabs. With an API, you write a script once and reuse it forever. The real selling point is speed and repeatability. You call, get your number, drop it into your app, wait 5–10 seconds, hit the API again, grab that code, and push it through no typos, no delays, no copy-paste errors.
How the request and callback flow looks in practice
You POST to the getNumber endpoint with your country parameters.
Your script takes that number and inputs it into Duffl's sign-up or verification screen.
Duffl triggers the SMS server-side.
You either poll via getSms or receive a webhook response.
"Your pipeline treats the message as pending until the API confirms delivery, ensuring real-time verification."
Duffl OTP Receipt API: Understanding Polling vs. Callback Options
This is the first fork in the road. You've got two paths for receiving your Duffl OTP: Polling or Callbacks. Your choice will depend on your workload.
Polling intervals for real-time code delivery
With the Duffl OTP receipt API, you'll typically set up a loop that pings the status endpoint every few seconds. It's simple to code and works fine for low-volume testing.
Interval: 1–4 seconds is a sweet spot for fast verification. Don't hammer it harder than that.
Trade-off: Polling generates more HTTP requests, which can trip rate limits if you're doing hundreds of verification checks per minute.
Cost efficiency: If you're only paying per SMS received online, heavy polling won't hurt your wallet much, but it can tax your network stack.
What happens when the OTP is delayed
Sometimes the SMS gateway is slow. It might take anywhere from 15 to 30 seconds to route a message. If your code only polls for 10 seconds, it'll time out, and you'll lose that number.
A smarter timeout: Set your application timeout to 3–5 minutes before declaring failure.
An alternative: The delay may be caused by Duffl's anti-spam queuing, not the carrier. Build a "resend code" fallback into your flow as a contingency.
Step-by-step: Request a number in under 60 seconds.
Here's the process step-by-step:
Top up with crypto: Fund your PVAPins balance with Bitcoin (BTC) or USDT via the price dashboard.
Select the service: Rather than choosing "Duffl" specifically, you'll usually pick "Other" or the dedicated device option.
Select the country: Decide where you want the SIM "registered" (like the US, UK, etc.).
Send the API call: Use GET /request with your API key, service, and country.
Receive your numbers: The API returns JSON like: {"id": "223344", "number":"+19251231234"}.
That's it. You're now working with your Duffl SMS numbers in under a minute.
Selecting the right endpoint: temporary vs. long-lived numbers
The PVAPins API has two core modes:
Pay-per-use (Temporary): The classic one-time number for a quick OTP, valid for a few minutes.
Extended/SMS rental: For accounts that need stable MFA over days. You can use a virtual rent number service for a longer window, usually 1, 3, 7, or 30 days.
If you need just one code, stick with “Pay per use.” If the app expects a steady number for days, go the rental route.
Duffl Verification via API Request: From Number Purchase to Code Arrival
Here's what happens under the hood after you've ordered your number critical knowledge when things don't behave.
The Request Lifecycle
GET /stubs/hash: You get the activation ID from the purchase response.
GET /get: Initially, it returns an empty array "[]" if no SMS has arrived.
Message sent: Duffl requests the virtual number.
Callback injection: PVAPins stores the message asynchronously.
POST /scan: The system parses the code into a usable value.
Timeouts and retry logic for production environments
Do not create a loop that runs forever. Build production code that queries the SMS endpoint until the session actually expires (Duffl sessions usually last 8–10 minutes). Once the deadline hits, return an error and call the "resend code" endpoint.
Duffl Verification Programmatic: Why Slugs Matter for Fast Project Setup
Let's talk about the behind-the-scenes elements that most guides skip.
Structuring your request to keep verification repeatable
A slug is a tag within the API (e.g., google_confirm, whatsapp_bridge). It ties to a cvid (customer vector ID) for future tracking:
Rewrite handling: If a request fails and you retry, the slug helps prevent duplicate purchases.
Session tracking: The service uses the slug to associate callbacks and manage state.
CVOID and session management what it really does
Cvid is short for call vector identifier. It's a tracking mechanism that links your session to a specific request for easier accounting.
Set your cvid to match your internal "registration" ID.
If you hit max retries, the slug system automatically rejects future duplicates.
A clear tip: In production, protect your sessions. Inside your system, gate the cvid to the user ID requesting it to prevent API misuse.
API for Duffl SMS OTP: How to Integrate with Other Services
One major bonus: these numbers aren't locked to a single app. The Duffl SMS OTP API works with WhatsApp, Telegram, Google Accounts, and more.
Verifying accounts from services that auto-detect virtual numbers
Some platforms (like WhatsApp) actively track whether a number is tied to a physical SIM. The API can't fix that. But it's not a permanent blocker either; it just means you'll need fresh numbers, not a single reused one.
Slack or other dev tool integrations for code routing
If you don't want the code just sitting in your terminal, you can route it somewhere more useful:
Slack: Write a webhook that sends the parsed message as a JSON payload to your dev channel.
Trello/Notion: Push successful OTP data to your QA pipeline for tracking.
This works because the API exposes the data at a standard endpoint, making it easy to pipe the extracted digits into any chat tool.
Google Duffl SMS Verification: Verify Google Accounts with a Virtual Number
Let's talk about the big one: Google. Google is a strict gatekeeper when it comes to virtual number reputation. Using a virtual number for verification is okay for testing your own workspace, but it has limitations you need to know.
What works and what doesn't
Works: Simple sign-ups and verification checks, typically with a new number on the first attempt.
Doesn't always work: Google uses machine learning algorithms to detect virtual number patterns. If a number has been used before, it can throw "This number cannot be used for verification."
How to prevent failed Google attempts
Try these:
Use a fresh, untouched number, never a number already used or shared.
Try a different country code. Something less common works more often.
Don't reuse numbers in the same session. Google tracks cross-account data actively.
How to trigger Google's SMS resend
If you don't get the code the first time, give it up to 60 seconds. Google sometimes sends a "Try again in 1 minute" message. You can manually ask for a resend from Google's side using your session. Verify ads from the number, waiting at least 60 seconds between attempts.
Duffl SMS Verification in the US, UK, Canada, and Germany
Geography matters. Different countries run different telecommunication grids and have different attitudes toward virtual numbers.
US and India: Why Number Polling Differs
US: Number-rich ecosystems. Virtual numbers are common, so platforms usually accept them without much friction.
India: Tightly regulated, based on stringent telecom norms. An operator checks the IMEI, so inconsistent coverage is normal.
UK: Privacy-focused
The UK (under ICO guidance) is more privacy-friendly. OTP delivery tends to be smooth, and temporary numbers are less stigmatized than elsewhere.
Australia and Canada: What to expect
Coverage is generally reliable for testing and management, but be advised that these regions sometimes have a small delay for high-volume automated services.
Global Coverage for Duffl Verification: 200+ Countries and Real-Time Delivery
PVAPins Android app operates across 200+ countries, but coverage isn't equal. It's worth noting the reality: practices differ, and some countries deliver better than others.
Cross-border OTP routing and latency
For "near-instant" delivery, match your app server location with the number's country code. A US number paired with a US server = fastest possible response. A UK number through an India-based server = slightly more latency, still functional.
The "when to go global" reality check
You don't need 200 countries in most cases. Realistically, you'll use fewer than 10 regularly the ones that match your actual user base and platform requirements.
Troubleshooting When Verification Codes Fail or Arrive Late
Let's address the most common reason you're here: something broke.
Why your request is active but the OTP never turns up.
There are a few usual suspects:
The number was reused for a platform that already flagged it (or that's the second attempt in 24 hours).
App throttling: Duffl blocks the request because too many attempts came from your IP in a short window.
The number is on a blocklist: Google and WhatsApp specifically maintain their own blocklists for virtual numbers.
Quick move: Use a different, fresh number, wait 5 minutes, and try the app's "resend code" button.
What to do if a code was already used or expired
OTPs are single-use and time-limited (typically 8–10 minutes). If you attempt a "resend" with the same number that already got a text, you'll hit "Invalid code." The most common cause is that your application uses the SMS variable elsewhere.
Fix: Treat each number as a one-shot container; for any retry, request a brand new number instead.
How to get a refund if a code is truly never received
Based on the No Code, No Fee policy: if you didn't receive the SMS within the validity window, you open a support ticket. They'll check the delivery logs. If confirmed as not delivered, any remaining credit is re-added. Worth knowing before you buy: the exact refund conditions in the pricing policy terms.
Security, Compliance, and Risks of Using Temporary Numbers
Let's outline the boundaries. Using virtual numbers is fine for most use cases, but you should respect the guardrails.
The "do not" list
Do not use virtual numbers for financial services (banks, digital wallets with identity checks). These often flag "virtual detected," which can cause a permanent ban.
Do not use virtual numbers for medical, insurance, or security-sensitive 2FA recovery.
The no-list really is: anything where a false must confirm you with non-repudiation.
Does PVAP OTP work better than public sites?
We don't claim 100% success. What we do offer is better quality of service than the public "OTP inbox" sites. PVAP fabric rests on consistent delivery.
Getting Started With PVAPins: Your Next Step
Your next step is simple: write a test.
Create an account: Top up with Bitcoin or USDT (minimum $5).
Try the free tier: If it's your first time, use your free online phone number to check how SMS receiving works without spending anything.
Scratch a quick script: Replace the console API_KEY, request a number, and poll for the code.
Build your pipeline: Run it via your CI/CD once you've proven it.
Looking to build a solid bulk workflow? Skip the one-off and rent a number for 3, 7, or 30 days for stable verification over time.
Compliance note: PVAPins is not affiliated with the app/website or platform. Please follow each app/website’s terms and local regulations.
Last updated:
Ready to Keep Your Number Private in Duffl?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Mia Thompson
Mia Thompson is a content strategist and digital privacy writer with 5 years of experience creating in-depth guides on online security, virtual number services, and SMS verification. At PVAPins.com, she specializes in breaking down technical privacy topics into clear, actionable advice that anyone can apply — no IT background required.
Mia's work covers a wide range of real-world use cases: from setting up a virtual number for app verification, to protecting your identity when creating accounts on social media, fintech platforms, and messaging apps. She researches every topic thoroughly, personally testing tools and workflows before writing about them, so readers get advice that's grounded in actual experience — not just theory.
Prior to focusing on privacy content, Mia spent several years as a digital marketing strategist for SaaS companies, where she developed a strong understanding of how platforms collect and use personal data. That experience sparked her interest in privacy tech and shaped the reader-first approach she brings to every piece she writes.
Mia is especially passionate about making digital security accessible to non-technical users — particularly people who run small businesses, manage multiple online accounts, or are simply tired of exposing their personal phone number to every app they sign up for. When she's not writing, she's testing new privacy tools, reading up on data protection regulations, or thinking about ways to simplify complex security concepts for everyday readers.