Dropverse SMS Verification API: Instant OTP Integration
Testing SMS verification flows with physical SIM cards is a nightmare. A Dropverse SMS verification API solves this with on-demand disposable virtual numbers.
Quick answer: To verify Dropverse with a virtual number, choose a country on PvaPins from $0.12, enter that number as your Dropverse phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
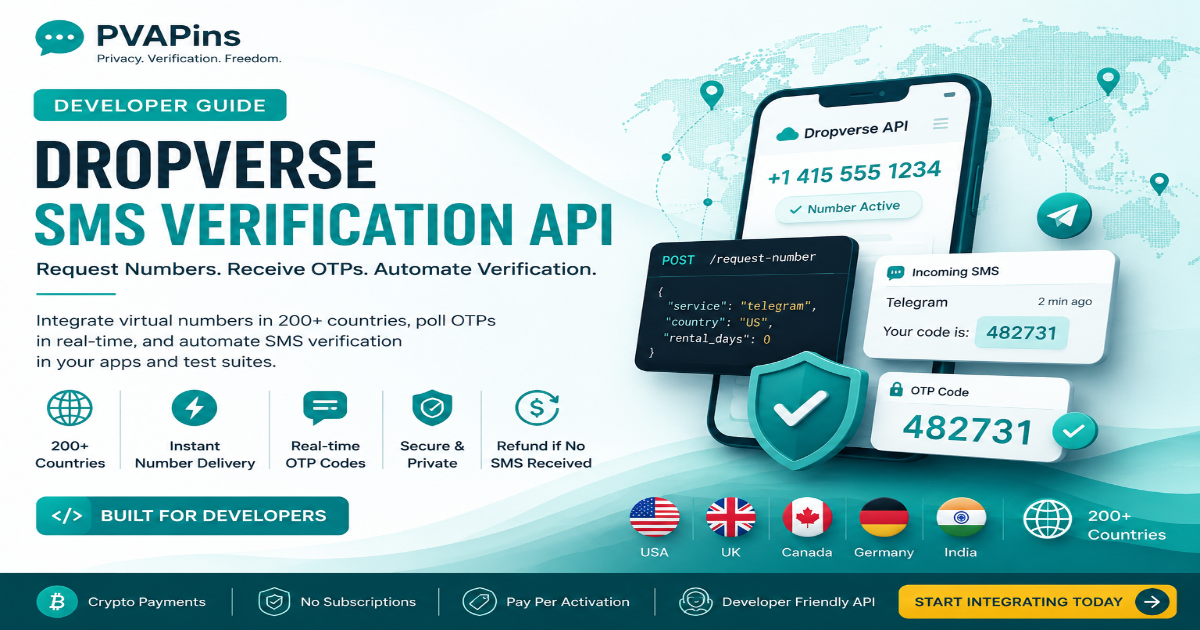
How it works
Authenticate: Set your API key as a header: curl -H "Authorization: Bearer YOUR_KEY". This is your identity for every request.
Request a number: POST to the /request-number endpoint with {"service": "telegram", "country": "US"}. You'll get a JSON response with your number_id and phone number.
Poll for messages: GET the /get-messages endpoint with your number_id every 3 seconds. Loop until you get a non-empty response.
Extract the OTP: Parse the JSON response and regex out the numeric code from the message body. Most OTPs are 4–8 digits.
Release the number: Once you've got the code, DELETE the number to free it up and avoid extra charges.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
USA: Best overall reliability; most apps send codes instantly to US virtual numbers. Default choice for most tests.
UK: Fast delivery with strong carrier infrastructure; ideal for testing fintech and e-commerce apps.
India: TRAI SMS regulations require templates and headers, which can cause delays expect occasional hiccups.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about Dropverse SMS verification.
Is using a Dropverse SMS verification API legal?
Yes, receiving OTPs on a virtual number is legal in most jurisdictions, but you must follow each app's terms of service and local regulations. PVAPins is not affiliated with any app or website, and using numbers for fraud, spam, or ToS violations is prohibited.
Why did my OTP code fail to arrive?
The most common causes are: the app never triggered the SMS, the app blocked the virtual number, the carrier delayed the message, or you polled the wrong number ID. Check the sender's status, verify your number_id, and wait up to 60 seconds before requesting a refund.
What's the difference between a one-time number and a rental number?
A one-time number is used for a single activation and then released. A rental number stays active for 1, 3, 7, or up to 30 days, so you can receive repeat OTPs from the same app without requesting a new number each time.
What should I NOT use temp numbers for?
Don't use virtual numbers for fraud, spam, creating fake accounts to evade bans, or any activity that violates an app's terms of service. The platform is for legitimate testing, privacy protection, and business verification only.
How do I troubleshoot a code that's taking too long?
First, confirm the app actually sent the SMS. Then check your polling interval; 3 seconds is ideal. If nothing arrives after 60–120 seconds, release the number and request a new one, or contact support for a refund if the code never comes.
Can I use the API for automated testing in CI/CD pipelines?
Yes, the REST API is designed for automation. You can request numbers, poll for OTPs, and release numbers programmatically, making it easy to integrate SMS verification testing into your CI/CD workflows.
How fast is number delivery, really?
Number allocation is instant: as soon as your payment clears, the number appears in your dashboard. Code delivery varies by app and country but typically lands within 5–15 seconds for major services like WhatsApp, Telegram, and Google.
Read more: Full Dropverse SMS guide
Open the full guide
Testing SMS verification flows with physical SIM cards is a nightmare. You're juggling devices, burning through personal numbers, and praying your test doesn't trigger a spam flag. A Dropverse SMS verification API solves this by giving you disposable virtual numbers on demand, perfect for automating sign-up flows, testing OTP retry logic, and verifying your app's SMS infrastructure without the hardware hassle.
This guide walks you through the entire integration: requesting numbers, polling for codes, optimizing delivery speed, and avoiding the common pitfalls that waste developer hours. Whether you're building a CI/CD test suite or need a quick verification number for a staging environment, you'll find the mechanics you need here.
Quick Answer:
Request a number: POST to the API with your app and country parameters; you get a virtual number instantly after payment.
Poll for OTPs: GET the message endpoint every 3 seconds to retrieve incoming SMS codes.
Pay per use: Rates start around $0.10 per activation, with a refund if no code arrives.
Scale globally: Access numbers in 200+ countries, including the USA, UK, Canada, Germany, and India.
Automate everything: The REST API fits into CI/CD pipelines, staging environments, and QA scripts with minimal overhead.
Why Developers Choose a Dropverse SMS Verification API Over SIM-Based Testing
Testing SMS flows with physical SIM cards is slow, expensive, and impossible to scale across multiple countries. A Dropverse SMS verification API for developers gives you disposable virtual numbers on demand, so you can automate sign-up flows, test OTP retries, and verify your app's SMS logic without burning through personal phone numbers. It also keeps your real SIM out of marketing databases and away from spam lists.
Here's why teams make the switch:
Scale without hardware: Spin up hundreds of unique numbers for parallel test cases without buying SIM cards or juggling devices. Your CI/CD pipeline can request a fresh number for every test run.
Global coverage: Access numbers in 200+ countries, letting you test region-specific SMS gateways and carrier behaviors. Need to verify how your app handles a German carrier's routing? You can do that.
Privacy-first: Your personal number stays off third-party databases, and crypto payments keep your billing footprint anonymous. This matters when you're testing apps you don't want tied to your identity.
No subscription: Pay per activation rather than committing to a monthly plan you won't fully use. For a team running 50 tests a week, that's pennies per test.
Automation-ready: The REST API fits into CI/CD pipelines, staging environments, and QA scripts with minimal overhead. No UI automation required just HTTP calls.
The bottom line: if you're building software that sends SMS verifications, you need a way to test it at scale. Physical SIMs don't scale. A virtual number API does.
How the Dropverse SMS Verification API Request Number Flow Works
The request number flow is a straightforward two-step sequence: you ask the API for a number tied to a specific app and country, and the API returns a virtual number instantly to your dashboard. From there, the number is yours for the activation window, and any incoming SMS is routed to your account for polling. This is the foundation of every integration, so getting it right matters.
Here's what happens under the hood:
Specify the target service: The API accepts parameters for the app (e.g., WhatsApp, Telegram, Google) and the country code so you get a number that works for your use case. This isn't a random number; it's likely to receive codes from that specific service.
Instant allocation: Once you request a number, it appears in your dashboard immediately with no waiting queues or manual approval steps. The moment your payment clears, the number is yours.
One-time vs. rental: You can request a single-activation number or rent the same number for 1, 3, 7, or up to 30 days for repeat OTPs. This is critical for apps that send periodic verification codes (like a banking app that re-authenticates weekly).
Cost transparency: The price is shown before you confirm, and you only pay for the number plus the receive SMS online. No surprise charges when the code arrives.
Refund safety net: If no code arrives for your activation, you're eligible for a refund, no fine-print games. This is your insurance against flaky senders.
The key takeaway: the request flow is designed to be frictionless. You specify what you need, pay a small fee, and get a working number in seconds.
Poll OTP with the Dropverse SMS Verification API: A Step-by-Step Pattern
Polling is how you retrieve the OTP once it lands on your virtual number. You send a GET request to the API's message endpoint, passing the number ID you received earlier, and the API returns any SMS messages associated with that number. The pattern is simple: request a number, poll at a sensible interval, and extract the code from the SMS body.
Here's the exact pattern that works:
Identify the endpoint: The API exposes a dedicated message retrieval route that accepts your number ID as a query parameter. Typically, this looks like GET /get-messages?number_id=12345.
Parse the response: The JSON payload includes the sender, timestamp, and message text so you can regex out the 4–8 digit code. For example: /\b(\d{4,8})\b/ will catch most OTP formats.
Poll responsibly: A 2–5 second interval is usually enough; hammering the endpoint faster than that wastes requests without speeding up delivery. The SMS won't arrive faster because you're polling harder.
Handle empty responses: If the API returns no messages yet, your code should retry gracefully instead of throwing an error. A simple if (messages.length === 0) { wait(3000); retry(); } pattern works.
Mark as consumed: Once you've extracted the OTP, close out the number to avoid reusing it accidentally in your test flow. This prevents cross-contamination between test cases.
The polling pattern is the heart of your integration. Get this right, and the rest is straightforward.
Dropverse SMS Verification API Integration: Authentication, Endpoints, and Payloads
Integration boils down to three things: authenticating with your API key, hitting the right endpoints, and sending the correct JSON payloads. The API uses a simple key-based auth header, so there's no OAuth dance or token refresh logic to manage. You can be up and running with a working integration in a single afternoon.
Let's break down each piece:
Authentication: Pass your API key in the request header (e.g., Authorization: Bearer YOUR_KEY), no complex handshakes. This is standard bearer token auth, which every HTTP client supports natively.
Core endpoints: You'll typically use /request-number, /get-messages, and /release-number to complete the full lifecycle. That's three endpoints for the entire flow: request, poll, release.
Payload structure: A request body might look like {"service": "whatsapp", "country": "US", "rental_days": 0} for a disposable phone number. For a rental, change rental_days to 7 or 30.
Response format: The API returns JSON with a number_id, the actual phone number, and a status field you can check. Example: {"number_id": "abc123", "number": "+14155551234", "status": "active"}.
Error handling: Standard HTTP status codes (400, 401, 404, 429) tell you exactly what went wrong, so log them and retry intelligently. Check the HTTP status codes documentation if you need a refresher on what each code means.
For full details on every endpoint, parameter, and response field, check the developer API documentation before you start coding.
Dropverse SMS Verification Real-Time OTP: Understanding Code Arrival Latency
Real-time OTP delivery means the code is routed to your dashboard as soon as the sender's SMS gateway processes it, typically within a few seconds. But "real-time" isn't magic; it depends on the sender's infrastructure, the carrier path, and whether the number is high quality. Knowing where latency creeps in helps you set accurate expectations for your test suite.
Here's what affects how quickly you see the code:
Sender-side delay: The app you're verifying (e.g., Telegram) must actually trigger its SMS gateway before anything moves that's outside your control. If the app's server is slow, your code will be slow.
Carrier routing: International SMS can hop through multiple carriers, and some routes are faster than others depending on the country. A US-to-US message is faster than a US-to-India message, simply because there are fewer hops.
Number quality: Fresh, well-maintained numbers tend to receive codes faster than recycled ones with a history of abuse. This is why it's worth paying a few cents more for a high-quality number.
Dashboard vs. API: Both receive the code simultaneously, but your API polling interval determines how quickly you notice it. If you poll every 10 seconds, you'll see the code up to 10 seconds after it arrives.
What "real-time" means here: Seconds, not milliseconds, so design your polling loop to tolerate a 5–15 second window. Don't set a 2-second timeout and expect success.
The practical takeaway: most OTPs arrive within 5–15 seconds for major apps. Build your integration around that expectation.
Dropverse SMS Verification Number Delivery Time: What Affects Speed
Number delivery time is the gap between your API request and the number appearing in your dashboard, and it's usually instant, measured in milliseconds. The bigger variable is code delivery time, which depends on the sender and carrier. This section separates those two clocks, so you know which one you can actually optimize.
Here's the breakdown:
Number allocation is instant: Once your payment clears, the API assigns a number immediately, with no manual review or provisioning queue. This is the fastest part of the entire flow.
Code delivery is variable: The SMS itself can take 2–30 seconds depending on the app's gateway and the destination country's carrier network. Major apps with robust SMS infrastructure are on the fast end; niche apps are slower.
Country-specific routing: Some regions (like India) have stricter SMS regulations that can add a step to the delivery path. TRAI SMS regulations require template registration, which can delay or block messages.
Peak hours matter: Sending a verification at 2 AM in the target country might be slower if the carrier does batch processing. This is rare, but it happens.
What you can control: Your polling interval, your number selection, and your retry logic, not the sender's infrastructure. Focus your optimization efforts there.
The key distinction: number allocation is always fast; code delivery is variable. Don't confuse the two when debugging.
Dropverse SMS Verification Instant Delivery: When It Happens and When It Doesn't
Instant delivery is the norm for the number itself and often for the code, but it's not guaranteed for every app or country. Some senders throttle SMS, some carriers are congested, and some apps route verification through multiple gateways. The honest take: expect instant number allocation, expect fast code delivery most of the time, and build retry logic for the exceptions.
Here's the realistic picture:
The instant part: Number allocation and dashboard visibility happen immediately after payment confirmation. You'll see your number in under a second.
The fast part: Most OTPs arrive within 5–15 seconds for major apps like WhatsApp, Google, and Telegram. These services have robust SMS infrastructure.
The slow part: Niche apps with weak SMS infrastructure, or countries with heavy SMS filtering, can take 30+ seconds. Budget for this in your test timeouts.
The failure part: If no code arrives within a reasonable window (e.g., 2–3 minutes), you can request a refund and try a different number. Don't waste 10 minutes on a dead number.
The smart move: Use the API's status endpoint to check whether the number is still active before giving up. Sometimes the number expires or gets released accidentally.
The honest expectation: instant delivery is the norm, but not the guarantee. Build for the 95% case and handle the 5% gracefully.
Dropverse SMS Verification in USA, UK, Canada, Germany, and India: Coverage Nuances
The SMS verification service works across 200+ countries, but the big five USA, UK, Canada, Germany, and India each have quirks worth knowing. The USA and UK offer the most reliable, fastest delivery for major apps. Canada and Germany are solid but can occasionally route through slower carrier paths. India has the most regulatory friction, with SMS often requiring extra headers or being delayed by TRAI compliance checks.
Here's the per-country breakdown:
USA: Best overall reliability; most apps send codes instantly to US virtual numbers, and number availability is high. This is your default choice for most tests.
UK: Fast delivery with strong carrier infrastructure; ideal for testing fintech and e-commerce apps. Many European apps route through UK gateways.
Canada: Reliable but slightly slower than the US; some carriers route international SMS through US hubs. Expect a 1–2 second delay compared to US numbers.
Germany: Strong privacy regulations mean some apps require explicit consent flows; delivery is generally fast once the SMS is sent. Review GDPR guidance for SMS data if you're handling user data.
India: TRAI SMS regulations require SMS templates and headers, which can cause delays or rejections for some senders, so expect occasional hiccups. This is the most challenging country for SMS verification.
Practical advice: default to US or UK numbers for general testing, and use India only when you specifically need to test Indian carrier behavior.
Dropverse SMS Verification Fast Delivery: Optimizing Your Polling Interval
Fast delivery isn't just about how quickly the SMS arrives; it's about how quickly your code notices it. The right polling interval balances responsiveness against API rate limits. A 3-second interval is a sweet spot for most use cases: it catches codes within seconds of arrival without hammering the endpoint.
Here's how to tune your polling:
Start at 3 seconds: This catches most OTPs within one or two poll cycles after they land. It's responsive without being wasteful.
Back off after 30 seconds: If no code arrives, switch to 5-second intervals to reduce load while still staying responsive. This prevents unnecessary API calls during the long tail.
Cap your total wait: Set a hard timeout (e.g., 120 seconds) and then decide whether to retry with a new number or request a refund. Don't let a single test hang forever.
Use exponential backoff: If the API returns 429 (rate limit), double your interval rather than retrying immediately. This respects the API's constraints and prevents further throttling.
Log everything: Record timestamps for request, first poll, and code arrival; this data helps you tune your integration over time. You'll quickly learn which apps are fast and which are slow.
The optimization goal: catch the code within 2–3 seconds of arrival without wasting API calls. A 3-second interval achieves this for most use cases.
Dropverse SMS Verification Code Arrival: Debugging Failed or Delayed OTPs
When a code doesn't arrive, the problem is almost always one of four things: the sender never triggered the SMS, the app blocked the number, the carrier delayed the message, or you're polling the wrong number ID. This section walks through a systematic debug sequence so you can isolate the failure fast and get back to testing.
Follow this checklist when a code doesn't arrive:
Check the sender side first: Did the app actually say "code sent"? If not, the problem is upstream; your number never got the SMS. Check the app's UI or logs for confirmation.
Verify the number ID: Make sure you're polling the correct number_id and that the number hasn't been released or expired. A simple typo here causes 90% of "missing code" issues.
Look for app-side blocks: Some apps detect virtual numbers and refuse to send codes; if so, try a different country or a rental number. This is more common with banking and government apps.
Wait before giving up: Carrier delays can stretch to 60 seconds in some regions; set your timeout accordingly. Don't assume failure at 30 seconds.
Use the refund policy: If the code genuinely never arrives, PVAPins FAQ refunds the activation so you don't pay for dead ends. This is your safety net.
The systematic approach: rule out your own errors first, then investigate sender-side issues, and finally accept the refund if nothing works.
Security and Compliance When Using a Dropverse SMS Verification API
Using virtual numbers for verification is legal, but it's not a free pass to break rules. You must respect each app's terms of service, avoid using temp numbers for fraud or spam, and comply with local regulations in the countries where you operate. PVAPins Android app is transparent about this: the platform exists for legitimate testing, privacy protection, and business verification, not for abuse.
Here's what you need to know:
Legality: Receiving OTPs on a virtual number is legal in most jurisdictions, but using them to evade bans or commit fraud is not. Know the difference.
Terms of service: Some apps prohibit virtual numbers outright; check the target app's ToS before integrating. If the app says "no virtual numbers," respect that.
Data privacy: Your real number stays protected, but the virtual number's SMS content should still be handled securely in your logs. Don't store OTPs in plain text if you can avoid it.
No fraud, no spam: PVAPins explicitly prohibits using numbers for scams, bulk messaging, or any activity that violates app terms. This is a hard line, not a suggestion.
Compliance line: "PVAPins is not affiliated with any app or website. Please follow each app's terms and local regulations."
The security mindset: treat virtual numbers like any other test credential; use them responsibly, handle the data carefully, and respect the platforms you're testing against.
Dropverse SMS Verification API for Developers: Pricing, Refunds, and Rental Windows
The pricing model is refreshingly simple: you pay per activation (around $0.10 and up depending on country and app), and you're refunded if no code arrives. For longer test cycles, you can rent a number for 1, 3, 7, or up to 30 days, ideal for apps that send periodic OTPs or for staging environments that need a stable number. Payments are handled via Bitcoin, USDT, and other crypto gateways for fast, private checkout.
Here's the full pricing picture:
Pay-per-use: No subscription, no monthly fees just the number and the SMS you actually receive. This keeps costs predictable and low.
Transparent rates: Prices are shown upfront before you confirm; no hidden fees or surprise charges. Check the transparent pricing page for current rates.
Refund policy: If the code never arrives, you get your money back; that's the safety net for flaky senders. No lengthy support tickets required.
Rental plans: 1-, 3-, and 7-day rentals, plus full 30-day options, for repeat OTPs and long-running tests. This is perfect for staging environments that need a stable number.
Crypto checkout: Bitcoin, USDT, and other popular gateways keep your payment private and instant. No credit card trail linking your testing activity to your identity.
If you need a number that lasts longer than one OTP, you can rent a number for longer windows at a flat rate.
Quick Start: Your First Dropverse SMS Verification API Call in Under 5 Minutes
Here's the fastest path from zero to a working integration: sign up, add crypto funds, request a number via the API, poll for the OTP, and extract the code. No SDK required; curl or any HTTP client. This quick start assumes you already have an API key and a funded balance.
Follow these five steps:
Authenticate: Set your API key as a header: curl -H "Authorization: Bearer YOUR_KEY". This is your identity for every request.
Request a number: POST to the /request-number endpoint with {"service": "telegram", "country": "US"}. You'll get a JSON response with your number_id and phone number.
Poll for messages: GET the /get-messages endpoint with your number_id every 3 seconds. Loop until you get a non-empty response.
Extract the OTP: Parse the JSON response and use regex to extract the numeric code from the message body. Most OTPs are 4–8 digits.
Release the number: Once you've got the code, DELETE the number to free it up and avoid extra charges. This keeps your account clean.
That's it: a complete verification cycle in under 5 minutes. If you want to test the waters before committing, explore the free online phone number page to understand availability and coverage.
Stuck on a code that won't arrive?
If a code fails, don't burn time debugging a dead number. Request a fresh one, and if it still doesn't land, the refund policy has you covered. Higher acceptance starts with the right number choice. Browse available numbers to find one that works for your app.
Key Takeaways
The Dropverse SMS verification API lets developers request virtual numbers, poll for OTPs, and release numbers programmatically across 200+ countries.
Number allocation is instant after payment; code delivery typically takes 5–15 seconds for major apps like WhatsApp, Telegram, and Google.
You pay per activation (around $0.10) with a refund if no code arrives, and crypto payments keep checkout fast and private.
Rental options (1, 3, 7, or 30 days) support repeat OTPs for long-running test cycles.
Poll at 3-second intervals for the best balance of responsiveness and API efficiency.
Debug systematically: check the sender first, verify your number ID, then investigate carrier delays before requesting a refund.
Compliance note: PVAPins is not affiliated with the app/website or platform. Please follow each app/website’s terms and local regulations.
Last updated:
Ready to Keep Your Number Private in Dropverse?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Alex Carter
Alex Carter is a digital privacy and online security writer with over 7 years of hands-on experience in cybersecurity, virtual number services, and identity protection. Based in Austin, Texas, Alex has spent the better part of a decade helping individuals and businesses navigate the often-confusing world of SMS verification, burner numbers, and account security — without sacrificing ease of use.
At PVAPins.com, Alex covers everything from step-by-step guides on verifying Telegram, WhatsApp, Gmail, and social media accounts using virtual numbers, to deep dives into why protecting your personal SIM matters more than ever. His articles are grounded in real testing: every tool, method, and tip Alex recommends is something he has personally tried and vetted.
Before joining PVAPins, Alex worked as a freelance cybersecurity consultant, auditing online account practices for small businesses and helping clients understand the risks of tying sensitive services to personal phone numbers. That experience shapes how he writes — clear, practical, and always with the real user in mind.
When he's not writing or testing verification workflows, Alex spends time contributing to privacy-focused forums, following developments in data protection law, and helping everyday users understand their digital rights. His core belief: online security shouldn't require a tech degree — and with the right tools, it doesn't.