Dosi Citizen SMS Verification API: Automate OTP Integration
Quick answer: To verify Dosi citizen with a virtual number, choose a country on PvaPins from $0.12, enter that number as your Dosi citizen phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
How it works
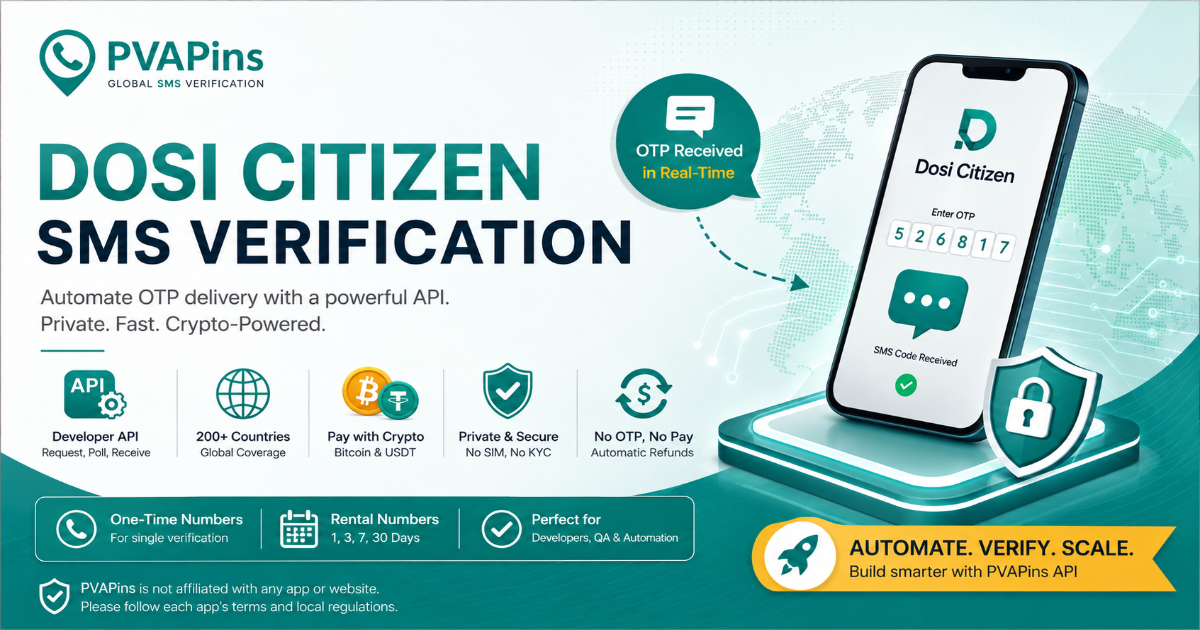
Request a number send an HTTP call with your API token, the Dosi Citizen service code, and a country code.
Poll for status loop the endpoint at your chosen interval until the SMS status changes to "received." Polling intervals are adjustable every 2 seconds or every 10, depending on delivery speed.
Retrieve the OTP parse the JSON response to extract the message body and code. Webhook-style responses are also available for event-driven architecture.
Test with a low-cost activation verify the flow with a single activation before scaling to high volume.
Wire it into your test suite place the API call in the QA login script that feeds your Dosi Citizen test cases. See the real-time SMS verification API documentation for both patterns.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
USA high-volume support for frequent activation cycles and bulk testing.
UK & Canada consistent availability for English-language workflows.
India variable availability depending on telecom rotations; plan for fallback countries when demand spikes.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about Dosi citizen SMS verification.
Is using a virtual number for Dosi Citizen verification against the law?
No, using a virtual number is legal in most countries as long as you aren't defrauding anyone or violating Dosi Citizen's terms of service. Check the platform's terms and local regulations before relying on any temporary number. PVAPins is not affiliated with any app or website.
Why does my Dosi Citizen OTP sometimes not arrive?
OTP failures can happen if the platform has blocked a certain carrier range, or if the number was recycled too soon. Refreshing to a new number usually resolves it. PVAPins provides a refund if no SMS is delivered.
Should I use a one-time number or a rental number for Dosi Citizen?
Choose a one-time number for initial verification only. If Dosi Citizen will ask for re-authentication later, rent a number for 1, 3, 7, or 30 days. Rentals make repeat verification seamless.
What should I NOT use temp numbers for?
Do not use temporary numbers for account recovery of critical personal accounts, identity authentication that requires verified personal data, or any activity that violates spam or anti-fraud regulations. Use them for testing, trials, and legitimate automation where disposable verification is appropriate.
Can I get a refund if the Dosi Citizen OTP never arrives?
Yes, if no code is delivered within the specified window, the activation qualifies for a refund. The credit is automatically returned to your PVAPins balance, so you don't need to submit a ticket.
Can I pay for Dosi Citizen verification with Bitcoin or USDT?
Yes, PVAPins accepts Bitcoin, USDT, and several other crypto gateways for top-ups and direct number purchases. This keeps your checkout anonymous and fast.
Read more: Full Dosi citizen SMS guide
Open the full guide
If you're building automation around Dosi Citizen account verification, you know the pain of manual OTP entry. This guide shows you how to receive Dosi Citizen SMS codes programmatically through a developer API, with private crypto payments and no personal SIM required.
This article is for developers, QA engineers, and automation builders who need a reliable way to handle Dosi Citizen OTP delivery without exposing their real phone number. You'll learn when to use a one-time number versus a rental, how the API flow works, and how to pay with Bitcoin or USDT.
Quick Answer:
Automate Dosi Citizen OTP receipt by requesting a virtual number via API and polling for the incoming SMS code.
Use a one-time number for a single verification; rent a number for 1, 3, 7, or 30 days if Dosi Citizen will re-authenticate later.
Pay with Bitcoin or USDT for private, instant checkout; no credit card or KYC required.
Coverage spans 200+ countries including the USA, UK, Canada, Germany, Australia, and India, subject to live carrier inventory.
If no OTP arrives within the defined window, you get a refund automatically no hidden fees, no subscription.
What Is Dosi Citizen SMS Verification and Why Automate It?
Dosi Citizen is a digital identity and citizenship platform that requires phone number verification via SMS OTP during onboarding or account recovery. Automating this with an API removes manual copy-paste workflows, minimizes human error, and lets developers integrate SMS receipt directly into their test suites, QA pipelines, or account-provisioning logic. Using a virtual number keeps your personal SIM out of the loop and protects your privacy.
Manual verification slows down bulk operations, especially when you're iterating on test accounts or running regression suites.
Here's why automation matters:
Dosi Citizen sends a one-time passcode (OTP) to validate the user's phone number.
Manual copy-paste of codes breaks automation flows and blocks CI/CD pipelines.
An API-driven approach polls for the SMS and retrieves the code in real time.
Virtual numbers prevent your real mobile number from being tied to repeated test signups.
Use cases include app testing, QA automation, and legitimate account provisioning workflows.
If you're building integration tests that need to verify Dosi Citizen's onboarding flow repeatedly, a scripted OTP retrieval is the only scalable path.
How the Dosi Citizen OTP API Integration Works
Integrating the Dosi Citizen OTP API follows a straightforward request-and-poll model: you request a number via an HTTP call, configure the activation for Dosi Citizen, and then poll the API endpoint until the SMS arrives. Once the code lands, the API returns it so your script can parse and submit it automatically. This method is built for speed and reliability, with no need to open a dashboard or handle SMS manually.
The flow typically involves three steps:
Request a number: send an HTTP call with your API token, the Dosi Citizen service code, and a country code.
Poll for status: loop the endpoint at your chosen interval until the SMS status receive OTP online.
Retrieve the OTP; parse the JSON response to extract the message body and code.
API endpoints accept parameters like country, service, and operator. Polling intervals are adjustable to match your automation tolerance; some teams hit the endpoint every 2 seconds, others every 10, depending on how fast Dosi Citizen delivers.
For developers who prefer event-driven architecture, webhook-style responses are available to push the SMS content to your server as soon as it lands, instead of polling. The real-time SMS verification API integrate documentation covers both patterns in detail.
A simple cURL example (using the official cURL documentation as a reference) shows how to fetch a number and the incoming SMS text:
Key Features of a Developer API for Dosi Citizen OTP
A production-grade API for Dosi Citizen verification includes instant number delivery, real-time SMS polling, broad global numbering, and flexible crypto payment rails. Developers should look for simple HTTP verbs, clear JSON responses, and transparent error codes that make debugging easier. The best APIs also offer full documentation and no hidden fees tied to failed activations.
Instant number assignment: your script never hangs waiting for inventory.
Real-time polling endpoints return SMS content as soon as it arrives, with millisecond timestamps.
Country-level and service-level numbering selection gives you fine-grained control over which market your test simulates.
Crypto checkout via Bitcoin and USDT enables private, fast top-ups without KYC.
Pay-as-you-go pricing with no subscription overhead; you pay only for what you use.
A robust dashboard displays usage history and balance in one view for reconciliation.
You want an API integrate that fails loudly with precise error codes, not one that silently returns empty responses. Transparent error handling saves hours of debugging when a carrier route goes dark.
How to Automate Dosi Citizen Verification Programmatically
Automating Dosi Citizen verification means replacing manual code entry with a script that handles number assignment, OTP retrieval, and submission. You can write it in any language that supports HTTP requests, and the flow is consistent enough to embed in unit tests or CI/CD pipelines. The goal is to eliminate human presence from the verification loop entirely.
Here's a practical checklist for your automation:
Store your API token in environment variables; never hardcode it in source.
Loop the polling endpoint with a timeout so your script fails predictably if no SMS arrives.
Parse the response JSON to extract the code field for downstream automation.
Use a number that isn't linked to your personal identity for every test run.
Add retry logic with exponential backoff to handle temporary network or latency hiccups.
Pair this flow with your CI/CD pipeline so every build that touches Dosi Citizen registration actually verifies the end-to-end path.
Your automation should also log every activation number, country, timestamp, and delivery latency so you can spot trends. If delivery times creep up, you can switch countries or numbers preemptively via the incoming SMS platform dashboard.
Geo Coverage: Dosi Citizen SMS Verification in USA, UK, Canada, Germany, Australia, and India
Virtual numbers for verification are available for Dosi Citizen verification across major markets including the USA, UK, Canada, Germany, Australia, and India. Availability can fluctuate based on carrier inventory and platform demand, so check the live service list before automating. For teams running global QA or multi-region account testing, this reach is essential.
Here's what to expect per market:
USA: high-volume support for frequent activation cycles and bulk testing.
UK & Canada: consistent availability for English-language workflows.
Germany & Australia: solid coverage for EU and APAC-specific testing scenarios.
India: variable availability depending on telecom rotations; plan for fallback countries when demand spikes.
The PVAPins dashboard shows live availability per country before checkout, so you don't commit funds to a dead route. Check it before you script a new region.
Pay for Dosi Citizen Verification with Bitcoin and USDT: Anonymous Checkout Explained
PVAPins Android app supports cryptocurrency payments for Dosi Citizen numbers, and checkout via Bitcoin, USDT, and other major gateways skips the need for traditional card processors. Crypto settlements keep the transaction private and avoid linking your purchase to a banking profile. Top-ups are credited instantly, and you pay only for the number and incoming SMS.
Here's how it works:
Bitcoin and USDT (TRC-20 or ERC-20) are accepted across all services.
No KYC is required at any stage of the purchasing flow.
Funds land in your automation proceeds instantly.
Refunds on invalid activations return to your balance in equivalent crypto value.
Anonymity layers: the disposable number itself and the payment method both protect your identity.
This model is built for developers who don't want their verification habits tied to a bank statement. Head to the crypto pricing and top-up page to see current rates per activation, starting around $0.10.
One-Time Numbers vs. Rental Numbers for Dosi Citizen
A one-time number is ideal for a single verification event where the platform won't demand re-authentication later. If Dosi Citizen requires additional OTPs for password resets or login checks later, a rental number with 1, 3, 7, or 30-day access provides a persistent receiving line. Choosing the right model up front prevents failed re-verifications.
One-time numbers are sufficient for initial signup or a single QA test run.
Rental numbers give you the same number across multiple verification sessions.
Repeat OTPs on one-time numbers trigger additional costs; rentals avoid that surprise.
Rentals work best for ongoing QA, beta testing, or long integration testing windows.
Your project roadmap should dictate whether flexibility or minimal cost wins.
If you only need to verify one account once, grab a temp number for one-time Dosi Citizen verification. But if your test suite will re-authenticate users repeatedly for password resets, login flows, or device checks, the math favors renting phone numbers.
Troubleshooting Common Dosi Citizen OTP Failures
OTP delivery failures happen when a platform rotates carrier routes, blocks an entire number range, or detects unusual traffic from a region. If no code arrives after your polling timeout, the first remedy is to refresh to a different number. When a refund is warranted, the PVAPins refund policy covers undelivered SMS.
Work through this checklist when codes don't land:
Double-check the service code; confirm the selected service matches Dosi Citizen for your chosen country.
Refresh to a new number after one failed delivery; don't loop the same activation; request a fresh one.
Lengthen your polling timeout; some platforms take 60-90 seconds to send, and premature failure is a common mistake.
Check the refund window: if the SMS never arrives, the activation qualifies for an automatic refund.
Clear caches on the platform side; browser caches and app-side throttling can delay receipt independently of your setup.
Persistent issues with a specific country route? The refund and service guarantee policies page outlines how to request route adjustments or get your balance credited.
Is Using a Temporary Number for Dosi Citizens Legal and Safe?
Using a temp number is legal in most jurisdictions as long as you aren't abusing platform rules or committing fraud. The main restriction comes from Dosi Citizen's own terms of service, which may prohibit disposable numbers for certain account types. Check applicable local regulations and the platform's policy before proceeding.
Legality depends on the platform's terms and your end use case.
Testing and QA use cases are widely accepted across the development community.
Fraud, spam, or identity deception violates our acceptable use policy and the law.
In the UK/EU, the ICO's guidance on data protection and identity verification frames how identity data should be handled.
In the US, the FTC's fraud prevention resources outline what constitutes identity misrepresentation.
Follow OWASP's SMS verification security recommendations when building your automation to avoid common pitfalls.
Step-by-Step: Building the Dosi Citizen Verification Flow with PVAPins API
Start by creating a PVAPins account and topping up via Bitcoin or USDT, then grab your API token from the dashboard. From there, call the number-request endpoint with the Dosi Citizen service code and a country code, then poll until the SMS appears. This flow takes less than five minutes to wire up and removes all manual steps.
Create an account at PVAPins, top up with crypto, and confirm your balance is active.
Locate your API token in profile settings and store it securely in your app config.
Request a number: call the endpoint with the Dosi Citizen service code and your target country.
Poll the OTP endpoint in a loop until the SMS arrives, then parse the JSON response.
Test with a low-cost activation; verify the flow with a single activation before scaling to high volume.
Wire it into your test suite; place the API call in the QA login script that feeds your Dosi Citizen test cases.
Test the API with a free phone number for sms now: Explore Dosi Citizen number availability at zero risk. Create an account and browse live service coverage before you commit funds. Monitor your dashboard to track number status and code retrieval in real time.
Key Takeaways
Automating Dosi Citizen OTP retrieval eliminates manual copy-paste and human error from your verification workflows.
The request-and-poll API model is simple to implement in any language that supports HTTP calls.
One-time numbers work for single events; rental numbers (1, 3, 7, or 30 days) handle repeat re-authentications reliably.
Bitcoin and USDT checkout keeps payments private, instant, and free of KYC requirements.
Refund policies cover failed deliveries, so your downside risk is minimal.
Compliance note: PVAPins is not affiliated with the app/website or platform. Please follow each app/website’s terms and local regulations.
Last updated:
Ready to Keep Your Number Private in Dosi citizen?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Mia Thompson
Mia Thompson is a content strategist and digital privacy writer with 5 years of experience creating in-depth guides on online security, virtual number services, and SMS verification. At PVAPins.com, she specializes in breaking down technical privacy topics into clear, actionable advice that anyone can apply — no IT background required.
Mia's work covers a wide range of real-world use cases: from setting up a virtual number for app verification, to protecting your identity when creating accounts on social media, fintech platforms, and messaging apps. She researches every topic thoroughly, personally testing tools and workflows before writing about them, so readers get advice that's grounded in actual experience — not just theory.
Prior to focusing on privacy content, Mia spent several years as a digital marketing strategist for SaaS companies, where she developed a strong understanding of how platforms collect and use personal data. That experience sparked her interest in privacy tech and shaped the reader-first approach she brings to every piece she writes.
Mia is especially passionate about making digital security accessible to non-technical users — particularly people who run small businesses, manage multiple online accounts, or are simply tired of exposing their personal phone number to every app they sign up for. When she's not writing, she's testing new privacy tools, reading up on data protection regulations, or thinking about ways to simplify complex security concepts for everyday readers.