Dolphin Flight Language SMS Verification Cost
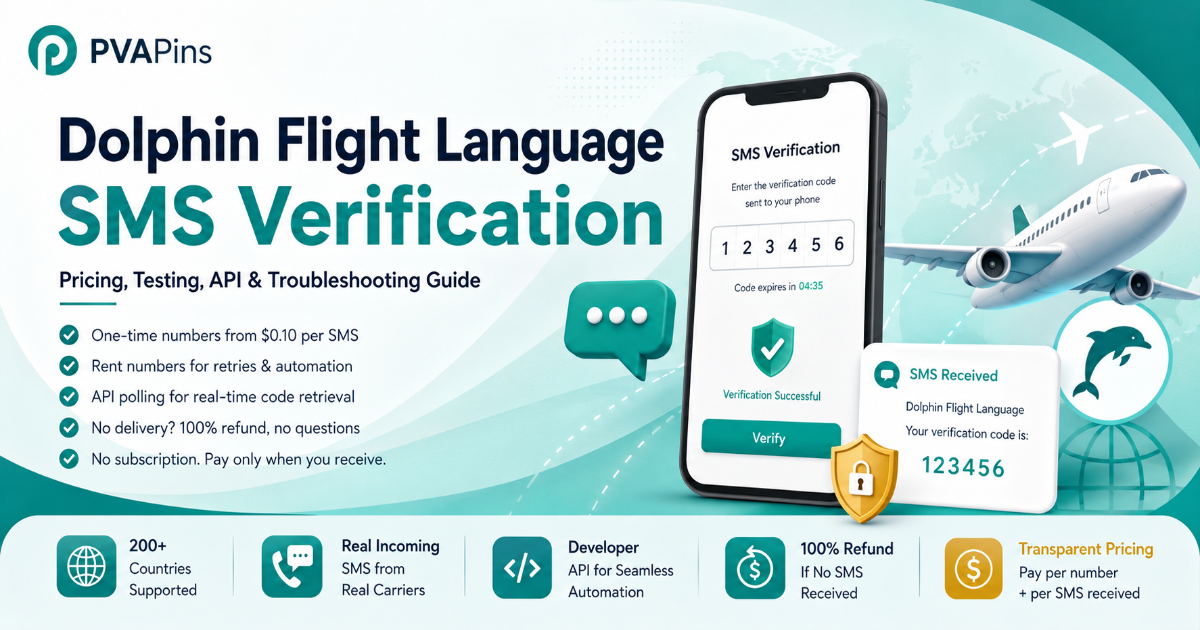
Quick answer: To verify Dolphin Flight Language with a virtual number, choose a country on PvaPins from $0.12, enter that number as your Dolphin Flight Language phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
How it works
Purchase or rent a number from the receive SMS page. Use one-time activation for single-shot tests, or rent 1–3 days for resend testing.
Copy the number into your app's signup/login form in your test environment and trigger the OTP send exactly as a real user would.
Check the real-time SMS inbox for manual verification, or call the API integration endpoint to poll for the incoming message programmatically.
Extract the OTP from the SMS body using a regex match (for example, CODE: [\d]{6} or verification code is \d{4,8}), then feed it back into your app's verification form and assert that authentication succeeds.
Log the full round-trip time from "Send OTP" to "Code received" to catch latency regressions in your app or the SMS gateway.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
OTPs often arrive as CODEor verification code is parse with a broader regex to handle encoding mismatches.
Match number country to what the app is likely to accept some apps geo-fence signups by IP or number country.
Numbers from low-cost regions (Southeast Asia, Eastern Europe, some African countries) cost less than premium geos like the US, UK, or Canada.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about Dolphin Flight Language SMS verification.
Is Dolphin Flight Language SMS verification "legal" to use?
Yes, in most contexts, evaluating your own app's signup or verifying your own account is legitimate. But it must not violate the app's terms. PVAPins does not support fraud or spam, and you are responsible for following each app's terms of service. PVAPins is not affiliated with any app or website. Please follow each app's terms and local regulations.
Why do SMS codes sometimes fail to arrive when testing?
Common causes: the app's sender shortcode is blocked by the covered routing, the source number doesn't allow port switching to your chosen country, or your code expired before you checked it. OTP time-to-live is often 10 minutes or less. Check the API endpoint's store log or retrieval status to see if the message vanished within the carrier.
Should I buy a one-time number or rent a number for Dolphin Flight Language test automation?
A one-time "burner" works if you only test a single verification. If resend windows recover the same number for multiple attempts, or you're repeatedly logging in more than 3–5 times, a 1-day or 7-day rental avoids frustration. For cyclical QA suites, rent 7 days.
Can I use a temporary number for my personal accounts?
You can, but be cautious. Don't use it for 2FA on financial accounts, emergency recovery on company accounts, or to bypass identity verification systems. Fraud gets flagged. Also, don't plan multi-login lifetime persistence on a disposable number; use repeat rentals for anything that needs to last.
How do I troubleshoot a failing code from PVAPins?
First, check that the service and country coverage are green for your target app. Second, poll the retrieval endpoint to confirm the message status. If pending or failed, retry with a new activation or switch countries. If no delivery occurs, PVAPins refunds your cost; your spend is zero under the non-delivery policy.
Is there a monthly subscription required?
No. PVAPins has no subscription model. You pay per number and per received SMS. If you don't use the platform, you don't pay. Top-ups are handled via cryptocurrency for fast, private checkout.
What's the difference between a "received" status and a "delivered" status?
"Delivered" means the carrier accepted the message for routing. "Received" means the message actually arrived at our infrastructure and is available in your inbox. Always check for "received" status before declaring a test failure; sometimes messages show "delivered" but arrive seconds or minutes later.
Read more: Full Dolphin Flight Language SMS guide
Open the full guide
If you're building or QA-testing a flight-crew training app like Dolphin Flight Language, you already know the drill. SMS verification codes are woven into your signup and login flows, but testing them? That can spiral into a mess of expenses, delays, and pure frustration. You need incoming OTPs that arrive reliably, cost predictably, and don't force you to sacrifice your personal SIM or watch your dev environment get rate-limited into oblivion.
This guide is for developers, QA engineers, and product testers who need to simulate real user behaviour against Dolphin-like SMS verification flows. We'll break down what drives pricing, how to run cost-effective tests, how to retrieve codes programmatically, and what to do when codes ghost you.
Quick Answer:
One-time Dolphin Flight Language SMS verification numbers start around $0.10 per activation on PVAPins. You pay per number plus per received SMS that's it.
Rental numbers (1, 3, 7, or 30 days) are the smart pick for retry-heavy flows, multi-step onboarding, or CI pipelines that need the same number across multiple OTPs.
API polling pulls codes programmatically in seconds. Dashboard receipt works fine for manual testing.
If a code never shows up, PVAPins refunds the cost: no subscription, no upfront fees, no drama.
Always test against a dedicated virtual number, never your personal SIM, to dodge blocking, spam loops, and data leakage.
Why Your Dolphin Flight Language SMS Verification Number Price Varies
The price you'll see for a Dolphin Flight Language (or any similar flight-crew training app) SMS verification number boils down to three things: whether you're grabbing a one-time activation (around $0.10 per code) or renting a number for repeated OTPs, the destination country's SMS gateway fees, and whether the app sends a single SMS or also triggers a voice-call fallback.
Most platforms won't show you a flat price because carriers in different countries charge different rates for inbound SMS. On the PVAPins Android app, you pay per number plus per received SMS, so a test cycle rarely costs more than a few cents if you're selective about what you buy.
What Actually Determines the Cost
One-time vs. rental: One-time activations are the cheapest per test. Rental plans 1, 3, 7, or 30 days make sense for apps with repeated OTPs or auto-resend windows. If your test needs exactly one code, a one-time number does the job. If you're hammering the resend button eight times in an hour, a rental saves real money.
Country variance: Numbers from low-cost regions parts of Southeast Asia, Eastern Europe, and some African countries- cost less than premium geos like the US, UK, or Canada. Pick a region based on what the app you're testing is likely to accept. Some apps geo-fence signups by IP or number country, so match your test setup accordingly.
Hidden fees: Watch out for fees on "no retrieval," meaning if the code gets sent and you miss it, some providers charge you for the status check instead of the SMS itself. PVAPins doesn't play that game. You pay only when the code arrives. Check the live rate page to see current per-country pricing before you commit.
Here's the operational reality most dev teams miss: overspending on SMS verification isn't usually about the per-code price being high. It's about buying numbers in bulk, using them once, and letting them expire. That's the cost killer, not the $0.10 activation fee.
Cheap Dolphin Flight Language SMS Verification Number: How to Cut Costs Without Breaking Your Test Flow
Going cheap is straightforward if you skip high-demand bulk numbers and stick to per-activation pricing instead of subscriptions. The biggest cost pitfall in Dolphin flight app testing is overbuying: grabbing a number, using it once, then watching it expire with zero codes received.
Use disposable numbers only for the transaction you're running right now. If you're testing retry flows, phone number rental service a 1-day number instead of burning a fresh activation every time.
Practical Cost-Saving Tactics
Use a "rent" option (single-day) if your test involves multiple SMSes across time, or if the app sends a new OTP after a 5-minute resend window. A 1-day rental usually costs less than five separate one-time activations.
Order numbers in batches, but only what you actually need. Never pre-order hundreds of numbers if your test volume doesn't demand it. Unused numbers still cost money. Run a cost-per-successful-verification calculation before bulk ordering.
Look for "no-fee" plans where you pay only for receiving an SMS. Don't pay for an unused number. PVAPins charges you only on "receive" to keep costs flat; if no SMS lands, you pay nothing.
Match number quality to test importance. Use the most affordable temp number for smoke tests and low-stakes flows. Reserve premium numbers for tests where delivery reliability is genuinely critical.
Track your spend per test suite. A simple spreadsheet mapping test case → number → cost per received code will show you exactly where money leaks.
Cheap doesn't mean unreliable. It means buying the right type of number for the specific test you're running, not defaulting to the most expensive option out of habit.
Dolphin Flight Language SMS Flow Testing: Step-by-Step for QA Teams and Developers
The flow for testing SMS-based Dolphin flight verification looks like this: (1) buy or rent a disposable number; (2) in your app build, trigger a send-OTP request; (3) receive the verification code via webhook or poll the API integrate for the incoming message; (4) assert the OTP against your test expectations.
For an automated suite, you'll want a way to trigger the OTP send and poll the platform for code retrieval rather than delegating manual verification. A developer API lets you ingest the exact SMS text into your test runner.
Step-by-Step Pipeline
Purchase or rent a number from the receive SMS page. For single-shot tests, use one-time activation. For resend testing, rent for 1–3 days.
Copy the number into your app's signup/login form in your test environment. Trigger the OTP send exactly as a real user would.
Check the real-time SMS inbox for manual verification, or call the API integration endpoint to poll for the incoming message programmatically.
Extract the OTP from the SMS body using a regex match (for example, CODE: [\d]{6} or verification code is \d{4,8}).
Feed the OTP back into your app's verification form and assert that authentication succeeds.
Log the full round-trip time from "Send OTP" to "Code received" to catch latency regressions in your app or the SMS gateway.
Mock failure paths by entering a wrong code, an expired code, or requesting a resend. Confirm your app handles each error state gracefully.
When Testing Retry and Resend Flows
When the app's "resend" timer is clicked, account for platform uptime; use a 3-day rental so the same number stays valid for all retry SMS flow tests. Some apps rate-limit resends per number, so having a stable number lets you test those limits accurately.
Try our real-time inbox instantly. Run a smoke test for $0.10 no subscription, no commitment.
Test the SMS by Purchasing a Number →
Test Dolphin Flight Language SMS Verification: The Complete Incoming Code Checklist
A robust smoke test for a Dolphin-like flight/crewing app should verify that an OTP matched the expected string pattern, then trigger a wrong-code path. Use a "test account" if the app supports it; if not, use a fresh temp number for each full QA pass.
PVAPins' SMS verification panel lets you retarget numbers and track what happened delivered or timed out across multiple browsers and traffic sources.
Pre-Test Checklist
Confirm the target app is covered for your chosen country. Check current coverage before buying.
Select the right number type: one-time for single verification, rental for multi-step or retry tests.
Open the dashboard or configure API polling before triggering the OTP.
Verify the phone number in your test is active and not previously used for the same app (to avoid "already registered" errors).
During-Test Checklist
Trigger OTP from the app's actual UI, not by directly calling internal APIs (unless that's what you're testing).
Check SMS text triggers are parsed correctly, especially for prefix codes like CODE: [\d]{6} vs. verification code vs. bare numeric strings.
Measure delivery time from "Send OTP" to "Code received in dashboard/API." Flag anything over 60 seconds for investigation.
Validate retry limits. Know whether the app permits sending to the same number more than 2–3 times per hour. Some apps allow 3–5 resends.
Track "timeout" status to see whether the number remains hot after a failed attempt. Only some apps resend within a 2-minute rewindow.
Post-Test Checklist
Confirm the code was consumed correctly and the app transitioned to the expected next screen.
Verify that entering an old or wrong code produces the correct error state.
Check the number's status post-test; release it if it's one-time use, or keep it if you're running more tests.
Log the full test results, including delivery time, parsing success, and any anomalies.
Note on free numbers: When using a free phone number for sms option just for testing, acceptance rates can be lower. Match tests with paid-only numbers to ensure codes aren't swallowed by shared or exhausted numbers.
Handling Dolphin Flight Language Incoming SMS Verification: Retry Logic and Timeout Settings
Most apps send one OTP, wait 60–90 seconds, and ask for a resend. If delivery is slow, your code can expire in flux. To handle this, build your test to use delivery hooks from the SMS provider: check your status endpoint for "received" status changes, not just "status delivered."
If no code arrives in 3–5 minutes, trigger a "retry" with the same number, not a fresh one, to emulate real user behaviour. You'll only need a rental for that.
Retry Logic That Works
Always map inbox delivery time for reporting: Unflagged = under 3 minutes. Flagged = over 3 minutes. Log both.
Use the same number for retries. A fresh number each retry wastes money and doesn't match real user behaviour.
If using external webhooks, code to catch a third-party webhook gateway failure; don't block your main test suite on a webhook that may be down.
Know the time-to-live window. If you get a number from a "buy" type, understand the 30-minute window before the number expires. Kick off long tests accordingly.
Switch countries if the app gives a "No route" error. Some route-less numbers don't connect to certain carriers.
Timeout Settings for Automated Tests
For automated QA, set your polling timeout based on typical delivery windows. If your provider reports "waiting" status, keep polling for up to 5 minutes. If no success=True response arrives, fail the test and log the failure reason.
This is where the OTP verification handling workflow matters: you need a system that shows you not just whether a code arrived, but where in the delivery chain it stalled.
Managing Dolphin Flight Language Verification Codes: Organizing Numbers Across Test Environments
In a busy QA build, you often have 10+ test cases needing Dolphin app SMS codes at the same time. Avoid letting a "true" active permanent SMS QR code get into automated code; instead, buy and seal a "rent-only" mode where each code holds a separate 30-day temp number map specific to a test case.
PVAPins' dashboard lets you store that mapping, pull the exact receipt from your API, and release the number after your run.
Organizing Your Test Matrix
Create a test case matrix per product line. Map each GUI flow to its corresponding number: the "checkout" test uses checkout-temp-number; when tracking Test-User #001, your number ID is logged alongside the test case.
Use free and public numbers for local dev (with .env entry variables). Use real, paid numbers for CI or higher-confidence runs.
Set up a "pool" of codes held for delayed results. The PVAPins API filters by order ID to pull back a specific string vs. test strings.
For cleanup, release numbers after the 7-day "rent" default only if your team's full suite has returned. Don't hold numbers you're not actively using.
Why Organization Matters
Disorganized number management is a silent money leak. Every number you forget to release costs you money. Every mapping you lose means a code goes unclaimed and a test fails for no reason. A simple spreadsheet or a field in your test runner.
Retrieving Dolphin Flight Language OTP: API Polling vs. Dashboard Receipt
There are two ways to pull the code: check the dashboard UI after a refresh, or call the "Get message" endpoint to fetch the status of an inbound SMS. On PVAPins, using the developer API is the fastest way: make a GET request with the number's ID and get your SMS text from 200+ connectors.
The code arrives, but you can also consume the callback in your app by subscribing to the number's webhook in API Integration.
API Polling
The full code sits in a JSON result. Parse the "body" string with a regex match to extract the OTP.
Supports 40–50 requests per minute for event retrieval; no global poll hash needed.
API responses include status codes like "waiting" or "verified"; you can synthesize a test timeout: start a timer; if no success=True within 5 minutes, error out.
Ask for "code receive permission" without 2FA despite the check-code trace; retrieve it via REST and generate your test report.
Dashboard Receipt
Log in, navigate to your purchased numbers, and view the SMS log per number.
Real-time updates show incoming messages without manual refresh.
Useful for exploratory testing, debugging, or one-off verifications.
Not ideal for automated test suites; use the API for anything that needs to run repeatedly.
Which One Should You Use?
Use API polling when you're running automated tests, CI pipelines, or any flow that needs code retrieval without human intervention. Use the dashboard for quick manual checks, debugging a failure, or when you're exploring an app's behaviourr before writing automated tests.
Dolphin Flight Language SMS Testing Developers: Avoiding the Number Burn Trap
If you don't use one-time numbers correctly, you'll get your app's IP blocked on the platform's SMS pipeline. A developer who uses a personal SIM for testing will burn it. All marketing, sign-in, and onboarding loops send codes to the same number, so any misuse becomes your real number's pain.
This is the danger. Use a dedicated temp number pool for testing and release components back into the pool or discard them; never keep a personal SIM on that testing path.
What "Number Burn" Looks Like
App providers flag your personal number as a test number, so future legitimate signups from that number are blocked.
Your dev environment's IP gets rate-limited because repeated OTP requests from the same source look like abuse.
Your carrier flags your account for unusual SMS volume, potentially suspending service.
How to Avoid It
Use dedicated temp numbers for all testing. Never mix test traffic with personal or production numbers.
Test only legitimate use cases. Do not test fraud. Test your own app's flows, never banned requests. Abusing test numbers harms the broader pool for everyone.
Avoid sharing numbers across concurrent test threads. Two flows using the same number at the same time can dead-end. Spot-check your test matrix for collisions.
Map each country vs. app checkbox to a specific test profile. Avoid cross-suite collisions by isolating number assignments per test case.
If you need stable inputs for repeat OTP callbacks, use a 3-day rental: fixed number, stable test conditions, no surprises.
The bottom line: your personal SIM is not a testing tool. It's an identity anchor. Protect it.
Dolphin Flight Language SMS Verification Handling: The Troubleshooting Guide for Failed Codes
Even with a good provider, you'll occasionally face a "code not received" state. Common causes include the app not being on the covered services list, the source country banning low-cost numbers (especially for healthcare-like apps with manual moderation), or shortcodes that reject generic SMS if the app sends via a premium short code.
Always start by checking the app's one-time login threshold against PVAPins' coverage or variable failed-status screen, then move on to network-level price and country mitigation.
Troubleshooting Flow
Check the delivery status. Pull the checkStatus log from the dashboard or API. Number 0 = normal; 1 = failed; 2 = expired; 3 = dropped by carrier. Report any 3-status errors.
If failure is consistent, choose an alternate country code for the target service. Some apps route differently by country.
If a shortcode sends a premium SMS link (don't use for OTP), some apps fall back to multi-step API verification; pick the appropriate string in your test.
If no receipt occurs (rate-limit), restart a new number from a fresh slot. If a receipt never arrives, you need to adjust your flow.
Dolphin Flight Language SMS Code Receipt: What Actually Happens After Payment
Here's the exact flow when you use PVAPins for a Dolphin Flight Language number: the app triggers its SMS gateway (Twilio, generic shortcode system, or carrier direct). We archive the job on your dashboard, fetch a 30-day code, and the number returns as "active" instantly.
When your code sends only when the carrier delivers, you'll see it via the events streaming row. If your app needs a clean pass, we handle encodings. You can use the same number multiple times within the rental window for all customizations.
What Happens Step by Step
You purchase a number (one-time or rental). Payment typically clears via crypto (Bitcoin, USDT) for speed and privacy.
We deliver the number instantly to your dashboard. No waiting, no manual provisioning.
You trigger the OTP in your app. The app's SMS gateway routes the message to our receiving infrastructure.
The carrier delivers the SMS to the number. We capture the message body, sender ID, and timestamp.
The code appears in your dashboard and is available via API polling within seconds.
You extract the OTP and complete verification in your app.
The number stays active for the rental period (or expires after one-time use).
The Refund Mechanism
After you pay, the order is final and non-refundable unless no code is delivered. If the SMS never arrives, you receive an automatic refund. That straightforward policy verifies the buying process and removes risk from your test budget.
Developer Tip: Log Sender Metadata
The opaque API history helps catalogue sender "message part count" vs. delivery provider for your compliance timeline. If you're testing in a regulated industry or need audit trails, pull these details and store them alongside your test results.
In for long queues, long SMS retries, or automated RRD? Grab a 24-hour rental where the number lasts for any repeat OTP.
Rent 1/3/7 Days →
Key Takeaways
Pricing is transparent and usage-based. You pay per number plus per received SMS. No subscription, no hidden fees, and automatic refunds if a code never arrives.
One-time numbers suit single verifications. Rentals (1–30 days) suit repeat OTPs, retry flows, and CI pipelines that need the same number across multiple tests.
API polling beats dashboard refresh for automation. Integrate code retrieval into your test runner for 1–3 second retrieval and full flow automation.
Match number quality to test importance. Use cheap numbers for smoke tests and premium numbers for critical-path validation.
Never test with your personal SIM. Dedicated temp numbers protect you from carrier blocks, app bans, and data leakage.
Organize your test matrix. Map each test case to a specific number ID, track costs per suite, and release numbers when done.
Compliance note: PVAPins is not affiliated with the app/website or platform. Please follow each app/website’s terms and local regulations.
Last updated:
Ready to Keep Your Number Private in Dolphin Flight Language?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Ryan Brooks
Ryan Brooks is a tech writer and digital privacy researcher with 6 years of experience covering online security, virtual phone number services, and account verification. He joined PVAPins.com as a contributing writer after years of working independently, helping consumers and small business owners understand how to protect their digital identities without relying on personal SIM cards.
Ryan's work focuses on the practical side of online privacy — specifically how virtual numbers can be used to safely verify accounts on platforms like WhatsApp, Telegram, Facebook, Google, and hundreds of other apps. He tests these workflows regularly and writes only about what actually works in practice, not just theory.
Before transitioning to full-time writing, Ryan spent several years in IT support and network administration, which gave him a deep, first-hand understanding of the vulnerabilities that come with exposing personal phone numbers to third-party services. That background is what drives his passion for educating readers about safer alternatives.
Ryan's guides are known for being direct and jargon-free. He believes privacy tools should be accessible to everyone — not just developers or security professionals. Outside of work, he keeps tabs on data privacy legislation, follows cybersecurity research, and occasionally writes for privacy-focused communities online.