The Developer's Guide to dobiQueen SMS Verification API
Quick answer: To verify dobiQueen with a virtual number, choose a country on PvaPins from $0.54, enter that number as your dobiQueen phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
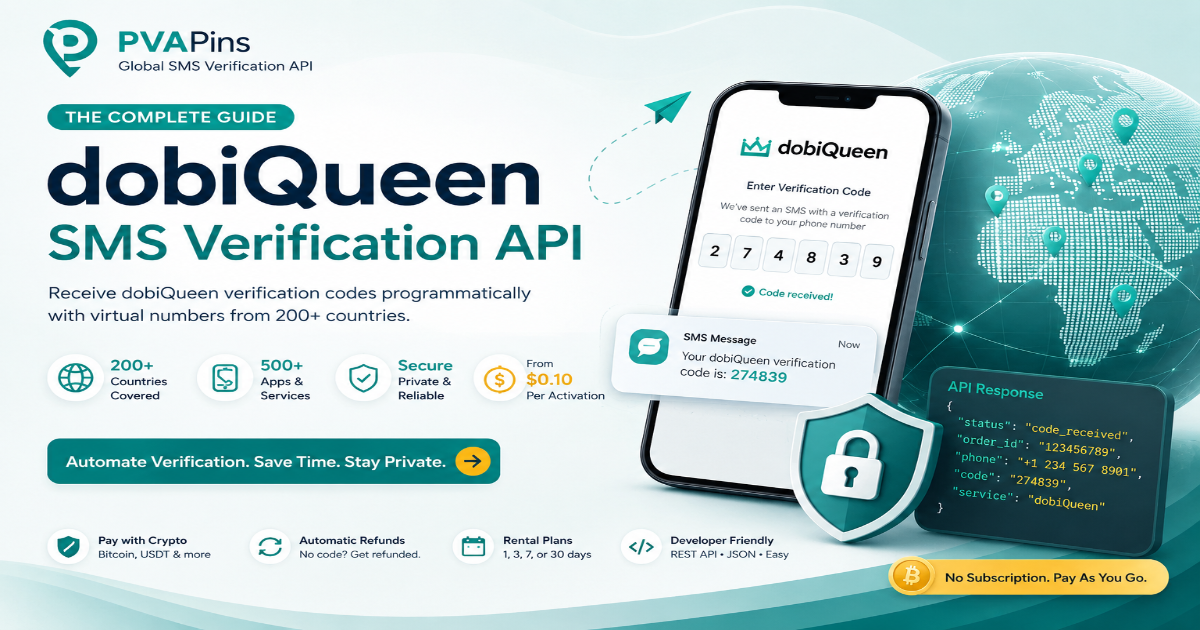
How it works
Choose the target country and service from the dashboard. Find dobiQueen in the service list, select your region. Availability refreshes live, so you know what's actually there before you commit.
Pay with Bitcoin, USDT, or another supported gateway. Rates start around $0.10 per activation. No card details, no subscription lock-in you're done the moment the payment clears.
Copy the virtual number and paste it into dobiQueen's verification field. That number is exclusively yours for the activation window. No one else can touch it while you're using it.
Watch the dashboard for the incoming SMS. Codes usually appear within seconds. Carrier lag can occasionally stretch things to a few minutes, so don't panic at the 90-second mark. . No code? Automatic refund. No support ticket required. You can retry with a fresh number immediately.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
A Brazilian number should display as +55, not +1. Use real regional numbers to catch formatting bugs in your UI before real users do•
Confirm the number's country matches the app's expected format. A UK number won't route correctly if the app expects US formatting•
Ensure the full international format, + prefix included, is entered correctly in dobiQueen's verification field—
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about dobiQueen SMS verification.
Is using a dobiQueen SMS verification API legal?
Yes, in most jurisdictions, using virtual numbers for app verification is legal, provided you're not violating an app's terms of service or using them for fraud. You're responsible for ensuring your use case complies with local laws and each platform's rules. PVAPins is transparent about authorized use cases and recommends reviewing terms before ordering.
Why didn't I receive my dobiQueen verification code?
The usual suspects: the app blocked virtual numbers, the number was previously used for that service, or a regional SMS routing hiccup. Double-check the country code and wait up to 5 minutes. If no code lands, PVAPins automatically refunds that activation.
What's the difference between a one-time number and a rental number?
A one-time number handles a single OTP, then expires. A rental number stays active for 1, 3, 7, or 30 days so that you can receive multiple OTPs for recurring logins or extended app testing. Rentals cost a bit more daily but are far more economical for repeated use.
What should I NOT use a temporary number for?
Never use virtual numbers for identity verification on financial platforms (banks, payment processors), healthcare portals, or government services. Those require real identity proof, and using a virtual number could constitute fraud. Also avoid creating fake, abusive, or spam accounts.
How do I troubleshoot a dobiQueen verification code that never arrives?
First, verify the number was entered correctly, and the country matches the app's expectations. Wait up to 5 minutes; carrier delays happen. Check your PVAPins dashboard for SMS status (pending vs. received). If it stays pending, cancel and retry with a new number.
Can I automate dobiQueen SMS verification for app testing?
Absolutely, that's one of the main use cases. Use the PVAPins API to request numbers programmatically, trigger OTPs in your test suite, and poll for codes. The API supports REST calls with JSON responses, so it integrates cleanly with any programming language or CI/CD pipeline.
Is my personal number exposed when using a temporary number?
No. The virtual number is completely separate from your real SIM. The app you're verifying only sees the virtual number, keeping your personal number off marketing lists, data broker databases, and potential breach datasets. Crypto payments add another privacy layer versus credit card billing.
Read more: Full dobiQueen SMS guide
Open the full guide
So you're deep in a build, and you've hit the wall every developer knows too well. You need to test real SMS flows; maybe you're automating signups across regions, or your QA suite needs to validate OTP delivery end to end. And then it hits you: you need a dobiQueen verification code, but you're not about to burn your personal number or sit around refreshing a physical phone every time a code drops.
Enter the dobiQueen SMS verification API. Give it a virtual number, let it receive the code programmatically, and your pipeline... runs no babysitting required.
Quick Answer
The short version, before we go deep:
PVAPins offers a dobiQueen SMS verification API that lets you request virtual numbers and pull OTPs programmatically through REST endpoints.
Coverage reaches 200+ countries, with live availability shown per service. Pay-per-use starts around $0.10 per activation, with no subscription to worry about.
Need repeat OTPs on the same number? Rental plans (1, 3, 7, or 30 days) handle ongoing logins and app testing without re-ordering.
Payments run through crypto (Bitcoin, USDT), and if a code never shows up, you get refunded automatically.
The API pattern is dead simple: request a number, trigger the SMS, poll for the code. Works in any language you throw at it.
Why Use a dobiQueen OTP API Instead of Your Real SIM
Here's the thing: your personal phone number is not a testing tool. Every time you punch it into a random signup form, you're handing it to data brokers, marketing lists, and, worst case, someone running a SIM-swap attack. A dobiQueen SMS verification API hands you a disposable virtual number instead, so your real SIM stays out of the crossfire. The whole flow becomes code: request a number, wait for the OTP, and pass it to your test suite: no physical device, no copy-paste marathons.
Why this matters in practice:
Keep your primary number off spam lists and out of SIM-swap crosshairs. The FCC has flagged SIM-swapping as a growing fraud vector, and your personal number is ground zero. Stop feeding it to every app that asks.
Make signup testing a code problem, not a human problem. Your CI pipeline shouldn't grind to a halt because someone forgot to check a phone. An OTP API removes that dependency entirely.
Grab numbers from 200+ countries and test geo-specific behavior properly. Your app might act differently in Germany versus Brazil. You need real numbers from both, not an approximation.
Stop mixing test accounts with your actual WhatsApp or Telegram identity. Keep the noise out of your real messaging apps.
Pay only for what you use. Zero tests this month means zero cost. No subscription, no "developer tier" upsell, no minimums.
Honestly, an SMS verification platform like PVAPins exists precisely because manual verification doesn't scale. The point is to turn a tedious chore into a single API call.
How to Receive a dobiQueen Verification Code: Quick Start
Want the code in under a minute? Here's the raw sequence. Pick your country and service (dobiQueen or any of the 500+ supported apps), drop a small crypto payment, and the virtual number appears in your dashboard instantly. Trigger the OTP from dobiQueen, and the code lands in your PVAPins inbox in real time. No forwarding, no second device.
The exact steps:
Step 1: Choose the target country and service from the dashboard. Find dobiQueen in the service list and select your region. Availability refreshes live, so you know what's actually there before you commit.
Step 2: Pay with Bitcoin, USDT, or another supported gateway. Rates start around $0.10 per activation. No card details, no subscription lock-in; you're done as soon as the payment clears.
Step 3: Copy the virtual number and paste it into dobiQueen's verification field. That number is exclusively yours for the activation window. No one else can touch it while you're using it.
Step 4: Watch the dashboard for the incoming SMS. Codes usually appear within seconds. Carrier lag can occasionally stretch things to a few minutes, so don't panic at the 90-second mark.
Step 5: No code? Automatic refund. No support ticket required. You can retry immediately with a fresh number.
This manual flow is your baseline. Temp numbers work fine on their own, but the real magic starts when you automate everything, which is exactly what's next.
Tired of burning your real SIM? Try a free test number from PVAPins and see how quickly a dobiQueen code lands. No subscription, no card details, just a crypto top-up and a real test. Explore free numbers →
dobiQueen OTP API Integration: Step-by-Step Code Flow
The integration isn't complicated, and that's intentional. Request a number, trigger the app's SMS, poll for the code in three stages- all REST, all JSON. You authenticate with an API key from your PVAPins Android app dashboard, hit the order endpoint to reserve a number for dobiQueen, and once the OTP arrives, a second endpoint hands it to your system. Then you proceed with verification like nothing ever required a human.
Stage-by-stage breakdown:
Authentication: Drop your PVAPins API key in the request header. No OAuth dance, no token refresh logic, no ceremony. Just a key in the Authorization header and you're moving. Store it in environment variables; hardcoding it invites trouble.
Order endpoint: Specify country ID, service ID, and rental duration. One-time activations are the default. Need the same number for multiple OTPs? Multi-day rentals stretch up to 30 days.
Polling loop: Retry every 5 seconds until status flips to code_received. Make this a background task in your integration. Fire the request, let a timer handle the polling, keep your main thread free.
Timeouts: Cap polling at 10 minutes. Most codes show up in under 60 seconds. If you hit the 10-minute wall, cancel and retry with a fresh number; the refund path covers failed activations.
Error handling: React to service_unavailable by swapping countries or retrying with a different number. High-demand regions sometimes drain the number pool. The API tells you explicitly, so your code can adapt without guessing.
The Developer API integration guide walks through every endpoint with example requests and responses. Bookmark it before you start building; it'll save you round-trips.
Pro tip: Building a reusable client? Follow standard REST API practices for error handling and idempotency. The RESTful API resource guide at restfulapi.net covers the patterns that keep integrations from crumbling under edge cases.
dobiQueen OTP Polling API: How to Fetch Codes Programmatically
If you're running test suites, checking a dashboard manually isn't an option. The dobiQueen OTP polling API exists for exactly this: place an order, poll the status endpoint with the order ID, and grab the SMS text when it lands. CI/CD pipelines, bot testing, bulk account creation this is where automation stops being optional.
A solid polling implementation looks like this:
Endpoint example: GET /orders/{order_id} returns current status and the received code. The response carries a status field (pending, code_received, failed) and, on success, the full SMS text with your OTP inside.
Polling strategy: Exponential backoff, not a fixed hammer. Start at 2 seconds, double up to a 10-second ceiling. Keeps server load sane while staying snappy under normal conditions.
Webhook alternative: If your setup supports callbacks, use them. Push-based delivery eliminates polling latency. Check the PVAPins dashboard for webhook configuration options; if it's there, it's faster.
Multi-order support: Poll multiple order IDs concurrently. Stress-testing signup rate limits with 50 parallel activations? Your polling layer needs to juggle all of them independently, without one slow order blocking the rest.
Logging: Timestamp everything. When a verification silently dies at 3 AM, you want a trail showing when the code was requested, when it arrived (or didn't), and exactly what the API returned.
Implementation note: code received is your terminal success state. Failed and the 10-minute timeout are terminal failures. Everything else means "keep polling." Simple as that.
dobiQueen SMS Verification in Multiple Countries: Coverage Explained
Country coverage is a huge part of why teams use virtual numbers in the first place; you can receive SMS online from apps that restrict signups to specific regions. PVAPins provides numbers across 200+ countries, covering the US, UK, India, Germany, Brazil, and plenty more. Availability varies by service, so the dashboard shows real-time status before you spend a cent.
In practice, this means:
Global reach across North America, Europe, Asia, Latin America, and Africa. Testing for Indonesia? Grab an Indonesian number. Mexico? Nigeria? Japan? Same story. The pool is deep.
Geo-specific testing for country codes and formatting. A Brazilian number should display as +55, not +1. If your UI butchers international formats, you'll catch it with real regional numbers before real users do.
High-demand regions like the US and UK usually have abundant supply. Best starting points if you're new to this. Niche countries can be thinner, depending on the service.
Service filtering: the API tells you which countries are available per service. Not every app supports numbers from every region. Check availability before ordering; the API surfaces this upfront.
Zero commitment. Unused numbers cost nothing. If dobiQueen isn't available in a specific country right now, try a neighboring region or check back later.
Receiving SMS across 200+ countries makes international app testing feasible. You're not boxed into one region or one number pool.
dobiQueen Verification Number for Global Use: Pricing and Rental Options
One-off numbers handle single signups fine. But what about repeated logins or multi-day test campaigns? That's where rentals come in. PVAPins offers online rent number plans from 1 to 30 days, so you can keep receiving OTPs on the same number without re-ordering every session. Pricing stays transparent: rental fee plus per-SMS cost, no hidden line items.
How to think about the economics:
One-time vs. rental: match the plan to your actual use case. Single OTP? Go one-time and pay the minimum. Ongoing logins or extended testing? Rent the number and stop re-ordering.
Rental pricing: per-day rates drop as you extend the window. A 30-day plan usually costs less per day than a 1-day plan. Longer commitment, better daily rate: classic trade-off.
Repeat OTPs: rental numbers make recurring logins painless. If dobiQueen sends a fresh code every session, a rental keeps your flow uninterrupted.
Billing: crypto only (Bitcoin, USDT). No credit card trails, no chargeback fights, no billing data tied to your verification activity. It's privacy by design.
Refund policy: failed activations don't cost you. If a number never receives a code, the platform refunds your payment. Applies to one-time and rental plans alike.
Check the number rental plans and transparent pricing and rates pages for current figures. Prices shift with demand, but the structure stays consistent: pay for what you use, nothing more.
dobiQueen SMS API for App Testing: Real-World Use Cases
This isn't just about one-off signups. The dobiQueen SMS API for app testing is about building repeatable, automated verification flows that run without anyone watching. QA teams use it to test SMS delivery mechanisms, validate OTP retry logic, and simulate user signups across different country codes. Penetration testing and integration testing with real SMS delivery? Also covered.
Real scenarios where this saves measurable hours:
QA automation: wire the API into your test suite and verify OTP flows programmatically. End-to-end tests create accounts, trigger verification, and confirm the OTP arrives no human touches a phone.
Multi-account testing: spin up dozens of test accounts to stress-test rate limits. What happens when 50 users register from the same IP in two minutes? You'll find out without recruiting colleagues for their numbers.
Geo-simulation: use numbers from different countries to validate localization. Error messages, date formats, and phone input masks all vary by region. Test them with real regional numbers.
CI/CD integration: run verification tests on every build or deployment. If your signup flow breaks in staging, you want to know before it does in production. Automated SMS verification surfaces immediately.
Demo environments: realistic signup demos without burning personal numbers. Sales calls, investor pitches, onboarding walkthroughs none of them should depend on someone's real phone.
Security note: Building OTP handling into your own app? Review the OWASP Authentication Cheat Sheet for guidance on rate limiting, OTP expiry, and secure storage. It's directly relevant to verification workflows.
Common Reasons dobiQueen SMS Verification Fails
Most failures come down to a handful of predictable causes. The app might block virtual numbers, the number might've already been used for that service, or regional SMS routing decided to throw a tantrum. Sometimes it's simpler: wrong country code, missing + prefix, or impatience. Most of these are easy to spot, and PVAPins refunds activations when no code arrives, so you can retry with a fresh number without eating the cost. our troubleshooting checklist.
ordered by likelihood:
Service blocks: some apps restrict virtual/VoIP numbers. Check dashboard availability before paying. PVAPins shows this upfront, so you're not gambling. If dobiQueen has a policy against virtual numbers, no integration will force it through.
Number reuse: a number previously used for the same service may get flagged. Order a fresh one instead of retrying with the same number. The platform rotates its pool regularly to minimize this.
Country-code mismatch: confirm the number's country matches the app's expected format. A UK number won't route correctly if the app expects US formatting. Double-check the full international format, including the + prefix.
SMS delays: wait up to 5 minutes before declaring failure. Most codes arrive in under 60 seconds, but carrier routing can lag. Don't cancel a pending order prematurely.
Refund path: if no code arrives, the platform refunds automatically: no support ticket, no dispute process. The system detects the failure and handles it.
Hitting consistent failures with a specific service or country? Switch regions or try a different time. Demand fluctuates, and number availability moves with it.
Code never showed up? That's on us to fix. Retry with a fresh number or get an automatic refund. Better acceptance rates start with the right number pool. Browse services →
dobiQueen Number API for Verification: Security and Compliance Best Practices
Using a dobiQueen number API for verification doesn't mean you can skip reading the rules. You're still responsible for each app's terms of service and local regulations. Virtual numbers are legit tools for privacy, testing, and business verification; they're not for evading bans, running fraud, or spamming people. Keep it lawful, and lock down your API keys like your database credentials.
The non-negotiables:
Terms of service: review each app's policy on virtual numbers; some explicitly prohibit them. That's on you, not the number provider. If an app bans virtual numbers, using one there violates the terms no gray area.
Use cases: legitimate uses include app testing, user research, and privacy protection. Keeping your personal number off marketing lists is a valid privacy practice, not a loophole.
Prohibited activities: fake accounts for abuse, vote manipulation, harassment. If your use case involves deception or harm to other users, you're outside legitimate bounds. Full stop.
API security: store keys in environment variables, never in client-side code. Whoever gets your key can order numbers and rack up charges. Treat it like a database password. Rotate regularly, revoke on suspicion.
Logging and audits: keep records of number usage. Which number for which service, and when. If questions arise, logs are your defense.
For a deeper dive on privacy and data handling, the ICO's GDPR guide covers the regulatory framing for verification data in the UK and EU. The NIST Special Publication 800-63B is the authoritative reference for digital identity and OTP verification standards, useful if you're building production-grade auth flows.
The Developer API Advantage: Going Beyond Manual Verification
Once the basic integration works, the dobiQueen API opens up more interesting territory. Batch number ordering, automated retry logic, and hooks into Slack or Jira for alerts. The API is REST-based with clear JSON responses, so wrapping it in Python, Node.js, or whatever your stack uses is straightforward. Teams that need scale can turn manual SMS verification into a fully automated pipeline.
What unlocks at the next level:
Batch operations: order multiple numbers in one request for parallel test runs: one API call, ten numbers, ten concurrent verification flows. Throughput scales without complexity creeping in.
Retry logic: automatically re-order when a number fails to receive a code. Your polling loop detects the failure, cancels the order, places a new one with no human intervention. Failed activations refund automatically, so retries cost nothing extra.
Third-party integration: stream codes to webhooks, messaging apps, or your own monitoring dashboard. Verification completes, webhook fires, Slack gets a notification. Or your Grafana dashboard increments a counter. The API fits whatever you're running.
Documentation: clear endpoint references, error codes, example responses. Good docs mean less guessing, more building. The endpoint reference is genuinely your friend here.
No subscription: pay-per-use scales down to zero when you're not testing. No monthly minimum, no "developer tier" gate. Pay for what you use. Stop paying when you stop using it.
The point isn't that manual verification is impossible. It's that manual verification doesn't scale: one OTP is easy, a hundred is tedious, a thousand is a full-time job. The API makes all three equally trivial.
One-time numbers are just the beginning. For ongoing app testing and repeat OTPs, rent a number for 1, 3, 7, or 30 days and keep your verification pipeline running without interruptions. Choose your rental plan →
Key Takeaways
A dobiQueen SMS verification API replaces manual phone checks with programmatic number requests and OTP retrieval. Your test suite handles verification end-to-end.
The integration pattern is simple: request a number → trigger SMS → poll for the code. REST endpoints with JSON responses make it language-agnostic.
Coverage spans 200+ countries, with real-time availability shown per service. Test geo-specific features without juggling SIM cards.
Pricing is pay-per-use, starting around $0.10 per activation: no subscription, no hidden fees, automatic refunds when a code never arrives.
Rental plans (1–30 days) support repeat OTPs for recurring logins and extended testing. More cost-effective than re-ordering one-time numbers every session.
Compliance is your responsibility. Free online phone numbers are legitimate tools for testing and privacy, not for fraud, spam, or evading platform bans.
Compliance note: PVAPins is not affiliated with the app/website or platform. Please follow each app/website’s terms and local regulations.
Last updated:
Ready to Keep Your Number Private in dobiQueen?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Daniel Marsh
Daniel Marsh is a software developer and technical writer with 8 years of experience in API integrations, backend automation, and online identity verification systems. At PVAPins.com, Daniel focuses on the technical side of virtual phone numbers — covering topics like SMS verification APIs, bulk number management, programmatic account setup, and integrating virtual numbers into development workflows.
Daniel has worked as a backend developer for multiple SaaS startups, where he regularly built and maintained phone verification systems for user onboarding and 2FA. That first-hand development experience gives him a uniquely practical perspective: he writes for developers, DevOps engineers, and technical teams who need more than just a surface-level overview of how virtual numbers work.
His guides at PVAPins go beyond the basics — diving into rate limits, number recycling, country-specific verification quirks, and how to select the right virtual number service for production environments. Every piece he publishes is informed by real testing and code-level experience, not just documentation review.
Outside of writing, Daniel contributes to open-source privacy tools, follows developments in GSMA and telecom regulation, and enjoys helping other developers navigate the often-underdocumented world of SMS verification at scale. His core belief: if a verification workflow is painful to set up, it's probably not designed for real-world use — and it's his job to help developers find what actually works.