Digit SMS Verification for Developers: Fix Delivery Failures
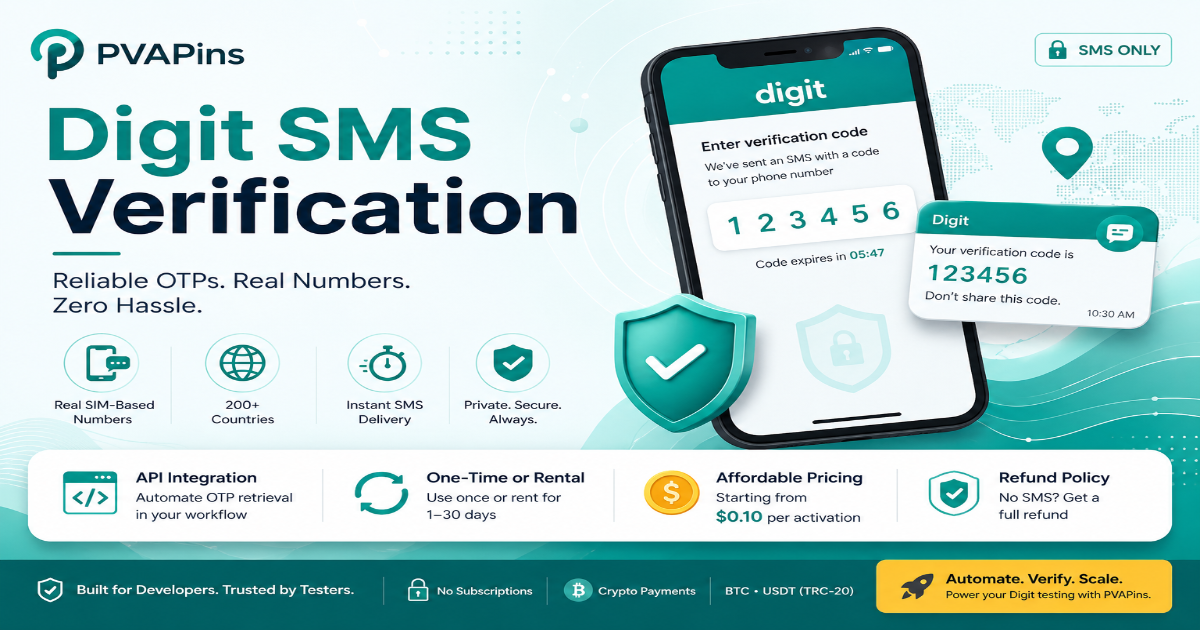
Quick answer: To verify Digit with a virtual number, choose a country on PvaPins from $0.26, enter that number as your Digit phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
How it works
Request a fresh number. POST to /v/create_service with the digits category. You get a clean, carrier-matched number reserved for your session.
Trigger the verification. In your Digit app instance device, emulator, or UI script initiate the code. The SMS routes to your reserved number.
Wait, then poll. Give it 10 seconds, then hit GET /v/message_status in a loop for up to 6 minutes. Most codes arrive in 30–60 seconds.
Handle resends. Still pending at 2 minutes? Script an automatic resend tap in the UI, then resume polling.
Log latency. Capture the internal_time when status flips to MESSAGE_RECEIVED. That baseline feeds CI/CD dashboards.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
Start around $0.10 per activation test small before scaling.
For extended regression testing, lock in a 7-day rental to handle re-authentication chains.
Buy a single cheap number first and manually walk the debug flow before scripting batch purchases.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about Digit SMS verification.
Is it legal to use temporary digit numbers?
Yes, provided you stay within the service's terms. PVAPins provides temporary verification for privacy protection and legitimate QA testing. Using it to bypass enforcement, commit fraud, or engage in any illicit activity crosses the line.
Why is my SMS not arriving at all?
"Unverifiable status" usually means a ported carrier or a flagged number range. Switch to a number on a different country code or carrier tier. A clean routing path resolves the majority of these cases immediately.
How is the temporary service different from a rental?
A standard temp number handles one OTP and rotates. If Digit collects two-step security and needs to re-verify your session later, a 7-day rental guarantees your number is still there when the second code fires.
What should I NOT use these numbers for?
Controlled inbox testing only. Don't attempt to circumvent KYC regulations for banking or credit card verification. If an app server-blocks a number, it's automatically closed and non-refundable.
What if my code is always "stuck pending"?
Integrate a status revision check before formatting your final output. Retry the verification with your local network protocol set to pure data mode; this sometimes forces the gateway to release the queued message.
Can I receive voice calls to verify Digit?
No. The platform is SMS-only. If Digit's sole verification method is a voice call, you cannot complete this flow.
Are there any refunds if the code doesn't come?
Yes. If no code is delivered to your temporary number, that specific activation cost is refunded.
Read more: Full Digit SMS guide
Open the full guide
Nothing kills momentum faster than staring at a phone that refuses to buzz. You've wired up the integration, written the polling logic, maybe even grabbed a coffee while waiting, and the Digit SMS verification code still hasn't landed. Meanwhile, your personal number is now tied to yet another test account you'll have to clean up later. There's a better way, and it doesn't involve burning real SIMs.
Quick Answer:
Digit's fraud filters are aggressive. They silently reject VoIP numbers and anything that smells like a public inbox service, so you need a quality virtual number that mimics real carrier behavior.
Grab a one-shot number for a single OTP, or rent one for days if you're running repeated login tests.
Automate everything through the API: request a number, trigger the code, poll for the SMS, extract it into your script.
When a code hangs in "pending," the fastest fix is almost always to discard and re-request a fresh number.
Why Digit SMS Verification Is a Pain Point for Developers
Digit's anti-fraud layer doesn't mess around. It cross-references phone numbers against risk databases, flags recycled VoIP ranges, and silently drops SMS requests that don't pass a background integrity check. As a developer, you get no error message, just an empty inbox and a creeping suspicion that your test harness is broken.
That suspicion is usually wrong. The problem is the number, not the code.
Here's what's actually happening under the hood:
Digit checks phone number hygiene against carrier records and known spam pools. Numbers from shared temporary services often get blocked before the SMS even leaves their gateway. You're troubleshooting a ghost.
The phrase "SMS Verification" in Digit's ecosystem can mean two very different things: a first-time login OTP, or a transaction re-verification triggered mid-session. The routing paths are not the same, and delivery behavior varies wildly between them.
Using your personal SIM for testing is a trap. Once your device ID and subscriber info get associated with a test loop, you risk rate limits and shadow bans that spill over into production usage.
Phone number rental services get treated better by carriers. A number held for 7 days tends to have a cleaner return path than one grabbed for 20 minutes, and your OTP delivery metrics will actually stabilize.
Your integration needs a proper "awaiting SMS" state with a polling interval that respects Digit's rate-limiting thresholds. Hammering their endpoint will only make things worse.
Getting Started: How to Receive a Digit SMS Verification on a Temporary Number
The mechanics are simple, but the timing matters. You need to complete your activation within the window before the number rotates away. Think of it like a hot potato: grab it, trigger the code quickly, and retrieve the SMS before the session closes.
One-and-done test? Head straight to the receive-sms page. Pick a number, punch it into Digit, and watch your dashboard. The message appears as plain text, ready to copy.
Need to re-trigger or run multiple login cycles over a few days? That's what the rent option is built for. Choose a 1-, 3-, or 7-day plan. Your number stays yours for the full window, so when Digit sends a follow-up code, you won't be scrambling for a new inbox.
Carrier selection matters more than you'd think. On the temp-number screen, you can pick the specific operator. If you're testing in a market like Korea, choosing between KT and SKT can make or break delivery on the first try.
Going programmatic? Use the API integration path. Have your public key ready, set up a test endpoint, then trigger the Digit code. Polling the message status endpoint is way faster than refreshing a dashboard manually.
Try the smallest activation first. One number, one code request, one successful retrieval. Get a feel for the latency before you build it into an automated suite.
Automate Digit OTP Testing: The Step-by-Step API Workflow
Automation here boils down to three steps: acquire a number, fire the OTP, and poll until you get a result. The whole flow replaces the physical phone interaction with a REST loop you can drop straight into a staging pipeline.
Here's the sequence that works reliably:
Request a fresh number. POST to /v/create_service with the digits category. You'll get back a clean, carrier-matched number reserved for your session.
Trigger the verification. In your Digit app instance, whether it's a real device, an emulator, or a UI automation script, initiate the code. The SMS routes to the number you just reserved.
Wait, then poll. Give it about 10 seconds to breathe. Then hit GET /v/message_status in a loop. Keep polling for up to 6 minutes. Most codes arrive within 30–60 seconds; anything longer suggests a routing hiccup.
Handle the inevitable resend. If you've been polling for 2 minutes and still see pending, script an automatic tap of the resend button in your app UI. Then jump right back into the polling loop.
Log the latency. Capture the exact internal_time value when the status flips to MESSAGE_RECEIVED. That number becomes your baseline for performance regressions and feeds directly into CI/CD dashboards.
Need the full parameter reference? The developer resources page has the API spec with every endpoint and response code documented.
How to Troubleshoot: Digit SMS Verification Not Sending, Stuck in Pending, or Code Not Delivered
"Pending" doesn't mean lost. It usually means the SMS hit a routing layer that hasn't finished doing its job, and sometimes that layer is a third-party gateway playing phone tag with carrier lookup tables.
If the code just never appears, you're probably dealing with Digit's silent anti-fraud rejection. The app accepted your request on the UI side, but the SMS pipeline quietly killed the message before it ever went out.
Here's how to break the deadlock:
Stuck pending? The Global Title Translation on the carrier side might still be resolving. It's annoying, but it's not a dead end. Switch to a one-time number on a different carrier. A fresh routing path often clears the queue instantly.
App-side blockage? Reset the session completely. Clear local storage, wipe the app cache, uninstall, reinstall. This flushes the device reference keys that Digit's client uses to pair with the SMS.
Network-level filtering? If your dashboard shows "blocked" instead of "delivered," change the host Message ID (MID) in your number selection. Different MIDs route through different gateway paths.
UI says SENT but nothing arrives? This one is sneaky. The WebView might be showing a cached confirmation while the actual POST request is never dispatched. Hard-kill the app and relaunch.
Still stuck after all that? Start a brand-new session with a free online phone number. It buys you a clean delivery route and, 90% of the time, a result within 60 seconds.
How to Fix Digit OTP Failure on Old SIMs and Dual SIM Configurations
Old SIMs carry baggage. Their IMSI registries might not fully support the modern SMS dispatch flow that Digit's 2FA relies on, and when the handshake fails silently, you get nothing.
Dual SIM phones add another layer of chaos. The wrong slot grabs the request first, the network switch lags, and the OTP falls into a gap between the two SIM states.
Here's what actually helps:
Digit's OTP flow tends to favor the last active data SIM. If your test slot isn't the primary data line, the SMS may route to the wrong place. Use a dedicated virtual number or eSIM profile to guarantee it's the active recipient.
Legacy SIM giving you grief? Force the device onto a stable network path. Sometimes updating carrier firmware helps; other times, routing your test device through a carrier-recognized VPN pushes the phone into a trusted "foreground state" and nudges the SMS through.
Dual SIM needs clear role separation. Set your personal number as the voice default. Keep the temporary digital number strictly as the SMS data line. That prevents the interrupt conflict that kills OTP delivery.
When old SIMs repeatedly fail, disable VoLTE temporarily and force the device to signal on a secondary band. It's a low-level workaround, but it's saved more than one QA session.
Handling Digit SMS Verification on Second Device and Dual SIM Setups
Digit fingerprints your device against the phone number. If the code goes to a secondary handset, the app instance on your main device might not pick it up unless everything is perfectly synced Bluetooth, cloud messaging, the works.
Using a second device is totally valid, but the timing and setup need to be deliberate.
Proper second-device flow: Log into the same account framework on both devices. Explicitly grant SMS permissions on the secondary one. The code almost always arrives faster on whichever device has the strongest carrier signal at that exact moment.
Dual SIM to primary app mapping: Designate the temporary number as the secondary data source on the physical second device. Keep it clean: no competing apps, no background sync fights.
Clock sync will bite you. If you're on a rooted device or emulator, SMS timestamps can drift. Run a forced NTP time sync on both Android and iOS before every test run. A 30-second clock skew can make it look like the code never arrived when it actually did.
IPv6 is the future, and it's already here. Make sure your polling or interception server handles IPv6 traffic gracefully. Some modern network paths will drop delivery reports entirely if the IP stack doesn't match.
Best Practices for Using Digit Verification App Codes in QA and CI/CD Pipelines
Treat the SMS receiver online as a detached external service because that's exactly what it is. Keep it separate from your app logic, mock early, and only graduate to live numbers once your mock flow passes consistently.
Mock first, live later. Build your aggregation JSON payload against a mock endpoint before touching a real number. This keeps real SMS intercept hooks out of your staging database and prevents accidental charge loops.
Environment variables are your friend. Set DIGIT_PHONE_NUMBER in your CI/CD pipeline config. At the start of every test run, pull a fresh number from the API or activate a current rental. It's one line in your YAML that saves hours of manual resetting.
Race condition guard. If your test uses dual numbers, build a watchdog timer. Script an alert to Slack, email, whatever if the message status doesn't flip to "received" within your expected window. Better to know immediately than to discover the failure in your regression report six hours later.
Webhook with backoff. Your SMS_Hook script should implement exponential backoff on retries. Hammering the status endpoint after a failure just guarantees rate-limiting. Start with a 5-second delay, then 10, then 30.
The Hard Truth: What Temp Numbers Can and Cannot Do for Digit Support
Let's be blunt: these are SMS-only reception points. No voice, no SIM-hardware pairing, no magic. If Digit's verification flow requires anything beyond a text message, this won't work. The legitimate path to receive SMS for testing means staying inside these guardrails.
What they won't do:
Voice call verification. There's no audio hardware on the back end. If Digit's only fallback is a phone call, you cannot complete the flow.
SIM-based hardware pairing. Any service that ties authentication to a permanent physical SIM ID will fail. These are virtual numbers, not hardware tokens.
Password reset flows that trigger marketing list verification. Those routes are profitable only for permanent SIMs and simply don't resolve on temporary lines.
WhatsApp or similar app-based verification where the platform explicitly bans virtual numbers. We supply the SMS reception; you are responsible for verifying the platform's terms allow it.
What they're great for:
OTP extraction in testing and QA environments.
One-time login verifications where SMS is the sole channel.
CI/CD pipeline integration where you need a fresh number per run.
Final Setup: Get Your Digit Test Number and Start Automating
Skip the friction. Head to the temp-number page, pick the Digit SMS service matching your operator requirements, and fund one activation. Pricing is straightforward: no monthly commitment; you only pay for messages that actually arrive. Crypto top-ups (Bitcoin, USDT) keep the flow fast and private.
International rates start around $0.10 per activation. Test small before scaling.
For extended regression testing, lock in a 7-day rental. That window handles re-authentication chains without breaking your workflow.
Developer tip: Buy a single cheap number first. Manually walk through the debug flow all the way to a zero state. Understand the full round-trip before you script a batch purchase. Those few cents will save you hours.
Then plug the PVAPins Android app into your dev environment using the integration panel. Numbers pull directly into your pipeline without leaving your console.
Need more? The full services list shows every available category and plan. Whether you're running one session or a hundred over 30 days, a dedicated rental queue brings predictability back to your testing loop.
Key Takeaways
Automate the full Digit OTP flow: API-purchase a number, trigger the code, poll with exponential backoff, extract the result.
The single most reliable fix for a stuck code is to discard the pending number and request a fresh one on a different carrier route.
In CI/CD, never use a real user's SIM. Pull a clean rented number via an environment variable for every regression run.
Temporary numbers handle text OTPs only. Voice calls and SIM-hardware verification are not supported, and no amount of configuration will change that.
Compliance note: PVAPins is not affiliated with the app/website or platform. Please follow each app/website’s terms and local regulations.
Last updated:
Ready to Keep Your Number Private in Digit?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Sarah Lin
Sarah Lin is a digital growth strategist and business writer with over 9 years of experience helping companies scale their online operations. At PVAPins.com, she covers the business side of virtual phone numbers — focusing on how agencies, marketers, e-commerce sellers, and multi-account operators can use virtual numbers to grow efficiently while staying compliant and private.
Sarah spent nearly a decade working in growth marketing and operations for digital agencies, managing campaigns across platforms like Facebook Ads, Google, TikTok, and LinkedIn — all of which require verified accounts to run at scale. That experience taught her exactly how important it is to have a reliable, repeatable system for account verification, and why relying on personal SIMs is a liability for any serious business operation.
Her writing at PVAPins is practical and business-minded: she breaks down how to set up virtual number workflows for account management, what to look for when choosing a provider for high-volume verification, and how to avoid common mistakes that get business accounts flagged or banned. She's particularly focused on use cases for affiliate marketers, social media managers, e-commerce businesses, and digital agencies managing multiple client accounts.
Sarah is based in Vancouver, Canada, and stays closely connected to the digital marketing community through industry events and online forums. When she's not writing, she consults with small businesses on growth strategy and keeps a close eye on how platform policy changes affect multi-account management practices. Her guiding principle: the best growth strategy is one that's sustainable — and that starts with building a secure, organized digital infrastructure.