Crunk SMS Verification API Integration
Quick answer: To verify crunk with a virtual number, choose a country on PvaPins from $0.13, enter that number as your crunk phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
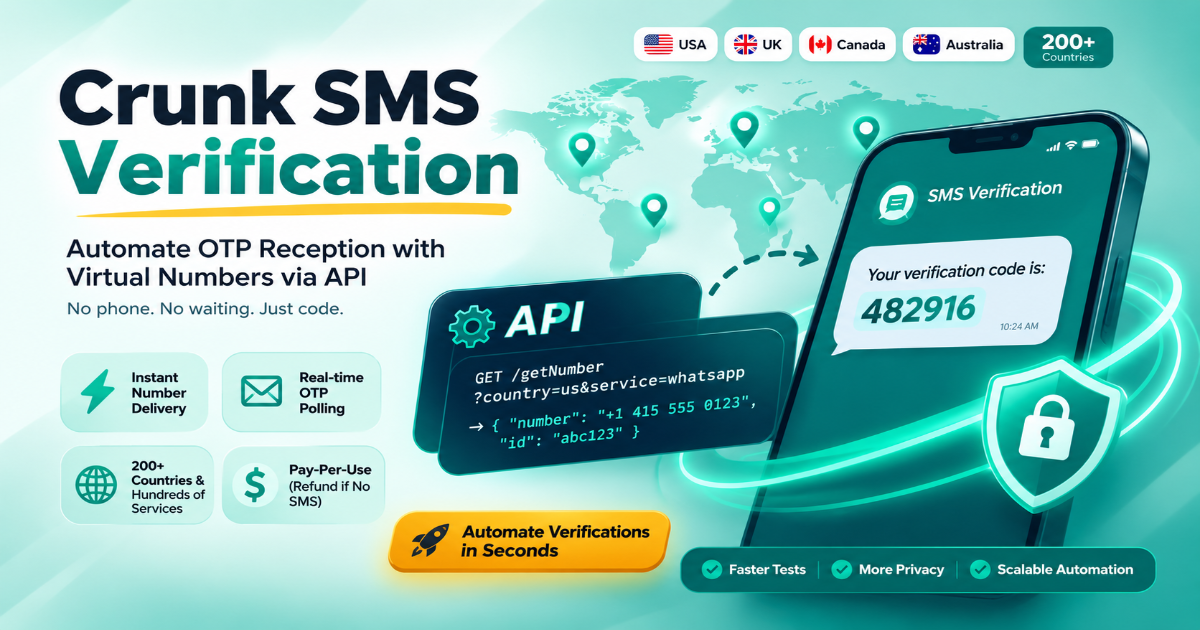
How it works
Sign up and generate your API key: From your provider dashboard, create an API key. Treat it like any other credential environment variables, never hardcoded, never committed.
Call the “get number” endpoint: Send a request with parameters for country and service. The response gives you a JSON payload with the number and an activation ID.
Submit the number to the target app: Your existing automation script or testing framework feeds the number into the service’s verification form.
Poll the “check SMS” endpoint: Every 2–5 seconds, hit the endpoint with the activation ID. When the status flips to received, the OTP is in the message text.
Parse the OTP and complete the flow: Pull the code from the response (usually a 4–6 digit string) and submit it to finish your verification.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
USA numbers are the most widely accepted by apps and have the highest success rates.
UK mobile numbers (07xxx) and geographic numbers (01xxx, 02xxx) are accepted by most European-focused services.
Australian mobile numbers (04xx) are most reliable for OTP reception in the APAC market.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about crunk SMS verification.
Is it legal to use a crunk SMS verification API for receiving OTPs?
Yes, as long as you follow each app’s terms of service and local regulations. Temporary numbers are designed for privacy and legitimate verification. PVAPins is not affiliated with any app or website. Please follow each app’s terms and local regulations. Using them for fraud, spam, or violating an app’s terms is illegal.
Why might an OTP code fail to arrive?
Codes can fail if the service doesn’t support virtual numbers, if the country’s carrier network has delays, or if the number is temporarily exhausted. Most providers, including PVAPins, offer a refund if no code arrives within the timeout window.
What’s the difference between a one-time activation and a rental number?
A one-time activation gives you a number for a single OTP session (usually 10–20 minutes). A rental number lasts 1, 3, 7, or 30 days and can receive multiple OTPs during that period, ideal for accounts that need periodic re-verification.
What should I NOT use temporary SMS numbers for?
Never use them for illegal activities, spamming, creating fake accounts for abuse, bypassing security, or violating any app’s terms of service. Doing so can get your API key revoked and may have legal consequences.
How do I troubleshoot a failed SMS verification?
First, check that your provider supports the service. Then verify that the country code matches the service’s requirements. If a code still doesn’t arrive within 60 seconds, cancel the activation and request a new number. Most providers offer a refund if no code is delivered.
Can I use the same temporary number for multiple verifications on the same service?
For one-time activations, the number is tied to a single session and expires after you receive the OTP, or the timeout passes. For rental numbers, you can receive multiple codes for the same or different services during the rental period.
Do temporary numbers work with two-factor authentication (2FA) resets?
Yes, they work with most 2FA flows that send an SMS code. However, some apps may flag virtual numbers for sensitive operations like password resets. If that happens, try a number from a different country or a rental number with a longer tenure.
Read more: Full crunk SMS guide
Open the full guide
If you’ve ever sat there refreshing a phone screen, waiting for a six-digit code to show up while your test suite times out, you already know why manual verification is a dead end. A crunk SMS verification API flips that entirely; it hands the whole loop over to your code. You request a number, the API serves one up, your app submits it to the target service, and the OTP lands in your polling endpoint instead of a physical device: no phone, no SIM swap, no waiting on someone else to read a code aloud.
This is strictly for the builders: developers wiring up automation flows, QA engineers testing onboarding at scale, and ops teams juggling multiple business accounts. It’s not a tool for dodging security, spamming platforms, or sidestepping terms of service. If that’s your angle, this isn’t the guide for you.
Quick Answer:
A crunk SMS verification API gives you programmatic access to temporary virtual numbers that catch OTPs.
You request a number, feed it to the target app, then poll the API for the incoming code, all in your logic.
It kills manual phone handling and keeps your real number out of databases.
Pricing runs pay-per-use, with numbers from the USA, UK, Canada, Australia, and 200+ other countries.
Refunds kick in if the code never shows up, and rental numbers cover repeat-verification accounts.
What Is a Crunk SMS Verification API and Why Would You Use It?
At its core, a crunk SMS verification API is a piece of infrastructure that lets your application pull a temporary phone number from a live pool, hand it to a service like WhatsApp or Telegram, and then retrieve the SMS OTP all without a human touching anything. It’s the middle layer between your code and a fleet of disposable numbers built for one job: catching verification codes.
Instead of parking a team member in front of a phone during a test run, your application runs the entire sequence. Request, submit, retrieve, verify. That loop takes seconds, not minutes, and it scales. For a dev shop running nightly builds or a business verifying hundreds of accounts, this isn’t a luxury; it’s the only sane way to operate.
Beyond speed, there’s a privacy angle that matters more than people admit. Every time you hand a real phone number to a random service, you’re gambling on whether it ends up in a marketing list, a data broker’s database, or a breach dump six months later. Temporary numbers act as a buffer. You get the verification you need without permanently linking your identity to the account.
Cuts out manual entry: No more typing codes from a phone screen during development or at scale.
Keeps your real number clean: Reduces exposure to spam, telemarketers, and data leaks.
Enables rapid iteration: Run dozens of test verifications in a single session without friction.
Works across the board: Not limited to a handful of popular apps; hundreds of services are supported.
No subscription trap: Pay-per-use means you’re not feeding a monthly bill for idle numbers.
Key Features to Look for in a Crunk SMS Verification API
The ones worth your time deliver numbers instantly, give you real-time OTP polling endpoints, and cover enough countries that you’re not stuck when a service demands a specific region. Beyond that, you want pricing that’s actually transparent, no mystery fees per activation, a refund policy that’s stated upfront, and the option to rent a number for longer than a single session. A clean RESTful interface with sensible error codes and documented rate limits saves you hours of head-scratching.
Not every API is built to the same standard. Some hand you a number fast but choke on delivery when it counts. Others have patchy coverage in the countries your app actually targets. Before you commit, look for signs that the provider invests in reliability and developer experience.
Here’s what to scan for:
Instant number delivery: The number should appear in the API response immediately after your call, not after a 30-second lag.
Real-time dashboard: A web UI where you can watch incoming messages without writing extra code, handy for debugging and spot checks. Browse our full list of supported services and countries.
Flexible rental periods: One-time activations (10–20 minutes) should sit alongside rental options (1, 3, 7, or 30 days) for accounts that need periodic re-verification.
Country-specific filtering: You should be able to request a USA, UK, Canada, or Australia number directly and see what’s available before you hit the endpoint.
Crypto payment gateways: Fast, private top-ups via Bitcoin, USDT, and similar, with no waiting on credit card settlement.
API keys with granular permissions: If you’ve got a team, scoped access means you can audit usage and cap costs per project.
The refund policy is a quiet signal of trustworthiness. If a provider tells you upfront that you’ll get your money back when no SMS arrives, they’re confident in their delivery. If they’re silent on it, you might be paying for dead air.
How to Integrate a Crunk SMS Verification API in Your App
Integration follows a pattern you’ve seen a hundred times: you call an endpoint to grab a number for a specific service and country, send that number to the target app, then poll another endpoint until the OTP shows up or the timeout fires. Most providers return a JSON payload with the number, an activation ID, and the incoming message text. Your job is to handle status codes like “waiting for SMS” and “code received” gracefully in your logic.
The flow is simple enough that you can have a working prototype running in under an hour. The trick is understanding the sequence and anticipating the edge cases: timeouts, empty number pools, and services that reject certain carriers.
Step-by-step integration:
Sign up and generate your API key: From your provider dashboard, create an API key. Treat it like any other credential: use environment variables, never hardcode it, and never commit it.
Call the “get number” endpoint: Send a request with parameters for country (e.g., us, uk, ca, au), service (e.g., whatsapp, telegram, google), and rental duration, if needed. The response gives you a JSON payload with the number and an activation ID.
Submit the number to the target app: Your existing automation script or testing framework feeds the number into the service’s verification form. This is where you plug in your headless browser or API client.
Poll the “check SMS” endpoint: Every 2–5 seconds, hit the endpoint with the activation ID. The response carries a status of waiting or SMS receiver online. When it flips to receive, the OTP is in the message text.
Parse the OTP and complete the flow: Pull the code from the response (usually a 4–6 digit string) and submit it to finish your verification.
This pattern is the foundation for nearly every integration you’ll write. Endpoint names and parameter formats shift between providers, but the logic stays the same.
Understanding Crunk SMS Verification API Documentation
Good API documentation spells out exactly which endpoints you can hit, what parameters each call expects, and how to read the response codes. Look for sections on authentication (API key in header), available countries and services, error handling (like “no numbers available” versus “invalid service ID”), and rate limits. It should also include sample requests in a few languages: cURL, Python, and JavaScript so that you can copy-paste and test immediately.
As a developer, you already know that documentation is the line between shipping in a day and debugging for a week. When you’re sizing up a crunk SMS verification API, spend five minutes in the docs before you write a single line of code. Explore our developer API documentation.
Here’s what solid documentation covers:
Base URL and authentication method: Typically a Bearer token or API-Key header. You should know the exact format and where it goes.
List of service IDs: A mapping of service names to codes (e.g., whatsapp for WhatsApp, telegram for Telegram, google for Google). Without this, you’re guessing and catching errors.
Status values explained: active (number reserved), waiting (waiting for SMS), received (code arrived), expired (timeout), canceled (you killed it early). Each is a state your code must handle.
Timeout durations: How long the number stays active before it expires, and what happens when no SMS arrives; most providers auto-refund.
Webhook setup: If you’d rather receive push notifications than poll, the docs should show you how to register a callback URL and what the payload looks like.
A well-maintained API doc includes a changelog too. If the provider updates endpoints or adds new services, you need to know before your integration breaks silently.
Programmatic OTP Handling: Polling vs. Webhooks
Polling means your application checks the API at fixed intervals, which is dead simple to implement but can waste requests if the code takes time to arrive. Webhooks flip the model: the API pushes the OTP to your server the moment it lands, cutting latency and API calls. For most integration scenarios, polling works fine; just set a sensible interval (2–3 seconds) and a max wait time (60–90 seconds) before you call it a failure.
Both approaches have their place, and your choice depends on your infrastructure and scale. According to general RESTful API design principles, polling is the most straightforward for clients without a persistent server, while webhooks are more efficient for high-throughput systems.
Polling:
Easier to debug and doesn’t demand a publicly accessible callback URL.
You control the frequency, but if you poll too fast, you’ll hit rate limits.
Works well for development, testing, and moderate-volume production use.
Best practice: poll every 2–3 seconds, max 20–30 attempts.
Webhooks:
More efficient for high-volume verification where every millisecond counts.
Requires a server endpoint that can receive POST requests from the provider.
You’ll need to handle signature verification to confirm the webhook is legitimate.
Once set up, you get the OTP in near real time without burning API calls.
Hybrid approach:
Poll for a short window (say, 10 seconds), then fall back to a webhook if available.
This gives you fast feedback during normal operation and a safety net for edge cases.
Regardless of your method, always handle duplicate codes gracefully. If the same OTP lands twice, your code should recognize it and skip the second attempt.
Which Countries Work Best with a Crunk SMS Verification API?
Coverage varies by provider, but the most reliable numbers for SMS verification tend to come from the USA, UK, Canada, and Australia thanks to high carrier availability and fast message routing. Developers targeting a global audience should also look for support across Europe, Southeast Asia, and the Middle East. A good API lets you filter by country code and shows real-time availability before you request a number. Check our country coverage for the USA, UK, Canada, and Australia.
Before you commit to a provider, verify that the countries you actually need are listed in their documentation. Some services are picky about which country codes they accept, and you don’t want to discover a gap mid-integration.
USA numbers are the most widely accepted by apps and have the highest success rates.
UK and Canada numbers work well for European and North American service verification.
Australian numbers are essential for localizing tests for the APAC market.
Some services restrict verification to numbers from the same country as the user’s IP.
Always check country coverage in the documentation before committing to a provider.
United States (USA)
USA virtual numbers are the gold standard for SMS verification because most global apps accept them without a second thought. When you request a crunk SMS verification number in the USA, you’ll typically receive a valid mobile or VoIP number that can catch OTPs from Google, WhatsApp, Telegram, and hundreds of other services. They’re ideal for testing North American user flows or creating business accounts that require a US-based phone.
The US mobile numbering system is mature, and apps rarely block American numbers outright. Even when a service is geo-restricted, a US number often passes because so many platforms have a global US user base.
High acceptance rate across social media, messaging, and productivity apps.
Area codes available from major cities (212, 310, 415, 312, etc.).
Suitable for both one-time activations and longer rental periods.
Some apps may reject numbers from certain carriers; check provider notes.
Refund eligibility if no SMS arrives within the timeout window.
United Kingdom (UK)
UK virtual numbers (+44) are essential for verifying services that geo-lock registration to British users or for localizing QA tests. They work reliably with major platforms like WhatsApp, Facebook, and banking apps that demand a UK country code. Like US numbers, they’re available for single-use activations or longer rental windows.
The UK has a well-regulated telecom market, and European platforms widely accept virtual numbers. If you’re testing a service that requires a UK presence for compliance or market-specific features, this is your go-to.
Accepted by most European-focused services and global platforms.
Mobile (07xxx) and geographic (01xxx, 02xxx) number formats available.
Good for testing compliance with UK-specific data protection norms.
Lower competition than US numbers in some provider pools.
Ensure your provider explicitly lists the UK in its country coverage.
Canada
Canadian numbers (+1, area codes like 416, 604, 514) are a solid alternative when US numbers are temporarily exhausted or when an app specifically requires a Canadian phone. They’re accepted by nearly all North American services and many international ones. Use them to verify accounts that require a Canadian presence or for broader North American coverage.
Because Canada shares the +1 country code with the US, international services often treat Canadian numbers the same as US numbers. If US numbers are in short supply, a Canadian number is a reliable fallback.
Works with Google, Telegram, WhatsApp, and most social platforms.
Canadian numbers are flagged for spam less often than some US VoIP ranges.
Available for both one-time and rental (1, 3, 7, 30-day) use cases.
Good for testing bilingual (English/French) service flows.
Verify that your API provider has real-time Canadian inventory.
Australia
Australian virtual numbers (+61) are crucial for developers targeting the APAC market or testing services that restrict registration by region. They’re widely accepted by platforms like Facebook, Instagram, and local Australian services. Using an Australian number during QA ensures your app’s verification flow works for users in that geography.
If your user base is in Australia or you’re expanding into the APAC region, testing with a local number is non-negotiable. Some Australian services even require a local number for account creation.
Strong acceptance rate for major social and messaging apps.
Mobile number ranges (04xx) are most reliable for OTP reception.
Useful for verifying Australian business accounts or localized marketing tests.
Time zone advantage: OTPs arrive during local business hours if needed.
Check provider for real-time Australian number availability before coding.
Crunk SMS Verification for Business Accounts and Multiple Users
Businesses use a crunk SMS verification API to create and manage multiple user profiles without exposing personal numbers. This is common for marketing teams running A/B tests, developers building multi-tenant platforms, or operations teams verifying internal accounts. The API lets you request numbers programmatically, associate them with specific projects or users, and track OTPs in a centralized dashboard.
When you’re running a business, you can’t have a single employee’s phone number tied to every account. What happens if that person leaves? Or if the phone gets compromised? A temporary number API decouples accounts from individuals, letting you manage verification at the team level.
Avoids the security risk of sharing one personal phone across the team.
API keys can be scoped per project for audit trails and cost allocation.
Rental numbers work well for accounts that need periodic re-verification. Rent a number for longer-term use
Team members can view incoming SMS without direct number access.
Pay only for activations used; no wasted spend on idle numbers.
For multi-tenant platforms, you can assign each client a dedicated API key with its own usage limits. This keeps billing separate and prevents one noisy neighbor from blowing through your entire quota.
Using a Crunk SMS Verification API for Testing and QA
During development, you need to confirm that your app’s SMS-based registration or two-factor authentication works end to end. A crunk SMS verification API gives you a disposable number, triggers the OTP, and captures the code automatically so you can automate that entire step in your test suite. This is far more reliable than using a personal phone or manual entry.
Manual testing is slow and error-prone. You might forget to clear a previous session, or the code might arrive when you’re not looking. Automating the verification step makes your test suite deterministic and repeatable.
Integrate the API into your CI/CD pipeline for regression testing.
Use different country numbers to test geo-specific verification logic.
Simulate timeout scenarios by requesting a number and not polling (check error handling).
Test multiple concurrent verifications to validate rate limiting and concurrency.
Combine with headless browser tools to automate the entire signup flow.
If you’re using a tool like Selenium or Playwright, the integration is seamless: your script requests a number, fills the form, and polls the API in the background. When the code arrives, the script enters it and continues. No human needed.
How to Avoid Common Integration Pitfalls
The most common issues stem from polling too aggressively (getting rate-limited), requesting numbers for unsupported services, or misinterpreting status codes. Always handle the “no numbers available” response gracefully: queue the request and retry later. Also watch for timeouts: if your app waits too long, the number may expire before the OTP arrives, so set a reasonable window (60–90 seconds) and trigger a retry with a new number.
Here’s a checklist to keep your integration smooth:
Poll every 2–3 seconds max: Faster than that and you’ll hit rate limits. Slower and you might miss the window.
Validate service IDs: Before requesting a number, check your provider’s list of supported services. An unsupported service will return an error.
Implement retry logic with exponential backoff: If the API returns a 429 or 503, wait and try again. A simple retry-after header check is a good start.
Log all API responses during development: Log every response, success or failure. When something breaks, you’ll have the full context.
Use the sandbox if available: If your provider offers a sandbox environment, test your integration there before hitting production. It’s free, and it saves you from burning real credits on mistakes.
If a code doesn’t arrive, don’t just retry endlessly. Most providers have a timeout window (typically 10–20 minutes). Cancel the activation, request a new number, and try again. If the problem persists, contact support if you run into integration issues. They can tell you if the service is down or if a particular country is experiencing carrier delays.
Security and Compliance When Using a Crunk SMS Verification API
Using temporary numbers is legal as long as you follow each app’s terms of service and local regulations. PVAPins is not affiliated with any app or website. Please follow each app’s terms and local regulations. Never use temporary numbers for fraud, spam, or bypassing security measures that violate both the provider’s terms and potentially the law. Store API keys securely, avoid logging OTPs in plain text, and use HTTPS for all API calls.
Security is a shared responsibility. The provider is responsible for maintaining the number pool and delivering SMS reliably, but you’re responsible for how you use the numbers and how you protect your API credentials.
Temporary numbers are for privacy, not abuse: They’re meant to keep your real number off marketing lists and to test your own apps. Creating fake accounts for spam or fraud is prohibited.
Comply with data protection laws: If you’re handling user data in the EU, you must comply with GDPR. That means being transparent about what data you collect and why. For more detail, refer to the European Commission’s data protection guidance.
Secure your API keys: API keys are secrets. Store them in environment variables, rotate them periodically, and never commit them to version control. The OWASP guide on secure API key storage provides a solid framework.
Avoid logging OTPs: If your app logs API integrate responses, make sure it strips out the SMS content. Logging one-time passcodes is a security risk.
Use HTTPS everywhere: Encrypt all API calls. If you’re sending an API key or receiving an OTP over HTTP, it’s exposed.
Remember that many apps explicitly prohibit using virtual numbers for account creation. Always read the target app’s terms before integrating. If you’re building a legitimate business use case, you’re usually fine, but ignorance isn’t a defense.
Real-Time SMS Reception: What Happens After You Send a Number Request
Once your application requests a number via the API, the provider reserves it from a live pool and returns it in the response. You then submit that number to the target service (e.g., WhatsApp). When the service sends the OTP, it arrives at the provider’s gateway and is made available through the polling endpoint or webhook. The entire process typically takes 5–30 seconds, though network delays can stretch it.
Understanding the lifecycle helps you write better error handling. The number isn’t pulled from thin air; it’s a real SIM or VoIP number that’s temporarily assigned to you.
The number is yours exclusively for the duration of the activation or rental.
Incoming messages appear in the dashboard and are returned by the API.
If no SMS arrives within the timeout, the activation is marked as expired and refunded.
Rental numbers continue to receive OTPs for the entire rental period (1–30 days).
You can cancel an activation early if the code arrives before timeout.
If you’re using a rental number, think of it like a short-term lease. You can use it for multiple verifications across different services, and it’ll stick around until the rental period ends. That’s ideal for accounts that need periodic re-verification, like a business profile that might trigger an SMS check every few days.
Getting Started with a Crunk SMS Verification API Today
The fastest way to start is to create an account at a provider like the PVAPins Android app, fund your wallet with crypto (Bitcoin or USDT), and generate an API key. Then make your first request: GET /getNumber?country=us&service=whatsapp. Within seconds, you’ll have a working number and a path to receive codes. The documentation is straightforward, and the pay-per-use model lets you test with minimal investment.
You don’t need to commit to a monthly plan or sign a contract. Start with a single activation, see if it works for your use case, and scale up from there.
No subscription required; pay only for what you use (as low as $0.10 per activation). Review our transparent pricing
Instant number delivery via API or dashboard for quick manual tests.
Supports 200+ countries and hundreds of services out of the box.
Rental options available for accounts that need repeat verification.
Developer API with clear rate limits and refund policy for failed deliveries.
Try It for Free: Want to test the integration before committing? Use a free sms verification or low-cost activation to see how the API works with your app. Visit PVAPins to get your first number →
Key Takeaways
A crunk SMS verification API automates OTP reception, cutting manual verification from minutes to seconds.
Integration follows a simple loop: get a number, submit it to the target app, poll for the code, and parse the OTP.
Polling is the easiest method for most developers; webhooks are better for high-volume production use.
USA, UK, Canada, and Australia numbers are the most reliable for SMS verification across services.
One-time activations are for single sessions; rental numbers (1–30 days) are for accounts needing repeat verification.
Always handle errors gracefully; timeouts, unsupported services, and rate limits are part of the normal flow.
Security is critical: store API keys securely, avoid logging OTPs, and never use temporary numbers for fraud or spam.
Pay-per-use pricing means you can start with a minimal investment and scale as needed.
Compliance note: PVAPins is not affiliated with the app/website or platform. Please follow each app/website’s terms and local regulations.
Last updated:
Ready to Keep Your Number Private in crunk?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Daniel Marsh
Daniel Marsh is a software developer and technical writer with 8 years of experience in API integrations, backend automation, and online identity verification systems. At PVAPins.com, Daniel focuses on the technical side of virtual phone numbers — covering topics like SMS verification APIs, bulk number management, programmatic account setup, and integrating virtual numbers into development workflows.
Daniel has worked as a backend developer for multiple SaaS startups, where he regularly built and maintained phone verification systems for user onboarding and 2FA. That first-hand development experience gives him a uniquely practical perspective: he writes for developers, DevOps engineers, and technical teams who need more than just a surface-level overview of how virtual numbers work.
His guides at PVAPins go beyond the basics — diving into rate limits, number recycling, country-specific verification quirks, and how to select the right virtual number service for production environments. Every piece he publishes is informed by real testing and code-level experience, not just documentation review.
Outside of writing, Daniel contributes to open-source privacy tools, follows developments in GSMA and telecom regulation, and enjoys helping other developers navigate the often-underdocumented world of SMS verification at scale. His core belief: if a verification workflow is painful to set up, it's probably not designed for real-world use — and it's his job to help developers find what actually works.