Instant CrazyKart SMS Verification Numbers for Online OTP
Quick answer: To verify CrazyKart with a virtual number, choose a country on PvaPins from $2.62, enter that number as your CrazyKart phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
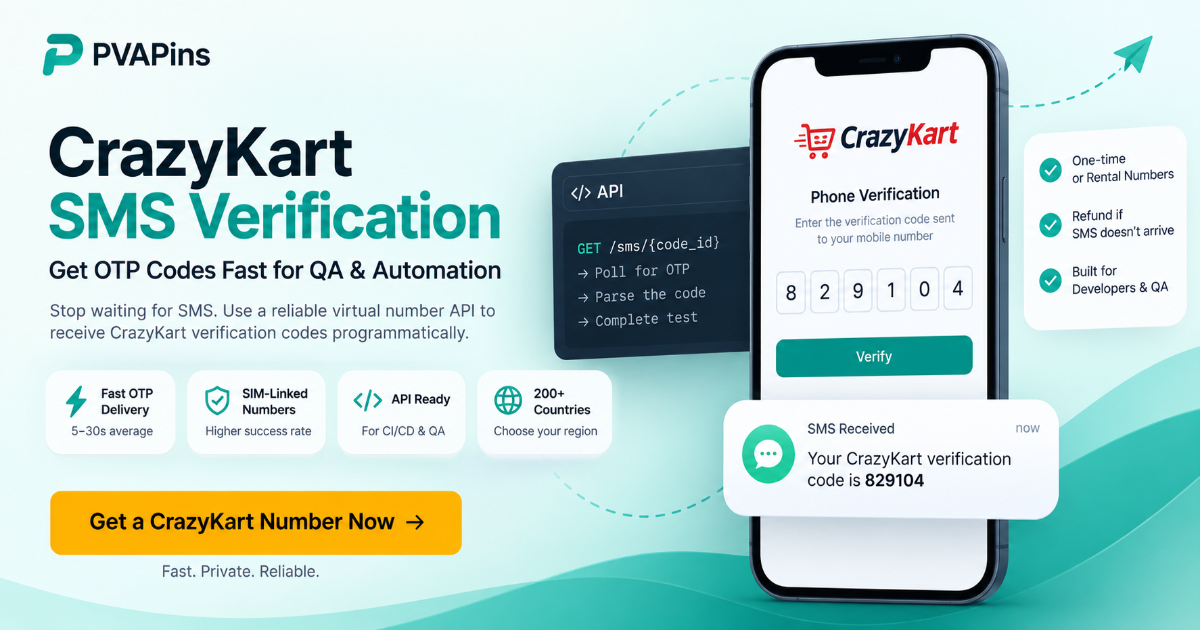
How it works
Authenticate: Grab a bearer token by calling the API's auth endpoint with your API key.
Request a Number: Call the number request endpoint with parameters service=crazykart and your target country code.
Trigger the OTP: Your test script kicks off the CrazyKart login flow using the phone number the API just gave you.
Poll for the Message: Start a loop that calls the SMS retrieval endpoint, passing the activation's unique id. Pause 3–5 seconds between each poll.
Parse the OTP: The API returns JSON. A quick regex pulls out the code (e.g., 829104). Inject and verify.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
Align the number's country with your test session's IP or locale headers to avoid silent region blocks by CrazyKart.
For international tests, use country codes like US, IN, or GB check carrier coverage for the target region before ordering.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about CrazyKart SMS verification.
Is it legal to use a temporary number for CrazyKart SMS verification?
Yes, it's legal for protecting your privacy, running QA tests on your own applications, or creating legitimate accounts. The line gets crossed when you use it for fraud, harassment, or to violate a platform's terms of service.
Why does my CrazyKart verification code keep failing to arrive?
Almost always because the number you're using comes from a public free pool that CrazyKart already blocked for spam prevention. A country mismatch between your number and your test session's apparent location is another common cause. Switching to a paid, SIM-linked number from the correct region usually solves it immediately.
Should I buy a one-time number or rent a number for CrazyKart testing?
A one-time number is cheapest and best for a single login test. If you're verifying multi-session behaviour, password resets, or "remember this device" flows spanning days, rent a number for 1–7 days so the same line stays alive.
What should I not use a temp virtual number for?
Never use one to bypass two-factor authentication on an account you don't own, create fake accounts to defraud a platform or users, or conduct any SMS pumping or denial-of-service attack. Those actions violate terms of service and carry real legal risk.
How fast will my CrazyKart OTP arrive via an API?
With a properly matched SIM-linked number, OTPs typically land within 5–30 seconds. If it consistently takes longer than 60 seconds, the number is probably flagged or the route is congested; try a different number or country code.
Can I automate the retrieval of the CrazyKart code in my CI pipeline?
Absolutely. That's the core use case. You integrate the API's polling endpoint into your Selenium or Playwright scripts with a 60-second retry loop and 5-second polling intervals. Mark the test "blocked" rather than "failed" if no code arrives so that you can distinguish infrastructure flakiness from actual regressions.
What happens if the code never arrives and I already paid?
On legitimate platforms like PVAPins, you're refunded or credited for the activation when no SMS is delivered. You pay for successful code receipts, not dead numbers that produce nothing.
Read more: Full CrazyKart SMS guide
Open the full guide
We've all stared at a test runner waiting for an SMS that refuses to show up. You trigger the CrazyKart login, your script starts its countdown, and then nothing. The pipeline goes red, and now you're digging through logs trying to figure out whether it's your automation code, some carrier black hole, or CrazyKart itself being difficult.
This guide cuts through that mess. It's for the developers and QA engineers who are done with flaky SMS-based tests and want something predictable. We'll walk through why those OTPs vanish, and how a dedicated SMS verification API replaces the whole manual waiting game with a clean, scriptable step your CI pipeline can actually rely on. Whether you're shielding your personal phone number from yet another test account or building a serious QA test bed, here's the blueprint.
Quick Answer:
CrazyKart OTPs usually fail because the platform flags recycled or VOIP numbers, not because your script is broken.
An SMS verification service hands you fresh SIM-linked numbers and lets you poll for codes programmatically the code lands, you grab it and move on.
For a single login test, grab a one-time activation (~$0.10). For multi-session QA work, rent a number for 1–7 days.
Wire the API straight into your CI/CD pipeline so manual code entry stops being the bottleneck.
Never use temporary numbers to commit fraud or violate CrazyKart's Terms of Service.
Why CrazyKart OTPs Fail or Time Out (And How Automation Fixes It)
The problem is rarely a simple "slow network." What really happens is that CrazyKart silently rejects numbers from pools it has already tagged as suspicious, or a carrier somewhere drops the SMS route, and nobody tells you. An automation API sidesteps both by serving you clean, carrier-grade numbers and letting your code actively hunt for the message instead of passively hoping it arrives.
Common causes for CrazyKart SMS not arriving
The biggest culprit is number blocklisting. Free phone numbers for sms pools get hammered by spammers, and eventually platforms like CrazyKart flag entire ranges; your verification text gets blocked at the gateway before you even know it was sent. Another sneaky one is region mismatch: you request a UK number, but your test session's browser locale or IP screams "India," and suddenly an anti-fraud rule kicks in and kills the message without warning. Then there's carrier-level throttling in certain countries, where a legitimate OTP gets delayed by 10–30 seconds, enough to blow right past CrazyKart's expiration window.
How a dedicated API bypasses carrier-level throttling
A real verification API doesn't sit around hoping for delivery. It maintains private pools of SIM-linked numbers that haven't been burned by public abuse. When you request a number for CrazyKart, you get one pre-validated for that service, not some random recycled digit string practically guaranteed to be flagged. And crucially, you're not stuck waiting for a push notification that may never fire. Your script actively polls the API's message endpoint every few seconds, snatching the OTP the instant it lands, well within that brutal 60-second TTL that would otherwise kill your test.
What You Actually Need from a CrazyKart SMS Verification API
You need three things that actually matter: numbers available right now across CrazyKart's supported regions, a polling mechanism with configurable timeouts that doesn't leave you guessing, and an honest cost model where you don't pay for SMS that never show up. Everything else is noise.
A practical API assigns a number in seconds, not minutes; this matters when your QA run is on a tight clock. Its endpoints should return the OTP as plain text inside straightforward JSON, not wrapped in some HTML blob or dependent on webhooks you haven't configured yet. The provider should also have a clear refund or credit system for undelivered messages; you didn't get a code, you shouldn't pay for one. You'll also want support for both single-use activations and longer rental periods, so one tool covers everything from a fast login smoke test to a multi-day password reset flow. And the whole thing should speak simple REST, with no heavy SDKs adding unnecessary dependency weight to your project.
Automating CrazyKart OTP Receipt for QA Test Suites
The play is simple: call the API, run a short polling loop, and inject whatever code comes back directly into your CrazyKart automation script—no human reading a phone screen, no typos, no delays.
Integrating the API into your CI/CD pipeline
The goal is for a missing SMS to become a logged event, not a pipeline failure. Inside your Selenium or Playwright script, you hit a GET /sms/{code_id} endpoint right after triggering the login flow. Wrap it in a try-catch that loops for a maximum of 60 seconds. Code arrives? Parse it and proceed. Doesn't it? Log the timeout as a "blocked" test result; this cleanly separates infrastructure noise (dead number) from actual application bugs. See the API integration guide for exact request formats and the structure you'll parse.
Polling vs. webhook strategies for fast code retrieval
For CrazyKart testing specifically, polling beats webhooks almost every time. Webhooks need a public-facing listener, which becomes a configuration headache in local dev environments and ephemeral CI containers. Polling is just a loop living inside the test runner you're already using. Hit the endpoint aggressively every 5 seconds for the first 45 seconds after triggering the OTP. It creates a tight race condition that snags the code far faster than any human manually reading a device. Store the successful OTP-to-number mapping in your test artifacts so you have a debug trail later.
Programmatic CrazyKart Code Retrieval: The Step-by-Step Flow
You request a number for the service "crazykart," poll the API for incoming messages, pull the numeric OTP out of the response body, and feed it back into your test harness. The whole cycle should finish within 90 seconds tops.
Here's what the technical flow looks like:
Authenticate: Grab a bearer token by calling the API's auth endpoint with your API key.
Request a Number: Call the number request endpoint with parameters service=crazykart and your target country code.
Trigger the OTP: Your test script kicks off the CrazyKart login flow using the phone number the API just gave you.
Poll for the Message: Start a loop that calls the SMS retrieval endpoint, passing the activation's unique ID. Pause 3–5 seconds between each poll.
Parse the OTP: The API returns JSON. Somewhere in it, you'll see something like "message": "Your CrazyKart verification code is 829104". A quick regex pulls out 829104.
Inject and Verify: Feed that code into the app's OTP field and complete your test step.
Buy a CrazyKart Number via API – One-Time vs. Rental for Testing
A one-time activation handles that single login test perfectly. But if your QA needs to verify password resets or multi-day session persistence, you rent a number for 1, 3, or 7 days. Rentals keep the same line alive so CrazyKart doesn't treat every login like a brand-new account.
Here's how to decide. A one-time activation, usually around $0.10, is ideal for a single smoke test. You log in once, receive an OTP online , and the number is done. But if you're testing a "remember this device" feature or a multi-factor recovery flow that fires multiple codes over hours or days, you need the number to stick around. A rental persists and can receive unlimited SMS during its lease. Use a duration parameter like duration=3 for a 3-day hold to match your exact test cycle. Ready to buy a dedicated number through the API? Start with the one-time model to prove the flow before locking a number into a rental.
Try it without risk: Grab a number from the public test pool to see how the polling works. No payment needed for your first call. → Start free testing
Developer API for CrazyKart SMS: Real-World Test Scenarios
Don't just test the happy path. Your automation should hammer the edge cases: expired codes, wrong country suffixes, and simultaneous registrations firing in parallel. Real QA means launching dozens of requests at once to see what breaks.
Testing multi-step CrazyKart logins (password + OTP)
Your script should handle a full two-stage auth sequence without dropping context. After a successful password entry, it waits for that first OTP. Then the same rental number should be able to pull a second OTP for a different phase, say, a password reset triggered immediately after login. This validates that the session state holds and the number's account association doesn't evaporate.
Simulating expired or invalid OTP states in QA.
This is where you stop testing what should happen and start verifying what happens when users mess up.
Late Arrival: Wait 120 seconds after requesting the OTP before injecting it. Your PVAPins Android app should show a clear "code expired" error, not some vague failure message.
Wrong Code Twice: Inject a bad code, then another bad one, then the correct one. Verify the app doesn't lock the account too aggressively and that the "Resend OTP" path still works.
Already-Registered Number: Try registering a new account with a rental number you used earlier. CrazyKart should return an "account exists" error rather than silently sending a pointless login code.
Troubleshooting CrazyKart Verification Code Arrival Issues
If your code never lands, check three things first: CrazyKart flagged the number as virtual, your polling interval overshot the SMS TTL, or you picked a number from a region CrazyKart handles poorly. Adjust the origin country or rental type before burning more test time.
CrazyKart SMS timeout solutions (adjust polling intervals)
OTP Time-To-Live windows are stupidly short, often 60 seconds. If your polling loop starts 5 seconds late and only checks every 15 seconds after that, you can easily miss the delivery before the code expires. A better rhythm: poll every 3 seconds for the first 40 seconds after triggering the OTP. This aggressive front-loaded interval catches most deliveries. If you're still seeing timeouts regularly, don't just keep extending the total wait; browse country-by-country coverage first to make sure you're ordering from a stable carrier that actually delivers to that region for this service.
Why your code didn't arrive (carrier blocklist, region block, misrouting)
The costliest QA mistake is using a free trial number for CrazyKart. These public pools are almost universally blocked by now. The fix is almost always switching to a paid, private activation. Misrouting is another silent killer: you get a US number but your script's IP or locale headers suggest India, and CrazyKart's fraud engine quietly routes the SMS through a different, slower path or blocks it entirely. Always align the number's country with your test user's apparent geography. In rare cases, CrazyKart might try delivering the code via voice call instead of SMS; if your API can't handle audio, that looks exactly like a dead number.
QA Verification with CrazyKart Numbers Building a Robust Test Bed
A durable test bed reuses the same rental numbers for a batch of steady-state tests, cycles fresh one-time numbers across ephemeral accounts, and records every OTP success or failure so you can spot pattern-based breakdowns. Treat your number pool like a database connection pool: watch utilization and rotate anything that starts failing.
Think of phone numbers as a managed resource. Reserve 3–5 stable rental numbers just for your critical daily login smoke tests. They become your pipeline constant, letting you track delivery performance over time. For ad-hoc feature work or a heavy regression run, burn through virgin one-time numbers instead. This stops CrazyKart from rate-limiting a single, heavily used line. As your test bed grows, build a lightweight internal dashboard that tracks each number's success rate, average OTP arrival time, and last test timestamp. When a number starts degrading, rent a replacement for extended testing cycles and retire the problematic one, using the same instinct as rotating a leaked API key.
CrazyKart App SMS Testing: Edge Cases You Should Automate
Stop validating only the perfect user journey. Automate the messy stuff: wrong codes punched in twice, SMS that shows up late, numbers that are already registered. These scenarios generate real support tickets.
Your suite isn't finished until it explicitly exercises failure. Write a script that submits a wrong code, then another wrong one, triggers "Resend OTP," and confirms the new code is actually different from the first. Another script should test severe delay: grab a code 180 seconds after requesting it and verify the app rejects it cleanly with "OTP Expired" instead of crashing or displaying something cryptic. Test the "account already exists" path by attempting registration with a known, pre-verified rental number. And test a deliberate region mismatch to see if CrazyKart blocks the verification silently. These negative paths reveal far more about your application's real stability than a thousand flawless logins.
Security & Compliance When Using Temp Numbers for CrazyKart
Temporary numbers are legal and legitimate for testing and privacy. They exist so you can automate QA without exposing your personal line and verify business workflows without burning real SIMs. They are not for fraud, abuse, or violating platform terms.
Your responsibility is straightforward. Rotate numbers regularly; using the same line for weeks of continuous testing gets you tagged as a testing operation and pollutes your own results. Treat the API token that provisions your number pool with the same care you'd give a production secret: environment variables only, never hardcoded. Store API response logs only as long as your debug session requires, then purge them along with any personal data, in line with GDPR or CCPA if they apply to your context. This tool exists for legitimate first-party testing and privacy protection, period.PVAPins is not affiliated with any app or website. Please follow each app's terms and local regulations.
For the full picture on our operating rules and privacy stance, read our compliance and privacy policy.
Key Takeaways:
To fix CrazyKart "SMS not received," ditch free number pools and use a paid, SIM-linked number matched to your test's locale.
Programmatic code retrieval via REST API integrate turns a 60-second gamble into a reliable, sub-10-second step in your test script.
A solid QA test bed mixes stable rental numbers for core flows with fresh one-time numbers for dynamic and exploratory testing.
Automate the ugly edge cases: wrong codes, OTP expiry, region mismatches, because that's where real users trip up.
Stay within legal and ethical boundaries: temp numbers are for privacy and testing, never for bypassing security or committing fraud.
Need a number that lasts? Rent for 1, 3, 7, or 30 days and keep the same CrazyKart-compatible line. Top up with crypto for private, instant checkout. → Rent your test number.
Compliance note: PVAPins is not affiliated with the app/website or platform. Please follow each app/website’s terms and local regulations.
Last updated:
Ready to Keep Your Number Private in CrazyKart?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Team PVAPins
The PVAPins Team is made up of writers, privacy researchers, and digital security professionals who have been working in the online verification and virtual number space since 2018. Collectively, our team has hands-on experience with hundreds of virtual number platforms, SMS verification workflows, and privacy tools — and we use that experience to produce guides that are genuinely useful, not just keyword-stuffed articles.
At PVAPins.com, we cover virtual phone numbers, burner numbers, and SMS verification for over 200 countries. Our content is built on real testing: before any tool, service, or method appears in one of our guides, a member of our team has tried it personally. We fact-check our own recommendations regularly, update outdated content, and remove anything that no longer works as described.
Our team includes writers with backgrounds in cybersecurity, digital marketing, SaaS product management, and IT administration. That mix of perspectives means our content serves a wide range of readers — from individuals protecting their personal privacy online, to developers building verification flows, to business owners managing high-volume verification.
We're committed to transparency: we clearly disclose how PVAPins works, what our virtual numbers can and can't do, and who our guides are designed for. Our goal is to be the most trusted, most accurate resource for anyone looking to understand and use virtual phone numbers safely and effectively — wherever they are in the world.