The Developer's Guide to a Catch SMS Verification
Quick answer: To verify Catch with a virtual number, choose a country on PvaPins from $0.12, enter that number as your Catch phone number, and any SMS sent to it appears in your PvaPins dashboard. Numbers are available in 200+ countries, each as a one-time activation.
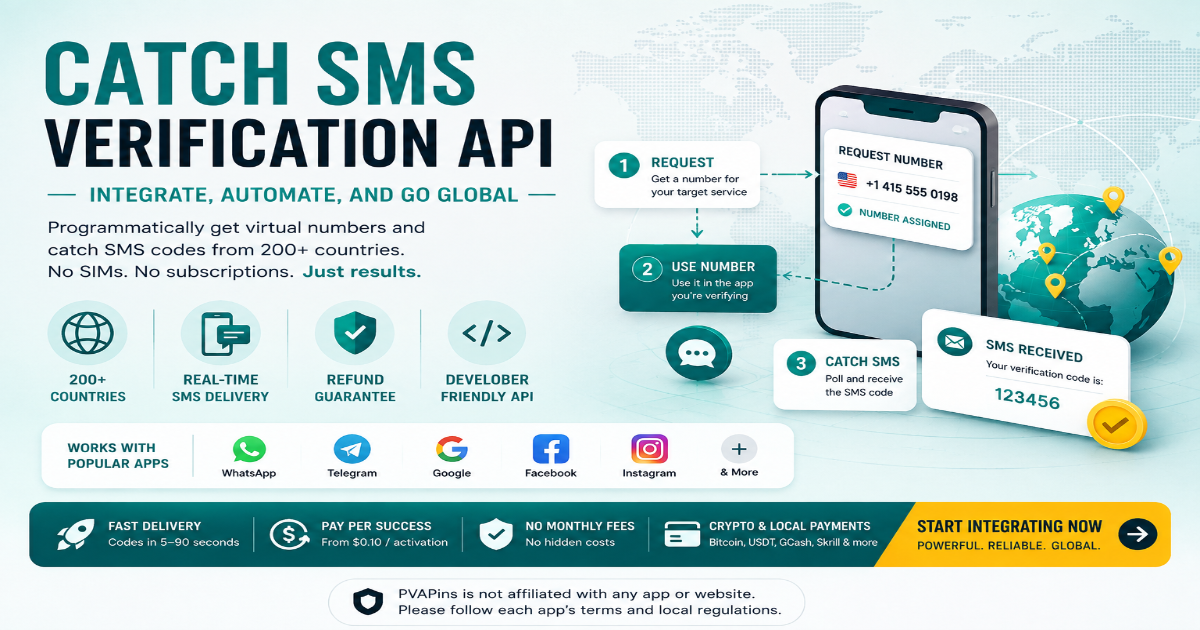
How it works
Request a Number: Your app calls an API endpoint (e.g., POST /getNumber) specifying the desired country and service (like "whatsapp").
Assign and Use: The provider assigns a temporary virtual number from its pool. You then use this number in the target application for verification.
Poll for Code: Your code continuously polls a second API endpoint (e.g., GET /getSms) for the incoming OTP until it arrives or a timeout occurs.
Capture OTP: Once received, the OTP is returned in the API response, ready for your application to use.
OTP not received? Do this
- Wait 60–120 seconds (don't spam resend)
- Retry once → then switch number/route
- Keep device/IP steady during the flow
- Prefer private routes for better pass-through
- Use Rental for re-logins and recovery
Wait 60–120 seconds, then resend once.
Confirm the country/region matches the number you entered.
Keep your device/IP steady during the verification flow.
Switch to a private route if public-style numbers get blocked.
Switch number/route after one clean retry (don't loop).
Free vs Activation vs Rental (what to choose)
Choose based on what you're doing:
Quick number-format tips (avoid instant rejections)
For international SMS verification, ensure the temporary number's country code matches the app's registration region (e.g., a +49 number for Germany).
Follow the standard E.164 format for phone numbers when using the API, which includes the country code and the full number without any leading zeros or special characters.
Inbox preview
| Time | Country | Message | Status |
|---|---|---|---|
| 2 min ago | USA | Your verification code is ****** | Delivered |
| 7 min ago | UK | Use code ****** to verify your account | Pending |
| 14 min ago | Canada | OTP: ****** (do not share) | Delivered |
FAQs
Quick answers people ask about Catch SMS verification.
Is using a catch SMS verification API legal?
Yes, as long as you use it for legitimate purposes like testing your own app, maintaining privacy on non-essential services, or conducting authorized research. Using it for fraud, harassment, or violating another service's terms is illegal. "PVAPins is not affiliated with any app or website. Please follow each app's terms and local regulations."
Why do some SMS codes fail to arrive?
Common reasons include the number being blocked by the app, the carrier rejecting SMS to virtual pools, or the activation timeout expiring before the code was sent. Cancel and request a fresh number from a different country pool; 9 times out of 10, it works.
What's the difference between a one-time number and a rental number for SMS verification?
A one-time number is activated for a single verification session and expires within minutes after a code arrives or times out. A rental number (e.g., a 1-, 3-, or 7-day plan) stays active for the rental period, allowing you to receive repeated OTPs or account recovery codes for the same service without needing a new number each time.
What should I NOT use temporary numbers for?
Never use them for bank accounts, healthcare portals, government services, or any system where identity verification is tied to a real person, and fraud has serious legal consequences. Also, do not use them to bypass security restrictions on apps you don't own.
What if the code arrives but is the wrong code or from a different service?
This is rare but can happen if the number is recycled too quickly. If you receive a stale code meant for someone else, cancel the activation immediately and request a fresh number. Reputable providers have cooling periods to prevent this.
Can I test the API without paying?
Some providers offer a free trial number or a low-credit demo endpoint. On pvapins.com, you purchase credits starting at a small minimum (e.g., $1-$5) and test with real activations. There's no monthly subscription.
Does the API work for phone verification in all countries?
Most major countries are covered (US, UK, Germany, India, Brazil, etc.), but remote regions or small island nations may have limited or zero coverage. Always check the provider's coverage list for your target country and app before building the integration.
Read more: Full Catch SMS guide
Open the full guide
Here's the thing about SMS verification: if you're still buying prepaid SIMs or juggling phones to grab a code, you're wasting time you could spend building. A Catch SMS verification API is how you fix that. It gives you programmatic access to temporary virtual numbers, lets you receive inbound SMS, including OTPs and poll for those codes without ever touching a physical SIM card.
Whether you're testing your app's authentication flows, keeping your personal number off random signup forms, or expanding into new markets, this approach scales hard. Just don't use it for anything shady; this is for legitimate testing, privacy, and automation, not fraud or ToS violations.
Quick Answer
A catch SMS verification API lets developers programmatically request virtual numbers and poll for inbound OTPs from apps like WhatsApp or Telegram.
Integration requires two core endpoints: one to get a number, another to retrieve the incoming code, no monthly fees, no SIMs.
Global coverage spans 200+ countries, with per-activation pricing starting at around $0.10 and a refund guarantee if no code arrives.
Best for testing app SMS flows, maintaining privacy on non-critical services, and verifying accounts at scale for legitimate business use.
What Is a Catch SMS Verification API? (Explained for Developers)
Think of a catch SMS verification API as your automated inbox for phone numbers. Instead of handing out your real number and manually checking for texts, your code requests a temporary virtual number, uses it wherever you need verification, and then polls an endpoint until the OTP arrives. It "catches" inbound messages from apps like WhatsApp, Telegram, or Google, and hands them back to your script.
No SIM card. No monthly contract. Just pure, programmable SMS receipt.
The "catch" part is key: this is active, real-time retrieval, not passive forwarding. Your application keeps polling an endpoint until a message appears. And unlike SMS gateways that send messages out, catch APIs are built for inbound receipt. Need a specific number for WhatsApp verification in Germany? You can request exactly that.
How "Catch" Differs From Standard SMS Forwarding
Standard SMS forwarding routes messages from one real number to another. Boring, limited, and tied to hardware.
A Catch SMS verification API does something smarter. It assigns a temporary, inbound-only virtual number that's provisioned specifically to receive an SMS from a target service. Your app then polls an endpoint to "catch" the message rather than having it auto-forwarded to your personal device. That distinction matters for privacy, for automation, and for keeping your real number out of databases you don't control.
Key Use Cases: Testing, Privacy, and Global Reach
Developers lean on catch SMS verification APIs for three big reasons:
Testing: Verify that your app's SMS delivery works across countries and carriers without requiring global SIM purchases.
Privacy: Sign up for services, tools, or trials without exposing your personal number to spam and marketing calls.
Global reach: Grab numbers from almost any country to simulate local user experiences or expand your service footprint.
It's practical, scalable, and way cheaper than maintaining a drawer full of prepaid SIMs.
How Catch SMS Verification Works: The Programmatic Data Flow
Here's the simple version: your app calls an API integrate endpoint to request a temporary number for a specific service (say, Google or Telegram). The provider assigns a number from its pool. You feed that number into the target app. When the app sends its OTP, the provider's infrastructure intercepts the SMS, and your code either polls for it via a second API call or catches it through a webhook. The whole cycle, from code request, usually takes seconds to a few minutes, depending on carrier speed.
Step 1: POST /getNumber with parameters for country and service (e.g., "whatsapp").
Step 2: GET /getSms polls repeatedly until the OTP arrives, usually within a 2-5 minute window.
Behind the scenes, providers maintain virtual SIM banks that are connected to real mobile networks via SMS aggregators or RAN-embedded systems. It's not magic; it's infrastructure.
Request → Poll → Capture: The Three-Step Loop
The core process is dead simple:
Request a virtual number through the API, specifying country and target app.
Use that number in the app you're verifying, then continuously poll the API's status endpoint for an incoming SMS.
Capture the OTP from the API response as soon as it lands.
This loop keeps things real-time. Your system acts on the code immediately, no manual copy-pasting required.
Why Polling Beats Webhook-Only Architectures for OTPs
Webhooks sound elegant: instant notifications, no polling overhead. But time-sensitive OTPs can fail you. A dropped connection, a server error, and that code is gone. You're left retrying manually.
Polling is more reliable. Your application checks repeatedly until the code is available, with built-in retry logic and timeouts. It handles temporary network hiccups gracefully. For critical SMS verification, polling wins every time.
Programmatically Get SMS Verification: Building the Integration
To programmatically get SMS verification, you wrap two core API calls: request a number, then poll for the code in your application logic. That's it. The simplest integration uses HTTP GET or POST requests with an API key; no SDK required.
You request a number for a specific app and country, use that number in your target service's registration form, then poll a second endpoint until the OTP arrives or a timeout expires.
SDK vs. Raw API: When to Use Each
Not sure whether to reach for an SDK or raw HTTP?
The raw API is fine for one-off scripts or when you want complete control over your HTTP requests.
SDK (if your provider offers one) simplifies complex workflows, retry logic, concurrent sessions, and error handling. It abstracts away boilerplate so you can focus on what matters.
For quick integrations, raw API gets the job done. For production systems with many moving parts, an SDK saves you headaches.
Test the API in Under 60 Seconds
Grab a $1 credit, hit the /getNumber endpoint, and see a real OTP land in your terminal. No commitment, no subscription.
Choosing the Best SMS Verification API Provider (What to Look For)
The best SMS verification API provider isn't the cheapest; it's the one that's transparent about coverage, clear about refunds when codes fail, and works on a pay-per-activation model rather than trapping you in a monthly subscription.
Start by checking if they support the exact app and country you need. Plenty of providers claim "global" but block high-demand apps like WhatsApp or Uber in certain regions. Then confirm their API includes a refund guarantee when an OTP isn't delivered within a reasonable window, not just a shrug and "blame the carrier."
Coverage Depth: Not Just Countries, But Specific Apps
Don't be impressed by "200+ countries" alone. Dig deeper. Does the provider offer numbers for the exact app you need, in your target country? A provider might cover WhatsApp in the US but not in Qatar. Look for a real-time coverage checker or a detailed list that shows what's actually available.
Pricing Models: Pay-Per-Activation vs. Subscriptions
Pay-per-activation is the way to go, like PVAPins' pricing (starting around $0.10 per code). You only pay for successful verifications. Subscriptions? Avoid them unless you're verifying hundreds of free online phone numbers daily. They lock you into costs you might not need.
Critical Feature: Refund Policy When a Code Fails
A reliable provider offers automatic refunds if a code doesn't arrive within a reasonable timeframe (say, 5 minutes). This is non-negotiable. If a provider won't back their service with a refund, they're not confident in their delivery rates: transparent refund policies = trustworthy provider.
SMS Verification API Integration: A Step-by-Step Developer Walkthrough
Let's walk through a real integration. You'll need three sequential actions: authenticate with your API key and check balance, request a number for a specific service and country, and poll for the incoming OTP until it arrives or times out.
Replace YOUR_API_KEY with your actual key from pvapins.com after signup.
Step 1: Authentication and Balance Check
Before anything else, authenticate and confirm you have a balance. A quick balance check prevents failed transactions later.
Step 2: Requesting a Number for a Target Service
Now request a temporary number for your specific app and country.
Step 3: Waiting and Retrieving the SMS Code
With the number obtained, start polling for the SMS.
If no code arrives after 5 minutes, cancel the activation with GET /cancelActivation?activationId=12345 to free the number and potentially trigger a refund.
For more detailed guidance, check our developer docs.
Developer API for SMS: Automating Verification at Scale
When you need to automate verification across hundreds of accounts or test suites, your SMS developer API must gracefully handle concurrency, retries, and error states. Treat each activation as an independent state machine: requested, waiting, received, or cancelled.
Batch number requests. Implement exponential backoff for polling. Log activation IDs in audit trails rather than reusing a single number across multiple apps.
Handling Timeouts, Retries, and Simultaneous Verifications
At scale, careful management is everything:
Set timeouts (e.g., 5 minutes) for each activation.
For getSms calls that return temporary errors, use retry logic with exponential backoff.
For simultaneous verifications, use unique activation IDs per request; never share a number across parallel verifications, or codes will collide.
Label your activation IDs with a UUID prefix for better tracking.
Best Practices for Rate-Limiting and Error Codes
Stick to the provider's rate limits to avoid temporary bans. Queue your polling calls to stay under the limit (e.g., 10 requests per second).
Know your error codes:
401 means bad API key.
402 means insufficient balance.
503 means the provider is overloaded (retry later).
A well-integrated API reduces manual verification time from 3 minutes per account to under 10 seconds, with full automation.
Automated SMS Verification: When and Why to Automate
Automated SMS verification is essential when you're testing SMS flows in CI/CD pipelines, bulk-validating app registrations for legitimate business use, or running large-scale automation that can't wait for someone to copy and paste code manually.
It saves hours of tedious manual work, but handles it carefully. Never automate verification for accounts tied to real identities or critical services without explicit permission. That's a quick way to violate terms of service.
Avoiding the "Death by Manual Entry" Problem
Manually entering OTPs for dozens or hundreds of accounts is a bottleneck that kills productivity. Automated SMS verification eliminates that "death by manual entry" problem entirely. It ensures consistency and speed in repetitive verification processes, perfect for setting up test environments in CI/CD pipelines or verifying user flows.
Automation vs. Human Oversight: A Balanced Approach
Automation is powerful, but doesn't cut humans out entirely. For critical systems or high-value accounts, a balanced approach works best: automatically retrieve OTPs, then have a human review or approve the final step. This hybrid method keeps efficiency without sacrificing security or compliance.
Catch SMS Verification Explained: The Hidden Technical Details
Curious what happens under the hood? Catch SMS verification relies on pools of virtual numbers provisioned from real Mobile Network Operators (MNOs) through wholesale SMS aggregators. When you request a number for US WhatsApp registration, the provider assigns an inbound-capable number from its MNO-connected pool.
The SMS from WhatsApp travels across the carrier network to a virtual SIM card or SMSC interface. The provider's software intercepts and parses it, then forwards the code to your API endpoint. All happens in seconds.
Virtual Number Pools and SMS-C Interception
Providers maintain massive pools of virtual numbers. Request one, and an available number is assigned from that pool. These numbers are linked to real carrier networks. When an SMS arrives, the provider's system intercepts the message directly from the SMS-C (Short Message Service Center) or through a virtual SIM gateway. Real-time capture, no delays.
Why Some Codes Fail (And How Providers Handle It)
SMS codes fail for a few reasons:
Carrier filtering (some MNOs block messages to virtual numbers)
Network latency
Target app restrictions
Reputable providers actively monitor their routes, switch to premium SMS gateways when needed, and implement cooling periods for number recycling. Even with best efforts, some codes still don't arrive due to factors outside the provider's control, such as carrier-level filtering.
International SMS Verification: Temporary Numbers for Worldwide Coverage
International SMS verification means matching the app's registration region to a number from that country's mobile network. To verify a WhatsApp account for a German user with a +49 number, you need a German virtual number.
Providers like the PVAPins Android app offer temporary numbers in 200+ countries, including the US, the UK, Germany, India, Brazil, and other niche markets. Coverage depth varies by app. Some providers excel in Asia but struggle in Africa. Always check country-specific availability before committing.
Country-Specific Success Rates: Why USA +44 and Russia +7 Behave Differently
Success rates vary significantly by country and app. Telegram verifies quickly on UK (+44) and US (+1) numbers but may reject Nigerian (+234) or Indonesian (+62) numbers due to frequent abuse or carrier restrictions. That's why providers specify app and country coverage; you need to know what works.
SMS Verification Numbers Worldwide: Matching the App's Registration Region
For successful international SMS verification, the temporary number must match the geographic region where you're registering the app account. A global provider lets you pick any country code and get a number instantly, but verify that the number is inbound-capable for the target app before purchasing. Wrong country code? The app might reject it.
Temporary Numbers for International Verification: Rental vs. One-Time
Need a number for repeat verifications over days? Look for rental plans (1, 3, 7, or 30 days) rather than one-shot activations. A one-time number is perfect for a single sign-up. For extended use, renting ensures consistency and spares you the need to keep acquiring new numbers.
Need a Number for a Week?
One-time activations are great for a single sign-up, but if you're verifying an account that sends multiple messages over the course of days, switch to an online rental number. We offer 1-, 3-, 7-, and 30-day plans.
Troubleshooting Your Catch SMS Verification API (Common Pitfalls)
Even with a solid API, SMS verification can fail. Most common issues: the number was already used by another activation, the target app blocked the number range, or the carrier delayed or lost the SMS. Sometimes it's app-level restrictions; Google occasionally rejects virtual number ranges for new account creation.
Here's how to diagnose and fix typical problems.
Code Never Arrives: Check Expiry, App Restrictions, or Country Blocklisting
Code not showing up? First, check whether the activation has expired (most providers set a 5-10-minute window). The target app might have restrictions on virtual numbers, or the country you chose might have blocked ranges.
Cancel the activation, request a fresh number from a different country pool, and try again. Nine times out of ten, a different number or country route works.
Number Already Used: How Providers Avoid Recycling That Fails
Getting a "number already used" message? The provider might have recycled it too quickly. Reputable providers implement cooldown periods (24+ hours) before reassigning numbers to prevent "ghost activations." If your provider's numbers are consistently marked as "already used," cancel and retry with a fresh number.
Carrier or App-Level SMS Blocking: What's Out of Your Control
Sometimes SMS blocking happens at the carrier or app level. Certain mobile operators, especially in India and Brazil, block SMS to virtual numbers. Some apps (Discord, Facebook) actively detect and block known virtual number prefixes.
In these cases, switch to a premium route offered by the provider or opt for a rental number, which often appears more legitimate.
Code Still Not Arriving?
If you've tried a new number and a different country without luck, you might need a premium route or a rental number. Our support team can help troubleshoot in minutes.
Compliance note: PVAPins is not affiliated with the app/website or platform. Please follow each app/website’s terms and local regulations.
Last updated:
Ready to Keep Your Number Private in Catch?
Get started with PVAPins today and receive SMS online without giving out your real number.
Try Free NumbersGet Private Number
Written by Alex Carter
Alex Carter is a digital privacy and online security writer with over 7 years of hands-on experience in cybersecurity, virtual number services, and identity protection. Based in Austin, Texas, Alex has spent the better part of a decade helping individuals and businesses navigate the often-confusing world of SMS verification, burner numbers, and account security — without sacrificing ease of use.
At PVAPins.com, Alex covers everything from step-by-step guides on verifying Telegram, WhatsApp, Gmail, and social media accounts using virtual numbers, to deep dives into why protecting your personal SIM matters more than ever. His articles are grounded in real testing: every tool, method, and tip Alex recommends is something he has personally tried and vetted.
Before joining PVAPins, Alex worked as a freelance cybersecurity consultant, auditing online account practices for small businesses and helping clients understand the risks of tying sensitive services to personal phone numbers. That experience shapes how he writes — clear, practical, and always with the real user in mind.
When he's not writing or testing verification workflows, Alex spends time contributing to privacy-focused forums, following developments in data protection law, and helping everyday users understand their digital rights. His core belief: online security shouldn't require a tech degree — and with the right tools, it doesn't.