
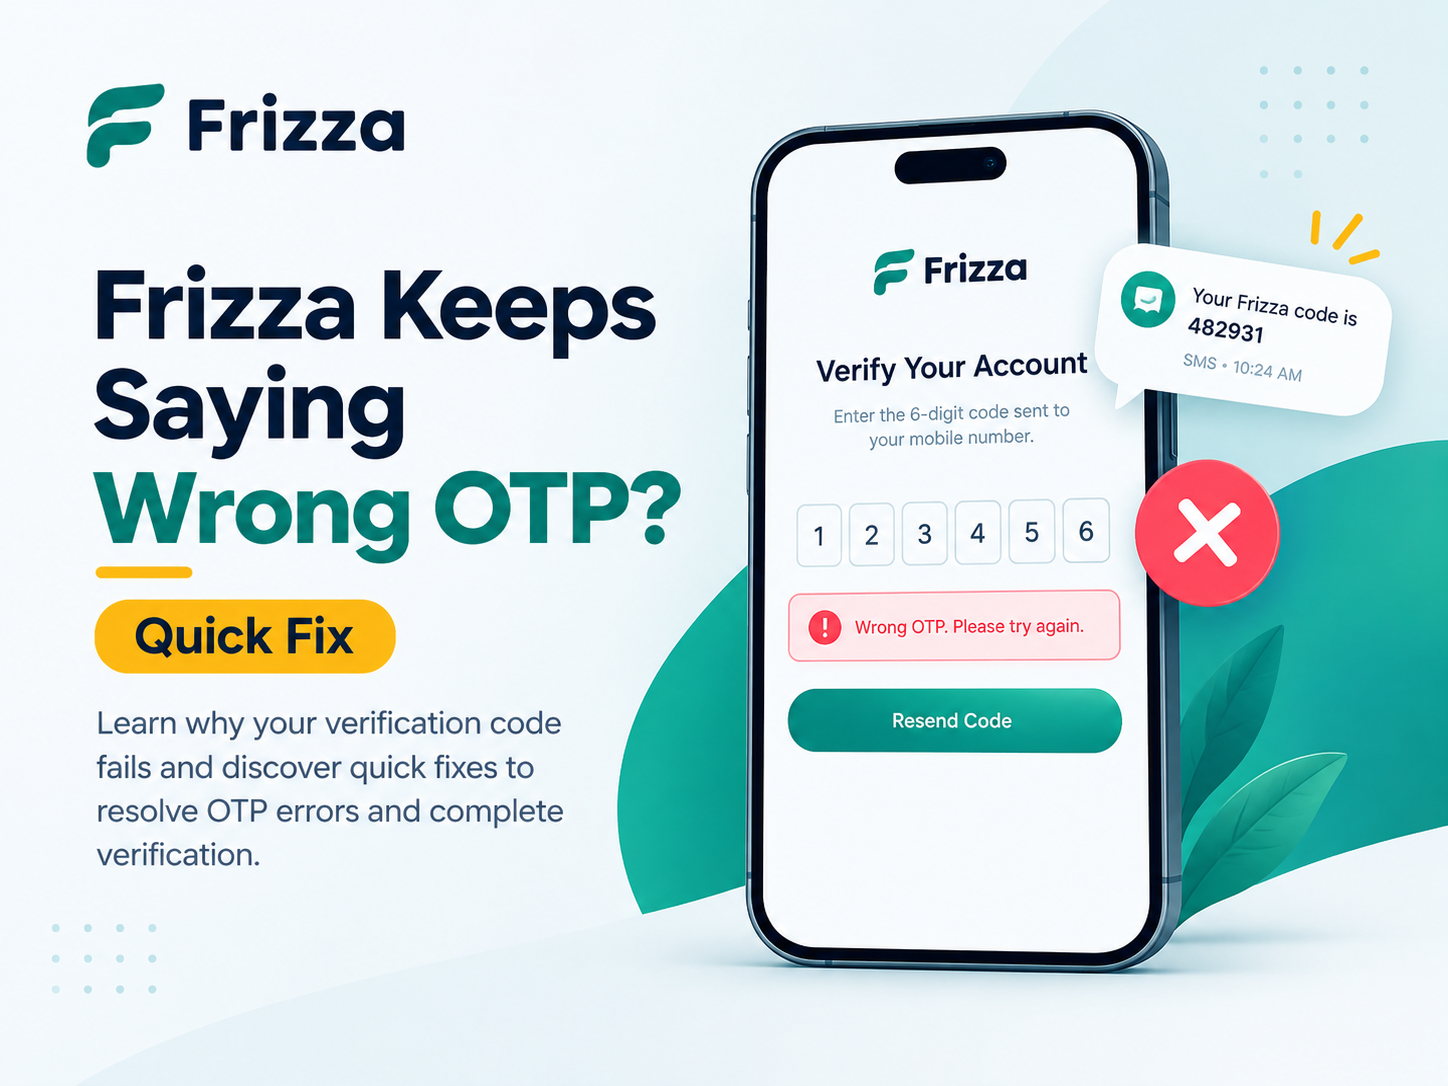

If you’re staring at a Wrong OTP error from Frizza when you know the code is correct, the problem isn’t your eyesight it’s your workflow. This guide is for developers, QA testers, and everyday users who are frustrated by invalid code errors. We’ll explain exactly why Frizza rejects codes, how to fix it manually in seconds, and how to automate the process entirely using an API. Hence, you never deal with this error again. If you’re using this for illegal activity, ban evasion, or spam, stop reading this guide for legitimate testing and privacy use only.
Quick Answer: Frizza Keeps Saying Wrong OTP
- Check the expiry: Most codes expire in 60–300 seconds; if you took too long, request a new one.
- Use the latest code: Requesting a new OTP instantly invalidates the previous one.
- Copy, don’t type: Manual entry causes typos; paste the code to avoid errors.
- Restart the session: Close Frizza completely and log back in to reset the session token.
- Check for truncation: Your carrier may have cut off part of the SMS, leaving you with a partial code.
Why Does Frizza Say Wrong OTP When the Code Is Correct?
When Frizza rejects a code you’re sure is right, the problem is rarely the code itself; it’s a mismatch between what Frizza expects and what you’re sending. The most common culprits are expired codes, accidentally merged SMS messages, or using a code from a previous verification attempt. Frizza’s system validates the most recent code sent; if you request a new one, the old one becomes invalid immediately.
Several factors contribute to this error, and understanding them is the first step to fixing it:
- Code expiration: Most OTPs expire in 60–300 seconds; Frizza enforces this strictly, and the code won’t work even seconds after expiry.
- Multiple requests: Requesting a new code invalidates the previous one immediately even if the old one looks like it should work.
- Partial code entry: Some carriers split OTP messages across two texts; you might be entering only half the code.
- Leading zeros stripped: If you copy-paste from a source that strips formatting (like some email clients or dashboards), a code like 00421 becomes 421.
- VPN or IP mismatch: Frizza may have flagged your login session as suspicious, causing the OTP to be rejected regardless of correctness.
The key takeaway: Frizza isn’t broken. The system is working exactly as designed to protect against unauthorized access. Your job is to align your input with its strict validation rules.
Quick Fixes to Try First Before You Contact Support
Before you dive into complex troubleshooting, run through these five high-probability fixes; they resolve the majority of wrong OTP complaints in under two minutes. The single most effective fix is to request a fresh code and enter it immediately, rather than lingering on the input screen. If that doesn’t work, force-close and restart Frizza’s app or browser tab, since stale sessions often cause false rejections.
Here’s your priority checklist for immediate resolution:
- Request a new code: Always generate a fresh OTP before entering, never reuse an old one.
- Restart the session: Close Frizza completely, reopen, and re-enter your phone number to trigger a new session token.
- Check your SMS inbox for duplicates: Sometimes carriers send two codes; use the second, not the first.
- Clear browser cache/cookies: For web users, cached authentication states can interfere with code validation.
- Try a different network: Switch from Wi-Fi to mobile data network-level SMS filtering varies by carrier.
Most users solve their issue at this stage. If you’re still stuck, the problem is likely timing or a deeper session issue, which we cover next.
Testing a new app or service and need a clean number fast? Get a temporary number in seconds with PVAPins pay only for the SMS you receive, no subscription.
The 30-Second Rule: Why Timing Breaks Your Frizza Verification
Frizza, like most verification systems, issues OTPs with a strict time-to-live (TTL) and if you don’t enter the code within that window, it’ll be marked as wrong even if you typed it perfectly. The practical implication? Open the Frizza input screen before you request the code, not after. Once the SMS arrives, enter it immediately; every second spent tab-switching reduces your chance of success.
Timing is the most common hidden killer of OTPs. Here’s what you need to know:
- TTL ranges from 60 to 300 seconds depending on the service Frizza is verifying; assume the shortest window to be safe.
- Copy the code before the SMS notification disappears. Don’t wait for the app to open automatically.
- If you’re switching between apps, keep the SMS thread visible and the Frizza input field pre-focused.
- Avoid retyping if the code fails once; request a fresh one rather than trying again with the same code.
- Set a timer on your phone for OTP-sensitive verifications to avoid losing track.
This is based on standards like RFC 6238, which governs time-based one-time passwords. The clock starts ticking the moment the SMS is generated, not when you read it.
How to Copy and Paste OTPs Correctly Without Typing Errors
The most underrated cause of wrong OTP errors is manual entry mistyping an O for a zero or transposing digits is common, especially with six-digit codes. Copy-paste eliminates this, but make sure you copy the entire code and not invisible characters like spaces or line breaks. When pasting, strip formatting to avoid submitting hidden characters that Frizza reads as part of the code.
To ensure your paste is clean, follow these steps:
- Use paste as plain text or paste into a text editor first to strip trailing spaces and newlines.
- Highlighting the full code partial highlighting often leaves out the first or last digit.
- Triple-check codes with letters (some OTPs use alphanumeric strings) O and 0 look alike.
- On mobile, use the SMS auto-suggest bar if it appears, but verify it inserted the whole code, not just a fragment.
- Never manually type more than once if the first attempt fails, copy-paste from the source instead of retyping.
If you’re using a temporary number to receive SMS, the copy-paste process is the same as with a physical SIM. The dashboard usually displays the code in a clean, copyable format, which reduces the risk of invisible characters.
Why Auto-Fill Apps Fail with Frizza and How to Fix It
Auto-fill apps and password managers often fail to correctly populate Frizza’s OTP input field because the field dynamically re-renders after the code arrives. When the auto-fill inserts the code too early, or into a hidden intermediary field, Frizza receives an empty or truncated value and flags it as incorrect. To fix this, turn off auto-fill on Frizza’s page and paste the code manually.
This is a known limitation with dynamic web forms. Here’s why it happens and how to work around it:
- Auto-fill timing issues: If the app inserts the code before Frizza’s field is ready, the value is lost.
- Dynamic fields: Frizza may use a one-time input mask that auto-advances; auto-fill tools don’t handle this well.
- Temporary fix: Turn off auto-fill for Frizza’s domain and manually paste from the SMS thread.
- Permanent fix: If you use an API or automation, bypass the UI entirely see the API sections below.
- Mobile-specific quirk: iOS and Android handle SMS auto-fill differently; iOS often pastes the entire message text, not just the code Frizza rejects.
If you rely on temporary number options for testing, the manual paste method is always safer than relying on OS-level auto-fill, which may not recognize the sender.
The Hidden Culprit: SMS Truncation and Carrier Filtering
Sometimes Frizza never receives the OTP, or receives a mangled version, because your mobile carrier truncates long SMS messages or filters messages from unknown senders. When an SMS is truncated, the code may be cut off entirely, so you’re entering a partial code that Frizza has never seen. This is especially common with virtual numbers and VoIP services, which often have aggressive filtering rules.
Carrier behavior is a variable you can’t control directly, but you can mitigate it:
- Message length limits: Standard SMS is 160 characters; longer messages get concatenated, and some carriers drop parts.
- Filtering by sender ID: Messages from unknown or international numbers are sometimes silently blocked or delayed.
- Virtual number sensitivity: VoIP and virtual numbers are filtered more aggressively than physical SIMs.
- Workaround: If you’re testing with a virtual number, use Frizza’s dashboard number directly rather than the SMS gateway.
- The fix: If truncation is constant, switch to a number from a different country or operator Frizza’s dashboard shows which numbers historically receive full messages.
Industry guidelines from groups like CTIA outline these filtering practices to combat spam. Understanding that this is a systemic issue helps you diagnose why a code might be wrong when it’s actually just incomplete.
What to Do When Frizza Marks a Code as Invalid But It’s Not
When you’re 100% certain the code is correct, and Frizza still rejects it, the issue is almost always a session-level problem: your authentication token has expired or been duplicated. The code itself is fine; the session that should validate it isn’t. Force a full logout (not just a browser refresh), wait 30 seconds, then log in again and request a new code.
Here’s the step-by-step recovery process:
- Session token conflict: If you have Frizza open in multiple tabs, the older session is invalidated.
- The fix: log out globally, close all tabs, log out from all devices if available, then retry.
- Check for SMS delays: The code Frizza just sent may not be the one you requested 10 minutes ago; request a fresh one.
- Verify the number: If you’re verifying a different number than the one you requested (e.g., country code mismatch), the code will always be rejected.
- If it still fails: Contact Frizza support with a screenshot showing the code and the error they can check backend logs.
This is the final manual step before you consider automation. If you’re doing this repeatedly, it’s time to move to the API approach.
Setting Up Frizza OTP API Integration for Developers
For developers, Frizza’s OTP API eliminates nearly every wrong code issue by bypassing the UI entirely. You request a number programmatically, receive the OTP as a structured API response, and use it directly in your test suite or automation. The API lets you specify the country and app, and polls for the incoming SMS, so there’s no manual copying, paste errors, or timing issues. You’re moving from human fallibility to deterministic code.
To get started, review the developer API documentation for the full endpoint reference. The integration logic works like this:
- API base endpoint: Requests return a unique request ID you use to poll for the OTP status.
- Number selection: Specify country and app; the API returns an available number or a not available error to retry later.
- Polling interval: Best practice is to poll every 2–3 seconds for up to 2 minutes; don’t poll faster or you risk being rate-limited.
- Response format: Parse the JSON response for the SMS text; extract the OTP with a regex.
- Error handling: If a number is occupied or the SMS doesn’t arrive, the API returns a clear error code handling these explicitly rather than retrying unthinkingly.
This setup removes the wrong OTP error entirely, as long as your regex is correct and the session is fresh.
How to Receive OTP Programmatically with Frizza’s API
Receiving an OTP programmatically with Frizza involves a three-step flow: request a number, trigger verification in the app you’re testing, and poll the API until the SMS arrives. Once you get the response, you extract the code and feed it straight into your test assertion. This approach is fully deterministic no human is typing, so the wrong OTP error becomes near-impossible unless the code itself is genuinely expired.
Follow this exact sequence for success:
- Step 1: Request a number via the API, specifying the country code and the app you’re testing.
- Step 2: Trigger the OTP on the target app, using the number Frizza returned.
- Step 3: Poll the API with your request ID until the status changes to received (usually within 5–30 seconds).
- Step 4: Extract the code from the SMS body using a regex that matches 4–8 digit patterns.
- Step 5: Submit the code to your test flow; if it fails, check that you received the SMS before you started polling.
If you’re building a test harness, this is the most reliable way to receive OTPs without flaky UI automation.
Automating Frizza Verification Codes: A Step-by-Step Workflow
A complete Frizza OTP automation flow for a CI/CD pipeline or test suite looks like this: start a session, request a number, trigger the app’s OTP, poll for the code, and assert it’s valid. The key is to design for failure if the SMS doesn’t arrive in the expected window, your script should terminate with a clear message rather than hanging indefinitely. This prevents flaky tests and gives you actionable logs when something goes wrong.
Here’s how to structure your automation for reliability:
- Use a staging number: Keep a dedicated number for automated tests to avoid conflicts with manual testers.
- Set a polling timeout: Hard-cap at 90 seconds; after that, fail the test and move on.
- Log the raw SMS: Store the full SMS body in test artifacts so you can debug any parser issues later.
- Handle parallel requests: If multiple tests run concurrently, use unique request IDs to avoid cross-polling.
- Retry logic: If the first number fails to receive SMS, request a new number and retry the whole flow, never reuse the same number for a second attempt.
This workflow is the gold standard for teams that need to verify accounts at scale without manual intervention.
Security Best Practices for Handling Frizza OTP Codes
OTPs are bearer credentials anyone who has the code can complete the verification, so you must handle them with the same care as passwords. For developers, that means never logging full OTPs in plain text, redacting them in test output, and ensuring the API response isn’t stored in logs. For manual users, it means never sharing the code or the number with third parties.
Adhere to these practices to keep your verification flows secure:
- Never log OTPs in plain text redact them to **** in test runs and CI logs.
- Use environment variables for API tokens rather than hardcoding them in source code.
- Restrict API token permissions to the minimum scope your integration needs.
- Rotate API keys regularly or after any suspected leak.
- Watch for phishing risks Frizza will never call you and ask for your code; enter it only in the verified app’s interface.
The OWASP Authentication Cheat Sheet provides excellent guidance on handling one-time passwords securely. Follow these standards to avoid turning a convenience feature into a liability.
When to Rent a Number vs. Use a One-Time Code
One-time numbers are ideal for single verifications, while rented numbers suit scenarios where you’ll receive repeated OTPs over days like testing multi-factor authentication flows or maintaining a profile on a service that periodically re-verifies you. Frizza offers 1-, 3-, 7-, and 30-day rentals for exactly this purpose. The rule of thumb: if you’re verifying once, use a one-time number; if you’ll verify more than twice in a week, rent.
Consider your usage pattern to make the cost-effective choice:
- One-time numbers: Best for quick signups, trial accounts, and one-off tests pay per SMS, no commitment.
- Rented numbers: Best for ongoing verification needs across multiple sessions or for quality assurance testing.
- Cost comparison: Renting is cheaper than buying multiple one-time numbers if you need frequent OTPs check PVAPins pricing for OTP verification for updated rates.
- Use case example: Testing an app with 2FA that expires your session every 24 hours a 7-day rental covers your whole sprint.
- Manual vs. automated: For automated testing, rentals are safer because you don’t repurchase a number each run.
Need a number that lasts for days, not minutes? Rent a number for repeated OTPs for 1, 3, 7, or 30 days and stop worrying about code expiry or repeat purchases.
What NOT to Use Temporary Numbers For Legality & Compliance
Temporary numbers are tools for privacy, testing, and trials; they’re not for fraud, spam, or evading terms of service. Using temp numbers to create fake accounts for abuse, bypass bans on platforms you’ve been kicked off, or run illegal verification rings is prohibited and can get your Frizza account suspended. Always follow the target app’s terms of service and your local regulations.
Keep your usage within these ethical boundaries:
- No fraud or spam: Don’t use temp numbers to create accounts for spamming, scamming, or other illegal activities.
- No ban evasion: If you were banned from a service, using a temp number to get back in violates that platform’s terms.
- No identity fraud: Don’t use temp numbers to impersonate someone or bypass KYC requirements.
- Respect app terms: Some apps explicitly prohibit virtual numbers for verification; check before you rely on this method.
- Stay within legal bounds: Ensure your use case complies with both the platform’s terms and your jurisdiction’s phone/telecom regulations.
PVAPins is not affiliated with any app or website. Please follow each app’s terms and local regulations.
Troubleshooting Checklist: 10 Things to Verify If OTP Still Fails
If you’ve tried everything and Frizza still rejects the code, run through this final checklist if all ten checks pass and the code still fails, the issue is on Frizza’s backend, and you should contact support. This checklist covers session state, number validity, SMS integrity, and timing, leaving no stone unturned. Keep this list handy; nine times out of ten, you’ll find your answer here.
Run through these checks in order:
- The number is formatted with the correct country code, including the + sign.
- The SMS is from the most recent request, not a previous attempt.
- The full code is entered, including any leading zeros.
- No hidden spaces or newlines in the pasted code.
- You started the Frizza session after requesting the number.
- You haven’t triggered the OTP more than once in 30 seconds.
- The code hasn’t expired (check the timestamp in the SMS).
- You haven’t used the same number with a different app at the same time.
- The number’s rental or one-time window hasn’t expired mid-verification.
- Your Frizza API token (if using the API) has the correct permissions.
If you’re still stuck, check the PVAPins blog for more guides or consider switching to a number with a higher success rate for your target app via PVAPins services.
Key Takeaways
- Frizza’s wrong OTP error is almost always caused by expired codes, session mismatches, or SMS truncation not your typing.
- To fix it manually, request a fresh code, enter it immediately, and avoid triggering multiple requests in a row.
- For developers, the API integration eliminates manual errors by allowing programmatic OTP retrieval and polling.
- If the code still fails after troubleshooting, the issue is on Frizza’s backend contact support.
- Always stay compliant: use temporary numbers for legitimate testing and privacy, never for fraud or ban evasion.
FAQ
Why does Frizza keep saying my OTP is wrong even though I typed it correctly?
The most common causes are an expired code, a mismatch between the code sent and the session you’re validating, or your carrier truncating the code. Request a fresh code and enter it immediately; if that fails, log out completely and restart the session.
What’s the difference between a one-time number and a rental number?
A one-time number gives you a single SMS for a single verification, while a rental number (1, 3, 7, or 30 days) lets you receive multiple OTPs on the same number over time. Rentals are more cost-effective if you need repeated verification codes and check rental plans for options.
What should I NOT use a temporary number for?
Never use temporary numbers for illegal activities, fraud, spam, market manipulation, or evading bans. Also avoid using them to bypass KYC requirements or impersonate other people. If the target app’s terms prohibit virtual numbers, respect that rule.
How do I troubleshoot a Frizza OTP that fails on the first try?
Start by requesting a new code and entering it immediately. If it still fails, clear your session, check for SMS truncation, and ensure the number’s window is active. Consult the troubleshooting checklist in this guide for the full 10-point process.
Can I automate Frizza OTP retrieval entirely?
Yes, Frizza’s developer API allows you to request a number, poll for the incoming SMS, and extract the OTP programmatically. This eliminates human error and is the most reliable way to avoid wrong OTP issues. Visit pvapins.com/api_integrate for API documentation.
Compliance Note: PVAPins is not affiliated with any app or website. Please follow each app’s terms and local regulations.
Also Helpful: The same privacy-friendly tricks work across platforms. See our guide on Freelancer Keeps Saying Wrong OTP if you use multiple inboxes.

